More than 8,300 Gitea instances found on the Internet have not yet been patched against a critical security flaw used in ongoing remote code execution attacks, according to cybersecurity watchdog Shadowserver.
The code injection vulnerability (CVE-2026-60004), the target of these attacks was Salesforce security researcher Shai Rodd reportsand allows authenticated attackers to execute arbitrary shell commands with the privileges of the Gitea service account by sending malicious patches via the diffpatch API endpoint.
While successful exploitation requires write repository access to repositories hosted on vulnerable servers, Gitea comes with self-registration enabled by default, allowing unauthenticated attackers to register an account, create a new repository, and trigger the vulnerability without prior credentials.
“Gitea’s diffpatch endpoint can be abused to install and execute a Git hook from content controlled by a repository. An attacker with simple write access to a repository can execute arbitrary shell commands as a Gitea OS user,” The Gitea security team explains. “With registration open by default, an unauthenticated visitor can gain the necessary write access by registering an account and creating a repository.”
Guidance version 1.27.1 released on July 27 to address CVE-2026-60004 and advised users to upgrade their servers as soon as possible.
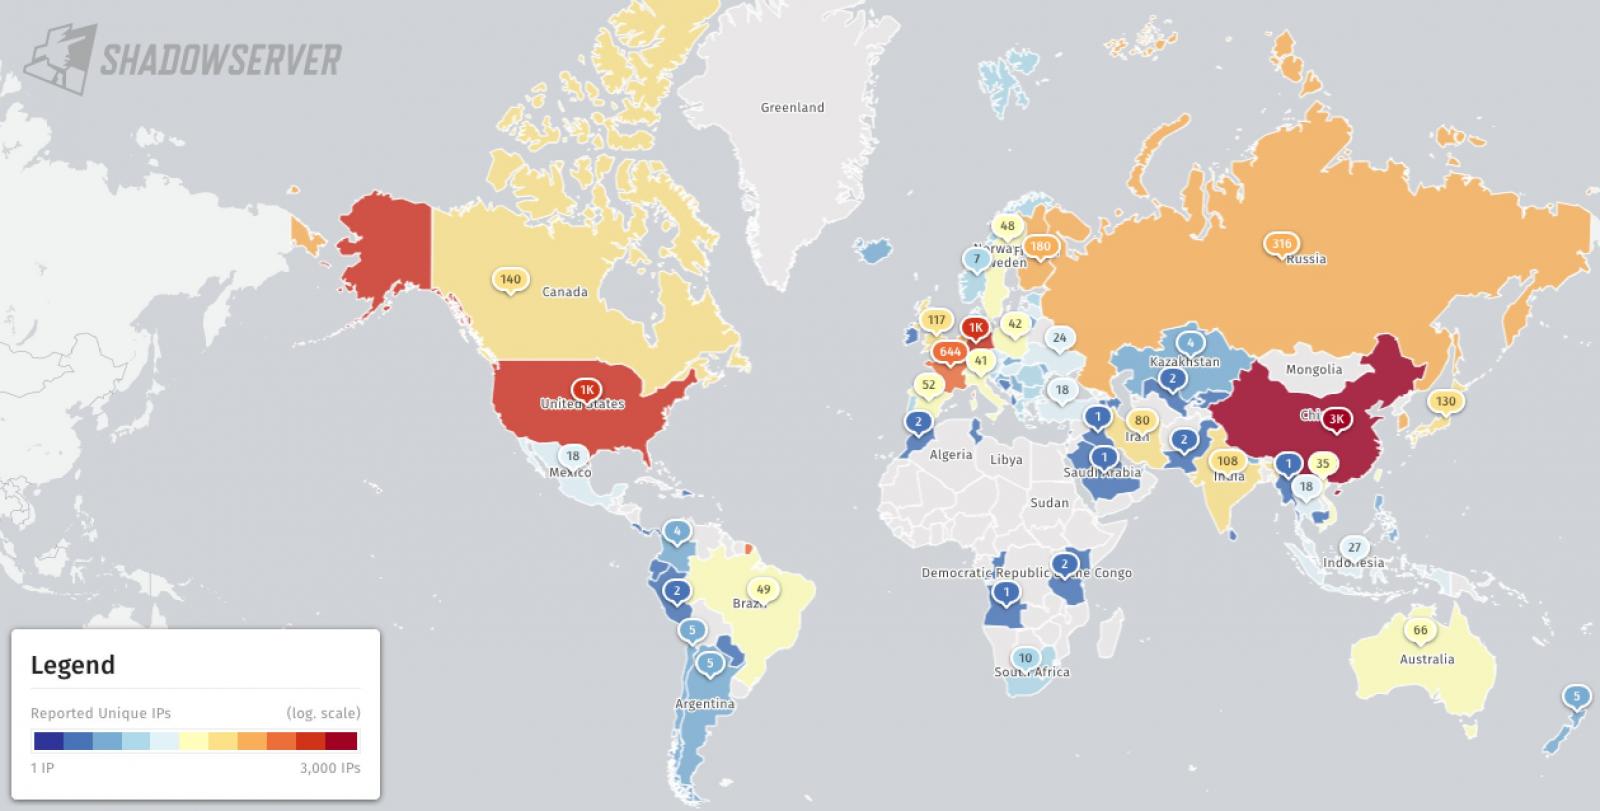
On Friday, the Internet security watchdog group Shadowserver warned that nearly 8400 Gitea servers exposed online are still unprotected and remain vulnerable to ongoing attacks.
“We are scanning/reporting Gitea instances vulnerable to CVE-2026-60004 (code injection) with 8393 IP addresses found vulnerable on 2026-08-27.” Shadowserver said.
On Tuesday, the US Cybersecurity and Infrastructure Security Agency (CISA) also added the vulnerability to its catalog of actively exploited flaws and directed US Federal Civilian Enforcement Branch (FCEB) agencies to repair their servers within three days, by August 28, as required by Binding Operating Directive (BOD) 26-04.
While the cybersecurity agency has yet to share further details about the attacks targeting this flaw, the move was likely prompted by reports of an exploit in the wild where attackers deploy cryptocurrency mining malware on unpatched Gitea servers.
“This type of vulnerability is a common attack vector for malicious cyber actors and poses significant risks to the federal enterprise,” CISA warned.
In July, threat actors were also seen abusing another critical vulnerability (CVE-2026-20896) in the official Gitea Docker image, an authentication bypass flaw affecting Gitea instances with reverse proxy authentication headers enabled.
Gitea is a self-hosted alternative to cloud-hosted GitHub, GitLab, and Bitbucket code hosting and DevOps platforms, with more than 400,000 installations and nearly 1,500 contributors.

Generic prevention scores can hide what happens after initial access. Once attackers use valid credentials, prevention plummets.
The 2026 Blue Report measures security techniques by techniques in 338 million simulations run in customer production environments.



