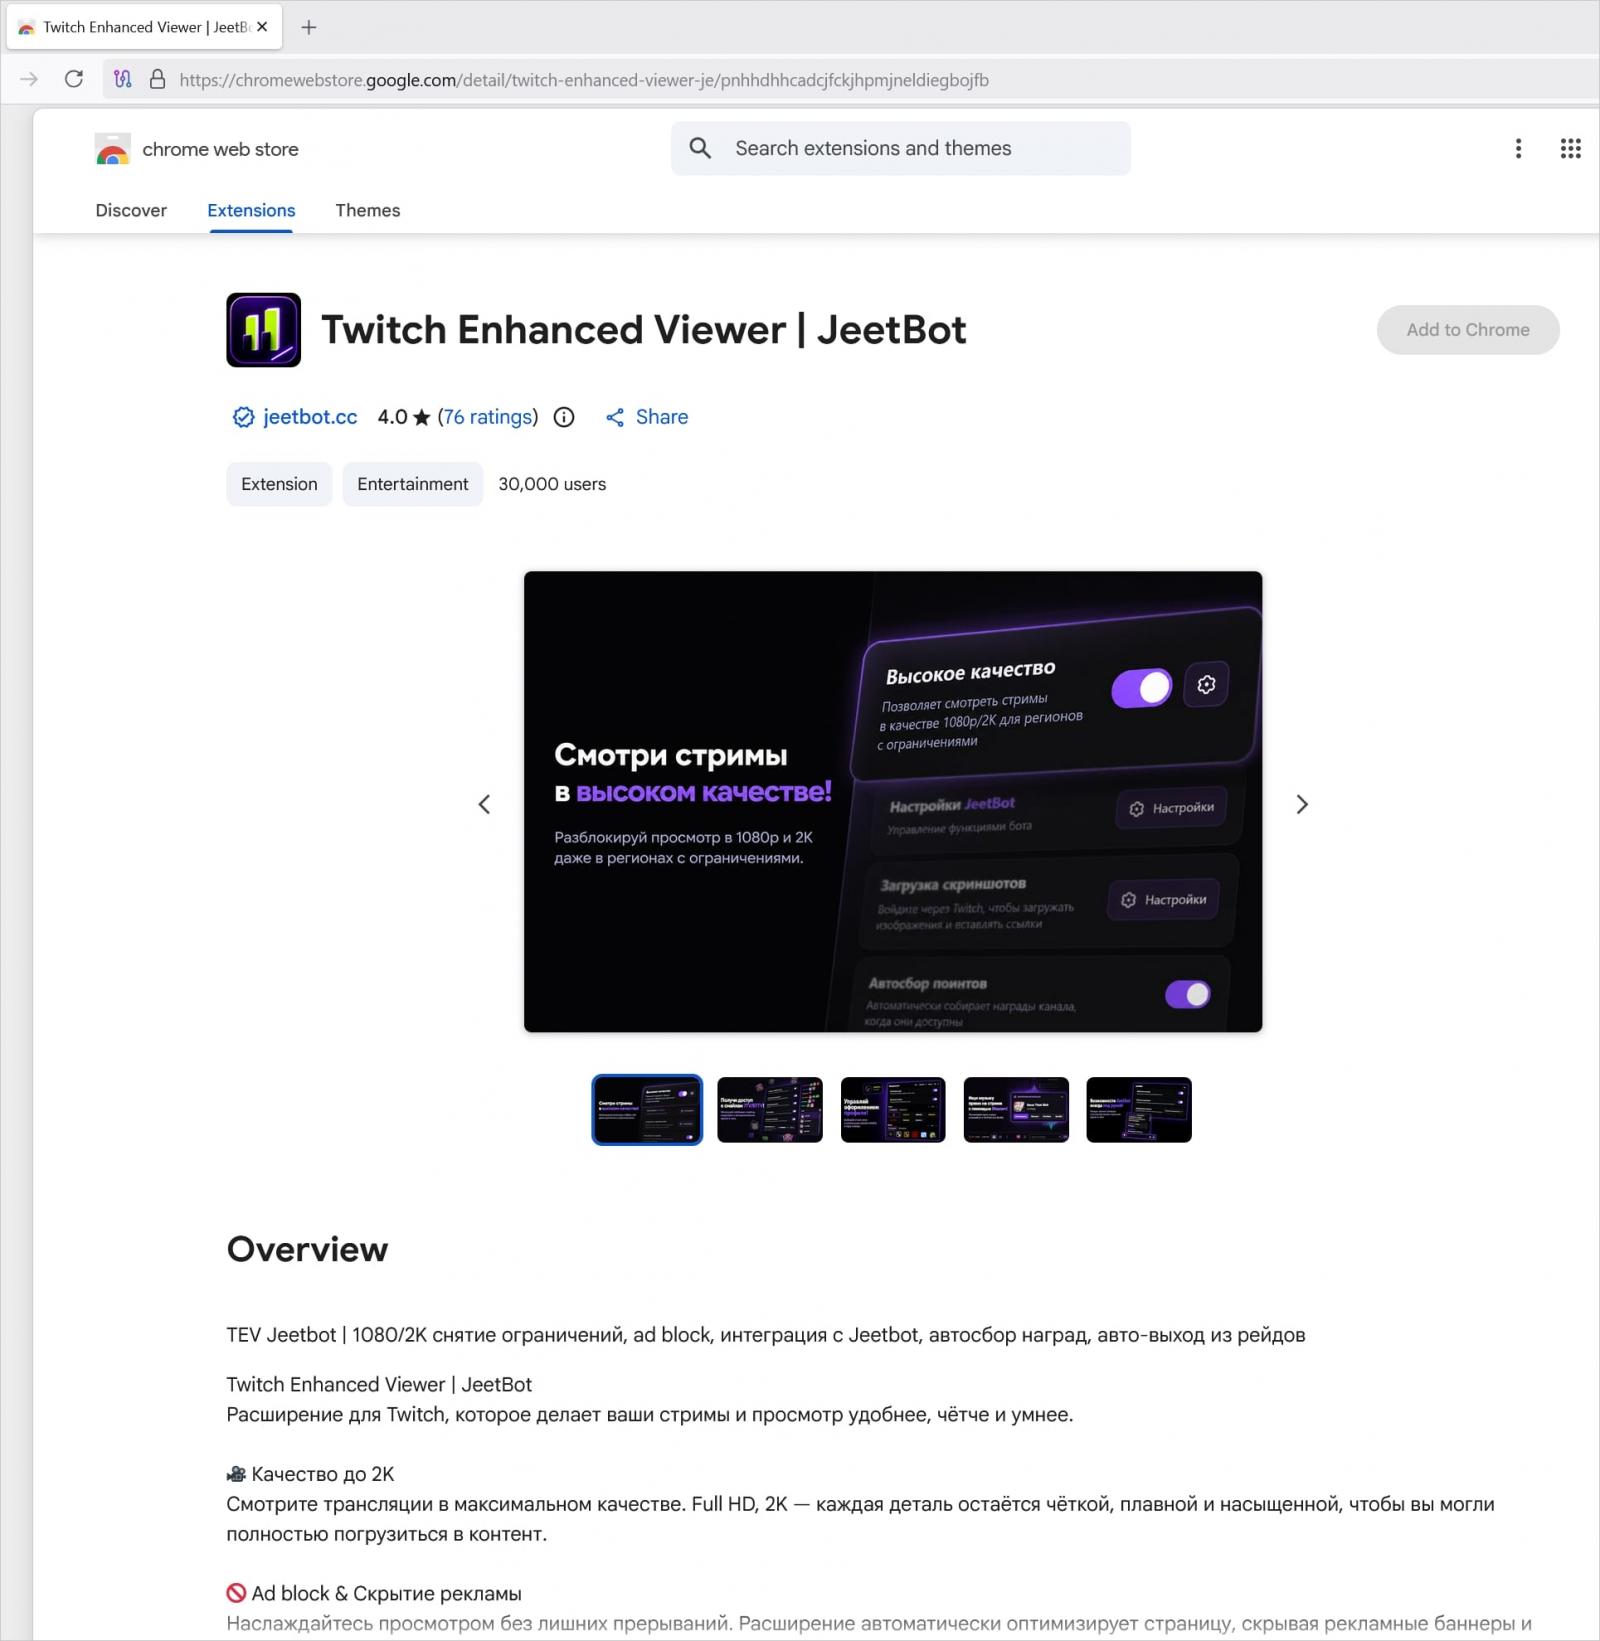
A browser extension called Twitch Enhanced Viewer | JeetBot, available in the official Chrome and Firefox stores, sends users’ Twitch OAuth session tokens to a commercial bot service.
The extension has more than 30,000 installs and is promoted as a legitimate third-party tool for Twitch that can block ads, force playback in 1080p (Full HD), bypass region restrictions, and enable channel points collection.
However, an analysis by application security company Socket shows that the extension captures the authorization header used by the Twitch web client, extracts the user’s OAuth token, and sends the credentials through proxy servers.
The servers are operated by JeetBot, a commercial Russian-language streaming and chatbot service that offers tools for Twitch, Kick and VK Live.
In current versions of the extension, the token is appended directly to redirected proxy requests auth= URL Parameter that ends up in the proxy server’s request logs, where the software provider can easily retrieve it.
“If the extension redirects the video playlist request from Twitch (to usher.ttvnw(.)net) via this proxy the token is appended as an &auth= query parameter.” Socket says.
“Because the token is placed in the URL query string, it is written to the proxy server’s request logs in plain text.”
This process occurs for each Twitch channel that the user views, except for a set of ten Russian-language channels that are hardcoded in the extension’s code.
Source: BleepingComputer.com
Socket emphasizes that previous versions of the extension included more explicit credential stealing mechanisms.
In the description of the product in the Firefox add-ons store, the developer provided a disclaimer about the mechanism used previously, saying:
“Previous versions of the extension transmit your OAuth Twitch token to our server. This is necessary for the stream to run in 1080/1440p.” (machine translated)
The privacy policy for the Chrome version of Twitch Enhanced Viewer | JeetBot says its developer “has disclosed that it will not collect or use your data.”
The statement covers the sale of user data to third parties, except in authorized cases, disclosure for reasons outside the “core functionality” of the product, or “for credit assessment or credit purposes.”
At the time of publication, the extension was still present in both the Chrome Web Store and the Firefox Add-Ons Store.
BleepingComputer sent JeetBot a request for additional information to the email address listed in the Chrome Web Store, but we have not received a response via publication.
Socket researchers believe the extension poses a security risk and recommend users remove it from their browsers, disconnect all sessions on Twitch, and then re-authenticate to invalidate any tokens that may have been forwarded.
Developers are recommended to avoid forwarding requests with authentication headers or tokens through third-party servers.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL and Atlassian for a two-hour digital summit to learn what attacks are changing at AI speed, what defenders should give up, and how to validate, decide, fix and re-validate at machine speed.