Cisco warned customers to patch a critical zero-day vulnerability in the Secure Email Gateway that threat actors have exploited in attacks.
“In September 2026, Cisco PSIRT became aware of active exploitation of this vulnerability,” the company said warned in a security advisory on Monday.
The vulnerability (tracked as CVE-2026-76461) was found during email parsing of the Cisco AsyncOS Software for Cisco Secure Email Gateway and affects virtual and physical appliances, regardless of device configuration.
A successful exploitation could allow unauthenticated remote attackers to execute arbitrary commands with root privileges on the underlying operating system.
“This vulnerability is due to insufficient validation in the email parsing logic. An attacker could exploit this vulnerability by sending a crafted email message containing malicious SQL statements via an affected device,” Cisco added. “A successful exploit could allow the attacker to execute arbitrary SQL statements, resulting in command execution with root privileges on the underlying operating system.”
Cisco shared indicators of compromise and recommended network defenders look for suspicious SQL statements in the mail logs of each cluster device.
However, administrators should also check network and firewall logs for signs of suspicious activity (including uploads and downloads to and from external or malicious IP addresses), as attackers may remove evidence of exploitation.
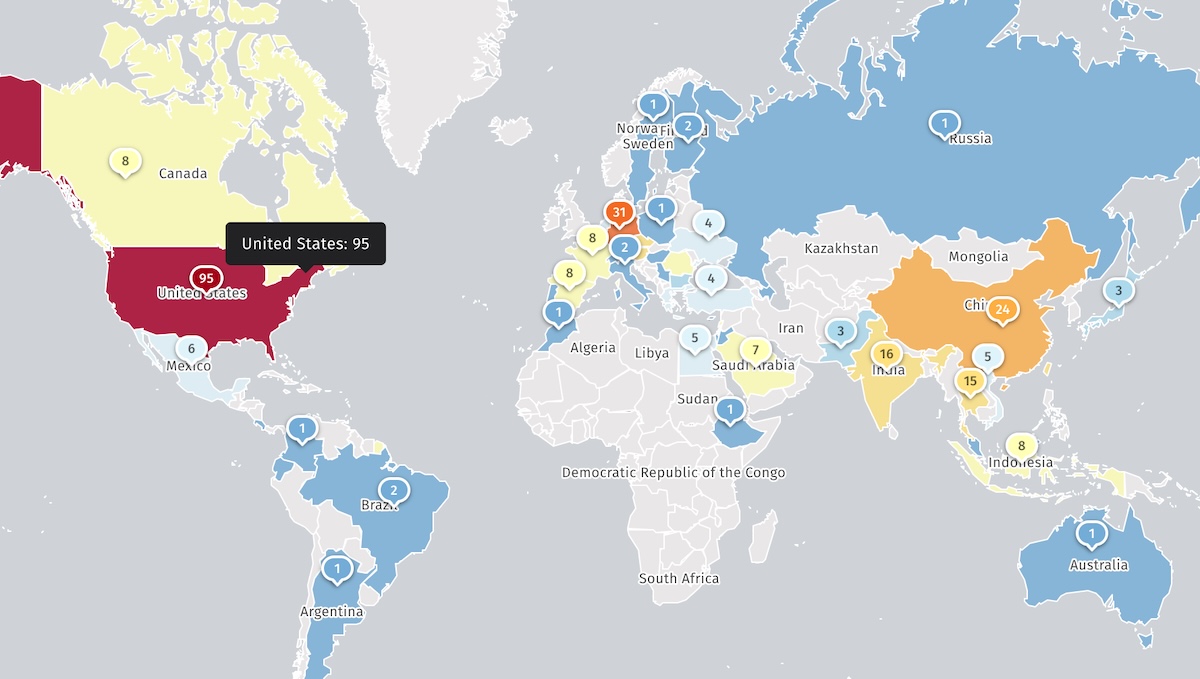
Internet security guard Shadowserver Currently tracks over 400 Cisco Secure Email Gateway appliancesHowever, there is no information about how many are honeypots or how many are already secured against attacks.
Also the Cybersecurity and Infrastructure Security Agency (CISA). added the bug CVE-2026-76461 Catalog of known exploited vulnerabilities (KEV) on Mondayby instructing federal authorities to patch their systems within three days, i.e. by September 17th.
Cisco spoke on Monday four additional critical vulnerabilities (CVE-2026-76440, CVE-2026-76441, CVE-2026-20353, and CVE-2026-76443) affect the Secure Email Gateway (SEG) and Secure Email and Web Manager (SEWM) appliances regardless of configuration, but stated that there is no evidence that they have been exploited in the wild.
In January, the company also patched a Cisco AsyncOS maximum severity flaw (CVE-2025-20393), which has been exploited in zero-day attacks on SEG and SEWM devices since November 2025.
Recently, Cisco announced that three different ransomware and state-sponsored threat groups exploited two recently fixed vulnerabilities in the Secure Firewall Management Center (FMC).
As of November 2021, CISA 98 Cisco vulnerabilities reported as being actively exploited in attacks, including seven exploited by ransomware gangs.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL and Atlassian for a two-hour digital summit to learn what attacks are changing at AI speed, what defenders should give up, and how to validate, decide, fix and re-validate at machine speed.