A massive cybercrime is exploiting thousands of compromised small business websites to deliver ClickFix payloads stored in smart contracts on the BNB Smart Chain (BSC).
In recent months, researchers identified more than 5,400 hacked websites, most of them based on WordPress and PrestaShop.
The original compromise method remains unknown, but each site was injected with a script that receives the next-stage payload from a smart contract on the BSC testnet endpoint, a technique known as EtherHiding.
Researchers at cloud security platform Netskope explain that the BSC testnet is designed for developers and works similarly to the mainnet, the production blockchain, but is available for free.
Threat actors use the EtherHiding technique to store malicious code or configuration data in blockchain smart contracts, providing a robust infrastructure that is difficult to destroy.
In the supply chain observed by Netskope, the script displays a ClickFix decoy that displays a fake CAPTCHA and instructs visitors to open the Windows Run dialog box and paste a PowerShell command.
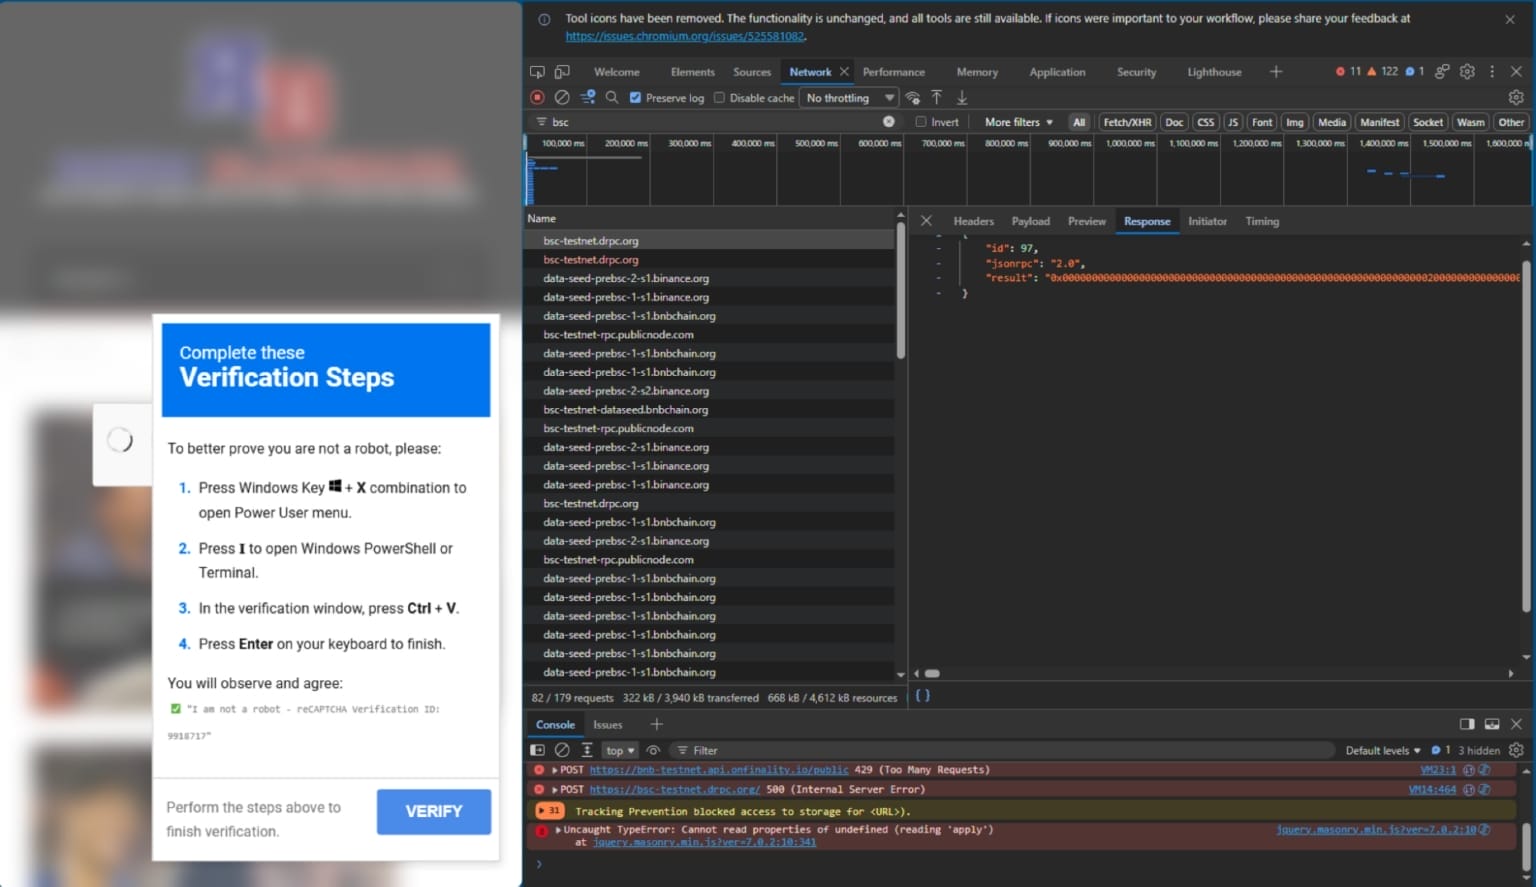
Source: Netskope
This downloads the final payload to the machine and executes it. Since the attacker stores the payload in a smart contract, he can change it at any time.
The researchers note that later in the campaign, the threat actor replaced the ClickFix payload in the smart contract with a WebRTC data channel stager.
In the newer variant, the payload sets up a covert encrypted channel to the attacker and executes the received code.
“The script creates a peer connection and a data channel and then generates the required session description offer like a normal WebRTC handshake.” Netskope explains.
“But instead of sending this offer somewhere and waiting for a real response, it is writes the answer yourself by hand and feeds it directly back into the connection. In this way, there is no handshake, but a data channel is still opened to the cyber attacker.”
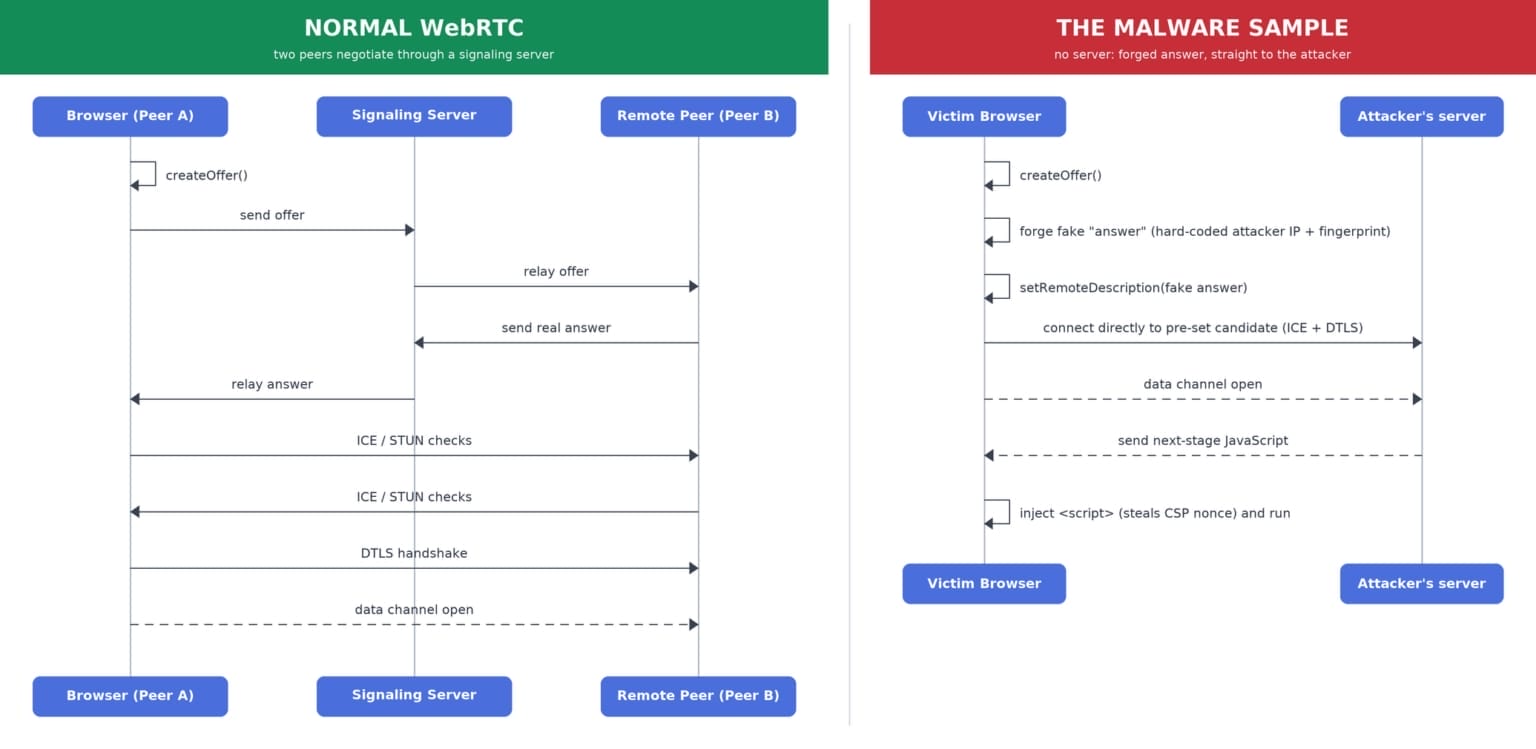
The stager receives JavaScript code from the hard-coded command and control address (C2), buffers it, and executes it when the channel is closed or after ten seconds.
The received code is assembled in browser memory and executed dynamically without saving to disk by adding it to the head of the DOM
Netskope warns that the operation uses more than 300 infected websites every day. Since the spring, the number of compromised websites contacting BSC Testnet RPC endpoints has steadily increased.
Telemetry data shows that nearly 400 websites called the endpoint daily in August, with a record high of 536.
The security researchers recommend that defenders block the entire pool of BSC Testnet RPC endpoints provided here and monitor non-web UDP traffic associated with WebRTC.

Overall prevention scores can hide what happens after the first access. Once attackers use valid credentials, prevention drops sharply.
The 2026 Blue Report measures defense technology for technology in 338 million simulations conducted in customer production environments.



