A supply chain attack on Android-based car head units uses a legitimate device update app to spread malware that incorporates compromised devices into a proxy botnet or uses them for advertising fraud.
Kaspersky researchers analyzed the malware and attributed the operation to the MoYu group, a threat actor previously linked to the BadBox malware botnet.
The researchers note that this is the first documented case of a malware infection chain created specifically to target the car’s head unit.
MoYu’s operation targets systems from DoFun, a Chinese automotive software and hardware provider owned by Shenzhen Driving Control Technology Co., Ltd.
DoFun is an automotive software, cloud services and hardware provider that sells generic drugs Android based head unitswhich act as a command center for a car’s infotainment, navigation and settings systems.
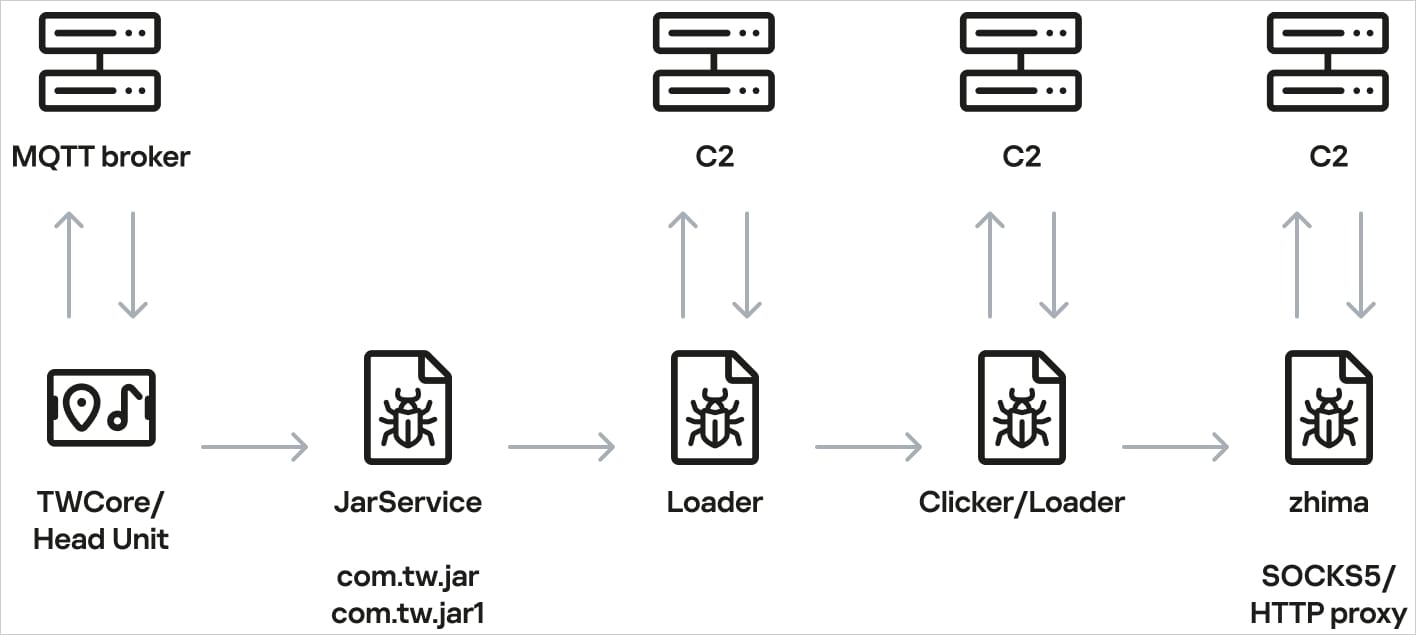
In June, Kaspersky researchers found a fraudulent APK file downloaded from a legitimate DoFun system app, TWCore, which receives instructions through an MQTT server hosted at cardoor(.)cn.
The unknown app has no interface and is a malware called JarService. When launched, the malware decrypts and runs a second-stage loader, which establishes communication with a command-and-control (C2) server and downloads another encrypted payload.
The final payload periodically reports device information such as model, screen resolution, Wi-Fi SSID and MAC address and retrieves commands from the attackers.
The malware supports the following nine commands:
- return – Retrieves a specified value from Android’s SharedPreferences store
- copy – Copies saved or downloaded content to the device clipboard
- http – Sends HTTP GET or POST requests and can store part of the response
- Web – Opens a URL in a WebView and runs the provided JavaScript
- Loadlib – Not fully implemented at the time Kaspersky published the report
- Loadlib2 – Downloads and runs any code or additional modules
- Loadlib3 – Not fully implemented at the time Kaspersky published the report
- Deeplink – Opens a specified resource in the browser
- trace route – Checks whether specified hosts can be reached via ICMP ping
Kaspersky says the malware does not interfere with driving or critical vehicle control systems and appears to be designed for advertising fraud and converting internet-connected car head units into residential proxy nodes for monetization purposes.
Source: Kaspersky
Researchers found that the operator primarily loaded a reverse proxy module called “zhima,” which turns the main entity into a proxy botnet node, and also made web requests for click fraud activities.
Kaspersky says It informed DoFun of its findings and the Chinese company responded that it had resolved the issue.
BleepingComputer has contacted both companies with questions about the original compromise vector and we will update the article with the information as soon as we receive it.

Overall prevention scores can hide what happens after the first access. Once attackers use valid credentials, prevention drops sharply.
The 2026 Blue Report measures defense technology for technology in 338 million simulations conducted in customer production environments.



