Phishing actors abuse the legitimate endpoint management platform Faronics Deploy to remotely gain administrative control of victims’ computers and install ScreenConnect remote support software.
In activity observed between July 21 and August 20, Faronics-themed decoys reached more than 457 endpoints via emails disguised as invoices, tax documents or other business files.
Faronics Deploy is a cloud-based endpoint management platform that enables IT administrators to remotely enroll and manage computers, deploy software, and run scripts.
Researchers at managed detection and response (MDR) company Huntress say the embedded malicious links lead to a website that profiles potential targets and funnels them through a malicious download flow.
If the website is accessed from an analysis environment, a deceptive routine is activated, for example by displaying an error message.
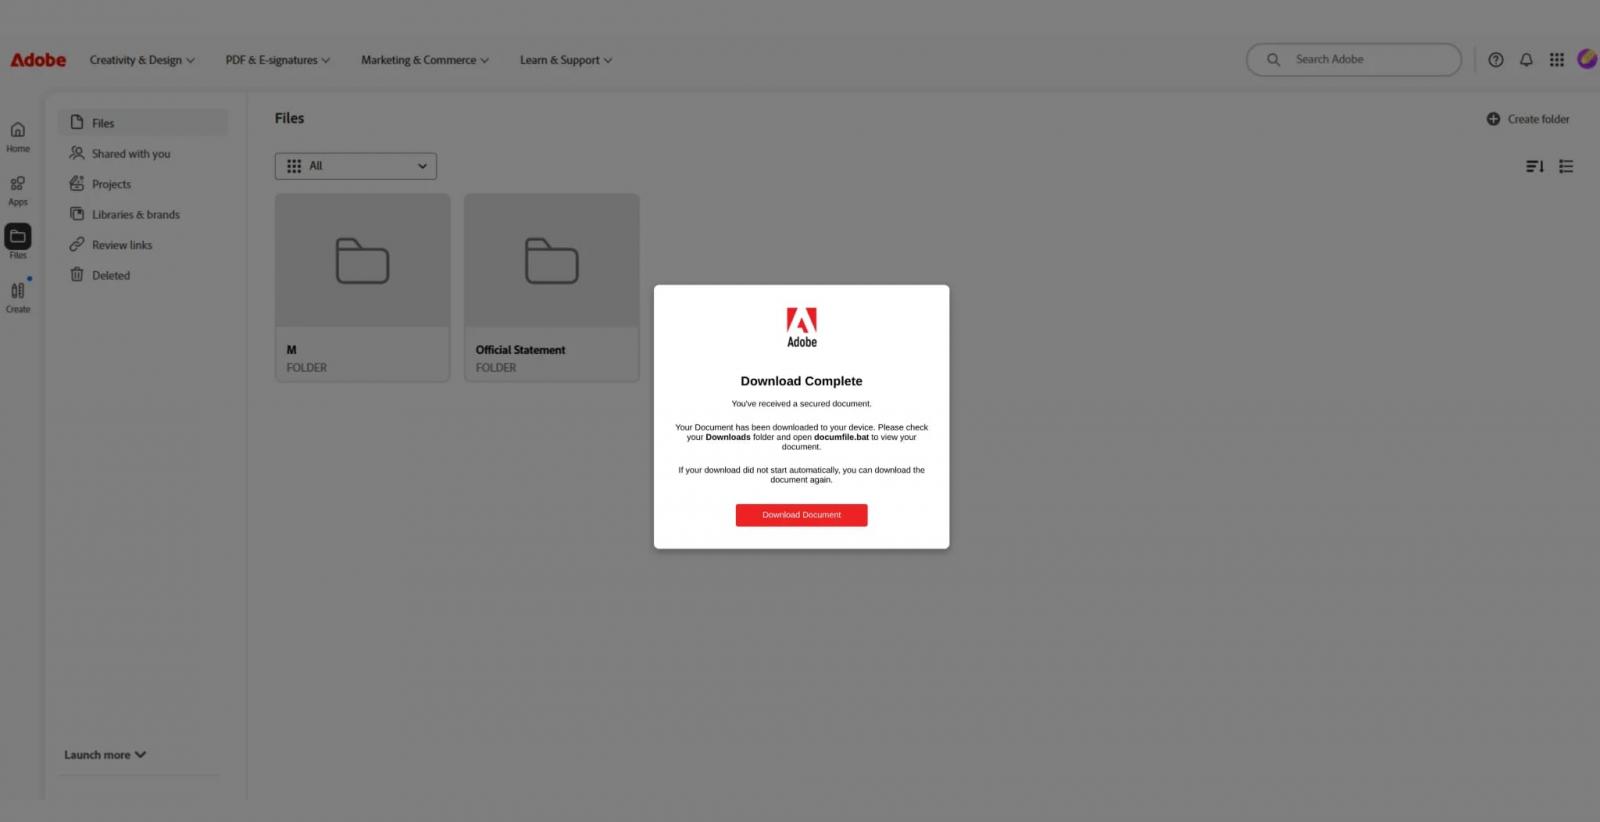
Huntress explains that a potential victim is asked to download and launch a legitimate, signed Faronics Deploy installer disguised as an Adobe document, reader app, or plugin update.
Source: Huntress
When the victim runs the Faronics installer, often called “Adobe.exe,” their computer is registered to a Faronics deployment controlled by the attackers.
The threat actor then uses Faronics’ remote deployment feature to execute PowerShell scripts on the registered computer without further user interaction.
These scripts download additional tools from the attacker’s infrastructure or external locations, including GitHub, and ultimately install another legitimate remote access tool, ConnectWise ScreenConnect.
“The delivery method varies depending on the script, with observed examples using Curl or MSHTA to retrieve additional content, while others call Msiexec to deploy payloads hosted on attacker-controlled infrastructure.” says Huntress.
“These scripts are then used to install ScreenConnect, establishing an additional remote access mechanism on the compromised endpoint.”
ScreenConnect provides attackers with an additional remote access channel independent of Faronics, enabling convenient remote control more suitable for interactive access, while also serving as redundancy when the malicious Faronics deployment is identified and terminated or when defenders remove their agent.
Huntress notified Faronics of its findings on August 5, and the vendor acknowledged the malicious activity it observed and addressed it by implementing additional anti-abuse measures.
In addition, Faronics has contacted affected organizations to inform them of possible compromises.
According to Huntress, malicious activity decreased significantly starting August 21, indicating that Faronics’ measures were working.
Huntress recommends administrators check the C:\ProgramData\Faronics\Logs\ location for a ScriptRunner.log file, which may preserve remotely executed script names and download URLs.
The company says the ck parameter in Faronics configuration requests is also an indicator because it identifies the associated customer deployment and can help identify compromised endpoints or malicious accounts.
Administrators should also check for ScreenConnect installations where it is not typically deployed.

Overall prevention scores can hide what happens after the first access. Once attackers use valid credentials, prevention drops sharply.
The 2026 Blue Report measures defense technology for technology in 338 million simulations conducted in customer production environments.



