Akira’s ransomware partner disables the endpoint detection and response (EDR) solution on a compromised system by restarting the machine in safe mode with networking.
The attack occurred on August 4 after the hacker gained initial access through an exposed SonicWall VPN device without multi-factor authentication (MFA).
Managed detection and response (MDR) services company Huntress says that approximately two hours after a successful VPN login, the attacker connects to the domain controller via RDP, enumerates Active Directory users and computers, and then moves to an application server.
They used WinRAR to archive mapped file shares and s5cmd command-line tool to upload the stolen data to an S3 container controlled by an attacker before installing AnyDesk for remote access.
At this point, the attacker uses AnyDesk to force the compromised host to boot into Safe Mode with Networking and disable both the Huntress agent and Microsoft Defender real-time protection.
Safe Mode is a Windows startup state designed for troubleshooting and diagnostic operations. It starts Windows with a limited set of drivers and services, which usually prevents most third-party software and services from loading.
For 10 minutes while in safe mode, “the host had no working EDR and the AV was blinded,” Huntress says.
Meanwhile, the attackers added AnyDesk to the Windows registry in safe mode, allowing it to run after a reboot and retain its remote access to the breached machine.
However, when they tried to run the main ransomware payload (akira.exe) through AnyDesk in safe mode, it failed because the system reported low virtual memory and generated out-of-memory and PowerShell errors.
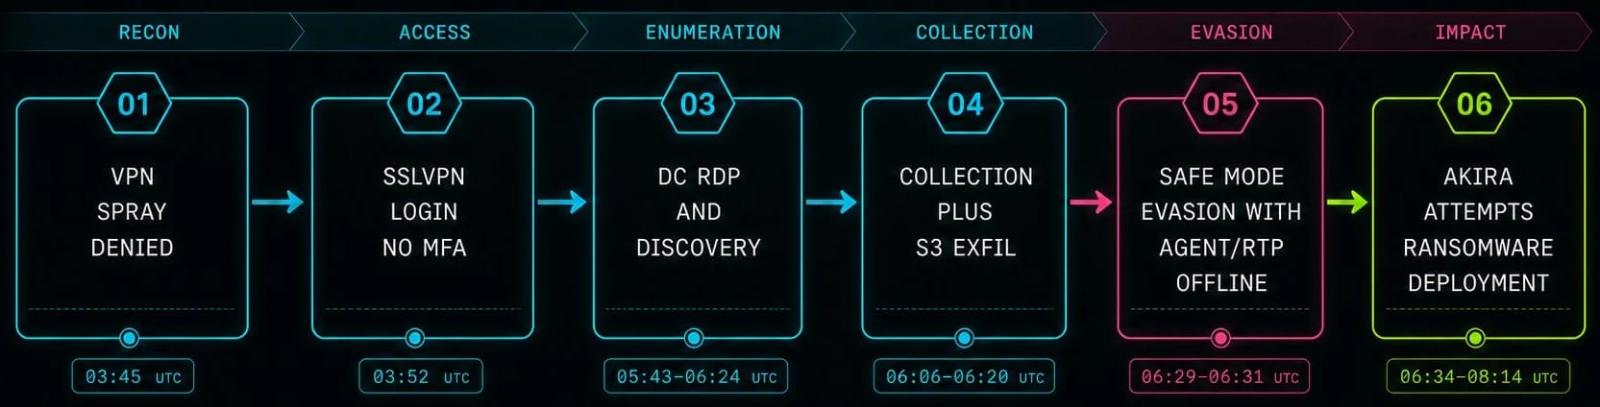
Source: Huntress
A scheduled Defender scan eventually found the Akira executable even if real-time protection was disabled in safe mode, but the security tool was unable to remove it while the machine remained in that mode.
Defender quarantined the file only after the attacker restarted the system in normal mode, which restored real-time protection.
Despite failing to encrypt the files, the Akira operator was still able to steal credentials and extortion files, all within less than five hours of initial access.
Huntress notes that other ransomware families, such as Snatch and AvosLocker, have used this tactic for years, but this incident marks the first time the company has observed it in an Akira attack.
The researchers recommend adding MFA to all VPN accounts, putting measures in place to detect credential spewing and monitoring for changes to the safe mode boot configuration, or adding tools to remotely access the safe mode service registry.

Generic prevention scores can hide what happens after initial access. Once attackers use valid credentials, prevention plummets.
The 2026 Blue Report measures security techniques by techniques in 338 million simulations run in customer production environments.



