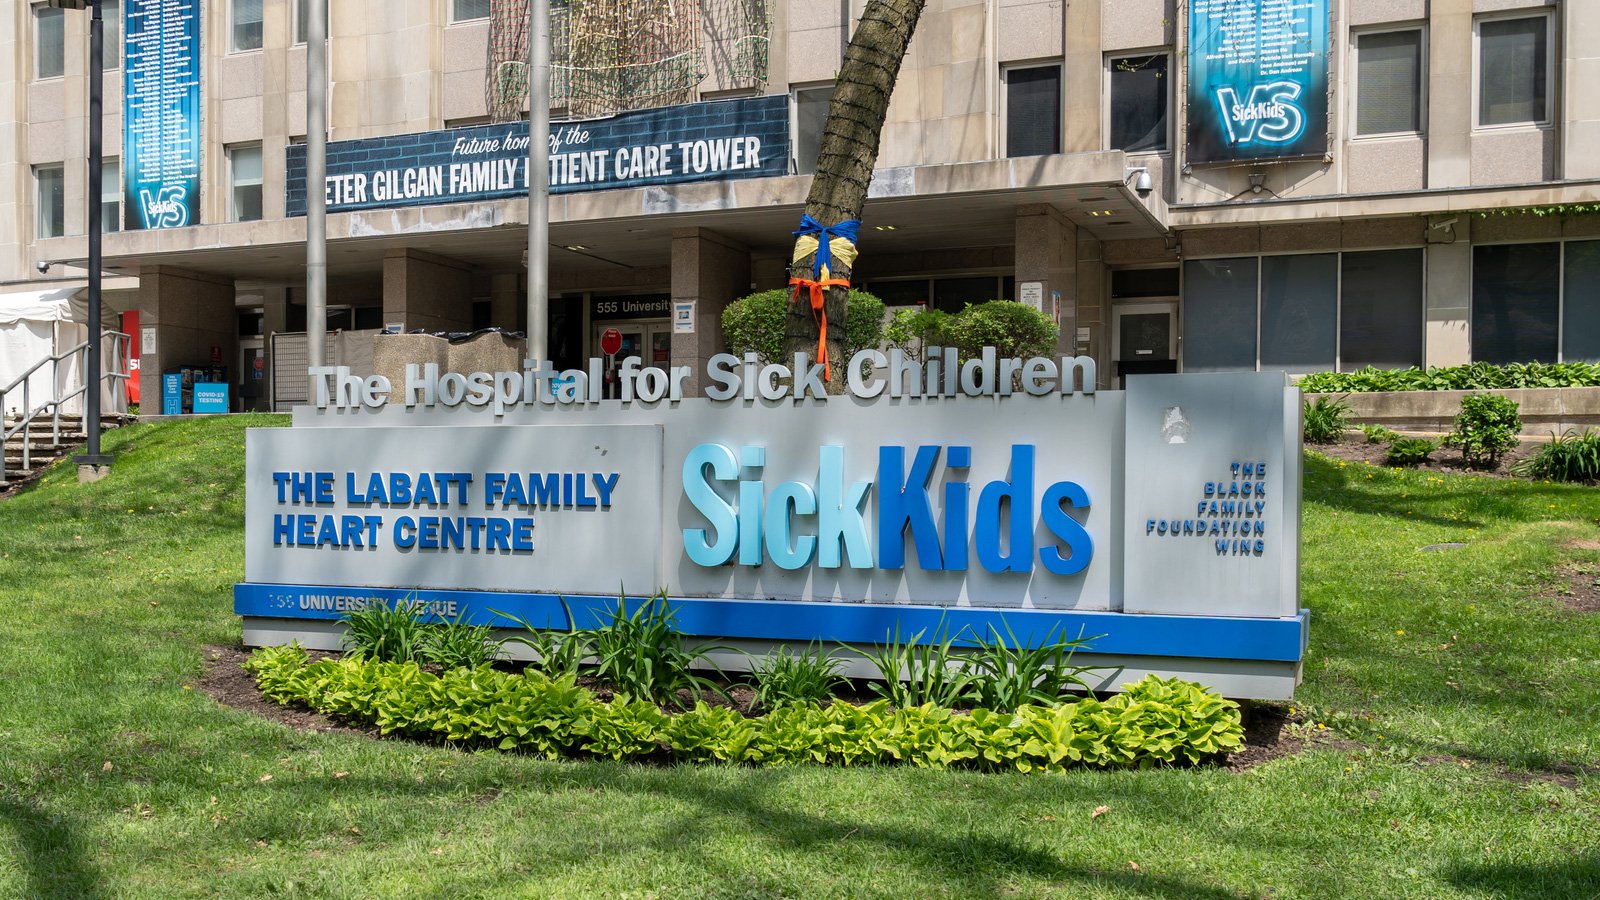
The Hospital for Sick Children (SickKids) has announced that the personal information of some current and former employees and applicants was exposed in a “cybersecurity incident.” The hospital says the breach was due to a bug in third-party software.
Toronto Children’s Hospital said clinical systems and patient records remained unaffected, but its publicly accessible careers website was temporarily taken offline.
Career page restored, scope of incident under review
SickKids disclosed the incident this week, saying it resulted in unauthorized access to employee data.
The hospital attributed the breach to a vulnerability in a third-party software application that it said was used by SickKids and other organizations, one said Media statement.
The language appears to indicate that there is a broader campaign against users of the same product, although the hospital did not name the vendor, application or CVE involved.
The external careers website was temporarily affected and has “now been safely restored,” according to the statement.
Clinical systems and patient information were not affected and patient care continued as usual, says SickKids.
After learning of the incident, the hospital launched an investigation with the help of outside cybersecurity experts.
The findings indicate that personal information may have been disclosed by current and former employees of SickKids, Boomerang (a children’s hospital operated by SickKids), and the SickKids Foundation, as well as SickKids job applicants.
The hospital did not say what categories of data were involved, how many people were affected or when the procedure took place.
The review of the affected information is not yet complete. People confirmed to be affected will be notified directly.
Meanwhile, SickKids says it has issued an abundance of caution to anyone who may be involved in the incident and is offering free credit monitoring and identity protection for 24 months.
Application portals are an unusually fertile target for data thieves. Applicants routinely provide full names, home addresses, telephone numbers, employment histories and, in some jurisdictions, government identifiers. This information is useful for both identity fraud and for building convincing social engineering pretexts against hospital staff.
A repeat goal
This is not the first publicly known security incident to hit the hospital in recent years.
In December 2022, SickKids was hit by a ransomware attack that crippled internal systems, hospital phone lines, and website, causing delays in lab and imaging results.
The LockBit ransomware gang subsequently apologized in a rare public apology, saying the responsible affiliate had violated its rules against medical facility encryption and handing over a free decryptor, but only after the hospital had spent nearly two weeks restoring the systems itself.
In September 2023, SickKids was among Ontario healthcare providers affected by a breach involving a third-party organization with which the company shares perinatal and child health data. This incident, which resulted from the mass exploitation of the MOVEit Transfer Zero-Day (CVE-2023-34362), exposed information about 3.4 million people, including names, home addresses, dates of birth, and health card numbers.
Healthcare remains one of the most targeted sectors for both ransomware teams and data extortion groups.
Children’s hospitals in particular have decades of confidential records, which continues to make them attractive to attackers, regardless of the ethics that criminal organizations claim to adhere to.

Overall prevention scores can hide what happens after the first access. Once attackers use valid credentials, prevention drops sharply.
The 2026 Blue Report measures defense technology for technology in 338 million simulations conducted in customer production environments.



