Data allegedly stolen from Manchester Airports Group (MAG) and leaked online this week includes the email addresses and phone numbers of 8.8 million people.
MAG announced the incident last week, warning that hackers had breached its systems and stolen parking, lounge and fast track booking data as well as airport WiFi logins at Manchester, London Stansted and East Midlands airports.
The airport operator said hackers had exfiltrated email addresses, phone numbers, vehicle registration numbers and postal codes, and noted that its operations had not been affected by the incident.
MAG confirmed that the stolen information was stored in a database hosted by a third party and that the attackers had made a ransom demand, but refrained from revealing further details on the matter.
Over the weekend, the FulcrumSec extortion gang claimed responsibility for the attack and has since released around 550 gigabytes of uncompressed data that was allegedly stolen from MAG.
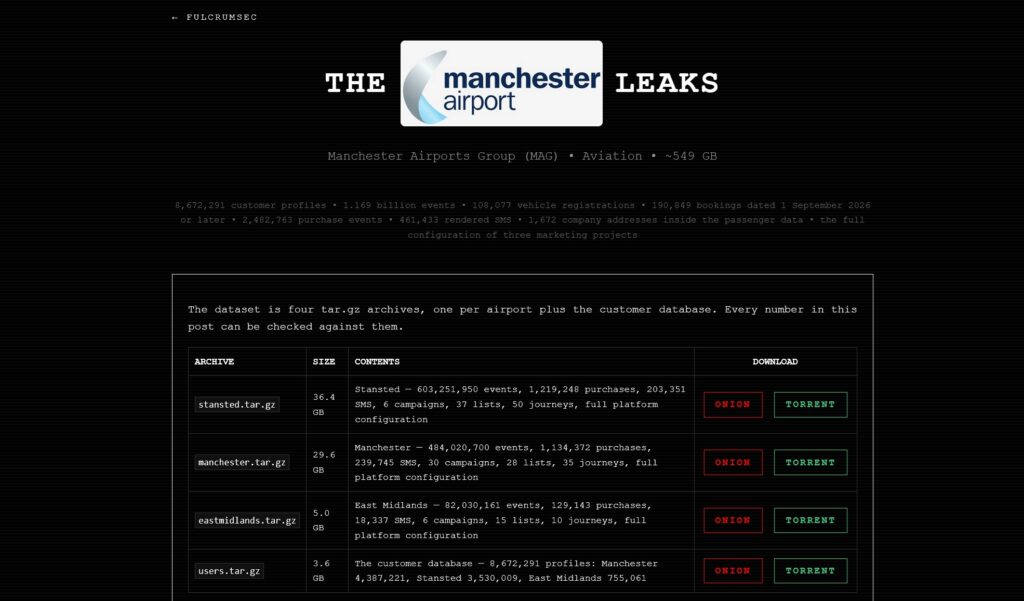
The data includes the personal information of around 8.7 million people, including names, emails, phone numbers, city and postal region, and private IP addresses used to access accounts, according to the group.
There are about 8.8 million email addresses and phone numbers, according to privacy alert site HaveIBeenPwned, which analyzed the dataset and added it to its database were compromised. Names, browser agent details, purchases and vehicle registration numbers were also exposed.
According to FulcrumSec, the stolen data includes 2,482,763 purchases (bookings for parking, lounges and fast track products), 461,433 SMS messages related to bookings, parking and vehicle registrations, and 108,077 unique UK vehicle registration numbers.
Additionally, the extortion group claims to have exfiltrated the configuration of the MAG platform. Safety Week has not independently verified the attackers’ claims.
FulcrumSec says it penetrated MAG’s systems using admin keys that were left “prominently visible in the front-end JavaScript of each of its three airports’ websites” in each root domain.
The extortion group has admitted that MAG did not pay any ransom.
Related: 153 million driver’s license images offered on the Dark Web
Related: Ransomware gang claims Nutex health data breach
Related: 9.5 million people affected by Aesto health data breach
Related: Berlin does not pay blackmail group for data theft



