According to vulnerability intelligence firm Previdian, attackers have begun targeting a critical vulnerability in Citrix NetScaler.
Tracked as CVE-2026-19490This vulnerability could allow unprivileged threat actors to remotely bypass authentication if the NetScaler appliance is configured as a AAA virtual server or as a gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy), depending on the NetScaler firmware version and whether the SAML action is configured.
“We strongly encourage our customers to check out the official NetScaler ADC and NetScaler Gateway Security bulletin“Assess whether your deployments are affected and update affected appliances to the recommended builds as soon as possible,” Citrix warned in mid-August when it patched the bug and urged administrators to fix it as soon as possible.
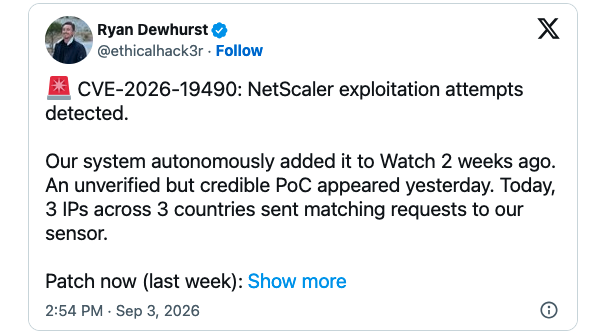
The company has not yet reported the vulnerability as being actively exploited Security notice dated August 19thPrevidian founder and security researcher Ryan Dewhurst told BleepingComputer on Thursday that attackers have begun targeting CVE-2026-19490 in the wild after a “credible” proof-of-concept exploit was published online.
“On September 3rd, one of our NetScaler sensors received requests for PoC from three different source IPs geolocated in Australia, the United States and Germany,” Dewhurst told BleepingComputer.
“Our current assessment is that this provides evidence of attempted exploitation, but does not confirm successful compromise of real systems.”
The Center for Cybersecurity Belgium, the National Center for the Coordination of Cybersecurity in Belgium (NCC-BE), also warned on Friday of exploitation attempts targeting the CVE-2026-19490 vulnerability and urged administrators to prioritize patching all vulnerable Citrix NetScaler appliances on their organizations’ networks.
Although the Internet threat monitor Shadowserver detects this over 22,000 NetScaler ADC devices and almost 1,700 gateways For the instances disclosed online, there is no information about how many are honeypots, have vulnerable configurations, or have already been patched against CVE-2026-19490 attacks.
Citrix asked administrators to fix two additional NetScaler bugs (CVE-2026-3055 And CVE-2026-4368) in March, just days before threat actors began exploiting them for attacks.
The Cybersecurity and Infrastructure Security Agency (CISA) added A week later, the CVE-2026-3055 vulnerability was added to the catalog of actively exploited vulnerabilities and federal authorities were ordered to patch vulnerable Citrix appliances within three days.
Since November 2021, the US cybersecurity agency flagged 23 Citrix vulnerabilities as exploited in the wild, six of which were also exploited by ransomware gangs.

Overall prevention scores can hide what happens after the first access. Once attackers use valid credentials, prevention drops sharply.
The 2026 Blue Report measures defense technology for technology in 338 million simulations conducted in customer production environments.



