Anthropic is warning some Claude users that Infostealer malware has stolen active Claude login sessions on their PCs, allowing attackers to access and abuse accounts.
The company will deregister affected users from Claude, remove stored payment methods, and refund charges that it identifies as unauthorized.
“We recently became aware of a malicious actor using common infostealer malware to steal Claude login sessions from other people’s computers and then using those login sessions to access and exploit Claude accounts,” Anthropic said in an email to an affected user divided it on Reddit.
“If your usage limits looked like they were filling up and then depleting while you weren’t using Claude, this was likely the cause,” Anthropic warned.
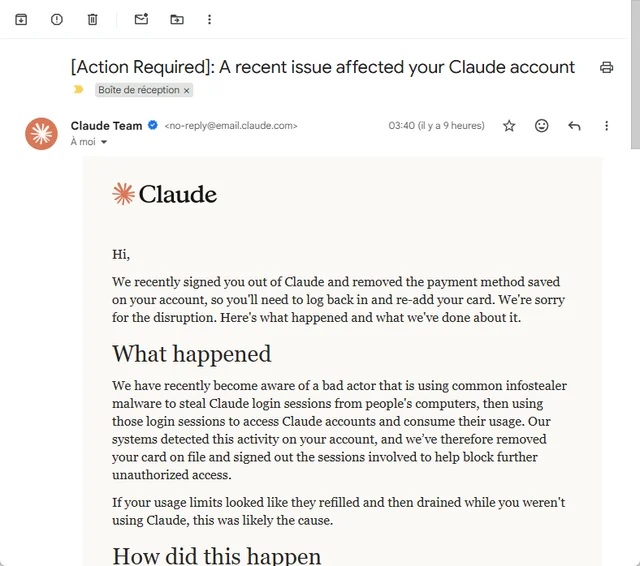
Source: Reddit
It’s also worth noting that infostealers can copy an already authenticated browser session, meaning the attacker may not have to go through the normal password and 2FA login process again.
Anthropic links attacks with Vidar, LummaC2, StealC, RedLine and other infostealers
In the email, which is also being sent to other compromised account holders, Anthropic states that the investigation is ongoing but that the computers are likely already infected with generic Infostealer malware.
“We have no reason to believe that this malware is related to Claude, was installed through Claude, or is related to anything you did with Claude,” the company emphasized.
According to Anthropic, the malware typically arrives via downloads or malicious apps and steals locally stored information, including browser passwords, login cookies and credentials from other apps.
“Your Claude Session was likely one of the many things it collected. It appears that a bad actor has now begun selecting and using the Claude Sessions from what it collected,” Anthropic said.
In this case, the Reddit user who shared the email confirmed that he had downloaded a pirated game, which explains why his system was compromised.
Anthropic has identified several malware, including Vidar, LummaC2, StealC, RedLine and Acreed on Windows, as well as Atomic Stealer (AMOS) on a small number of Macs.
If you are affected, Claude will revoke compromised sessions and remove saved payment methods to prevent unauthorized purchases.
“Logging out of Claude will stop the stolen sessions, but it will not remove the malware,” Anthropic warned. “If it is still on your computer, your next login session could be stolen in the same way.”
Anthropic has urged affected users to take basic security measures, including changing login credentials, revoking other sessions and removing the malware from PCs.

Overall prevention scores can hide what happens after the first access. Once attackers use valid credentials, prevention drops sharply.
The 2026 Blue Report measures defense technology for technology in 338 million simulations conducted in customer production environments.



