A likely Russian-speaking threat actor used hundreds of AI agents to develop and launch a global exploitation campaign targeting vulnerable PaperCut NG/MF servers.
The agents were tasked with creating, testing, and refining exploits for CVE-2026-81578 and CVE-2026-82078. Both vulnerabilities affect PaperCut software and were reported as being actively exploited earlier this month.
GreyNoise, an attack and threat intelligence company, said the campaign began on August 31 and combined OpenAI’s Codex and DeepSeek models with standard offensive tools.
The AI agents also created target lists via internet scanning and discovery platform Netlas.
GreyNoise data suggests that the operation compromised at least 440 PaperCut instances associated with 395 different organizations in 48 countries.
The attacker stole login credentials from 280 victims, obtained operating system or domain secrets from 147, and gained administrative privileges at 12 organizations.
Most victims came from the education sector, accounting for about half of all breaches. The United States was the most affected country, followed by the United Kingdom, France, Spain and Canada.
According to GreyNoise, the threat actor provided a list of countries to avoid, including Russia, China, Iran, Ukraine, Belarus, Moldova, Brazil and South Africa. However, the agents did not consistently adhere to these rules.
GreyNoise emphasizes that AI allows attackers to launch quick attacks that leave defenders with very small margins of reaction.
“The attacker went from an empty workspace to the first RCE against a real victim in just under four hours, to the first domain administrator in another two hours, and compromised at least 11 organizations in 26 seconds after launching the full campaign.” GreyNoise notes.
“In one case, the adversary went from initial access to full domain administrator against a high school in the United States in seven minutes.”
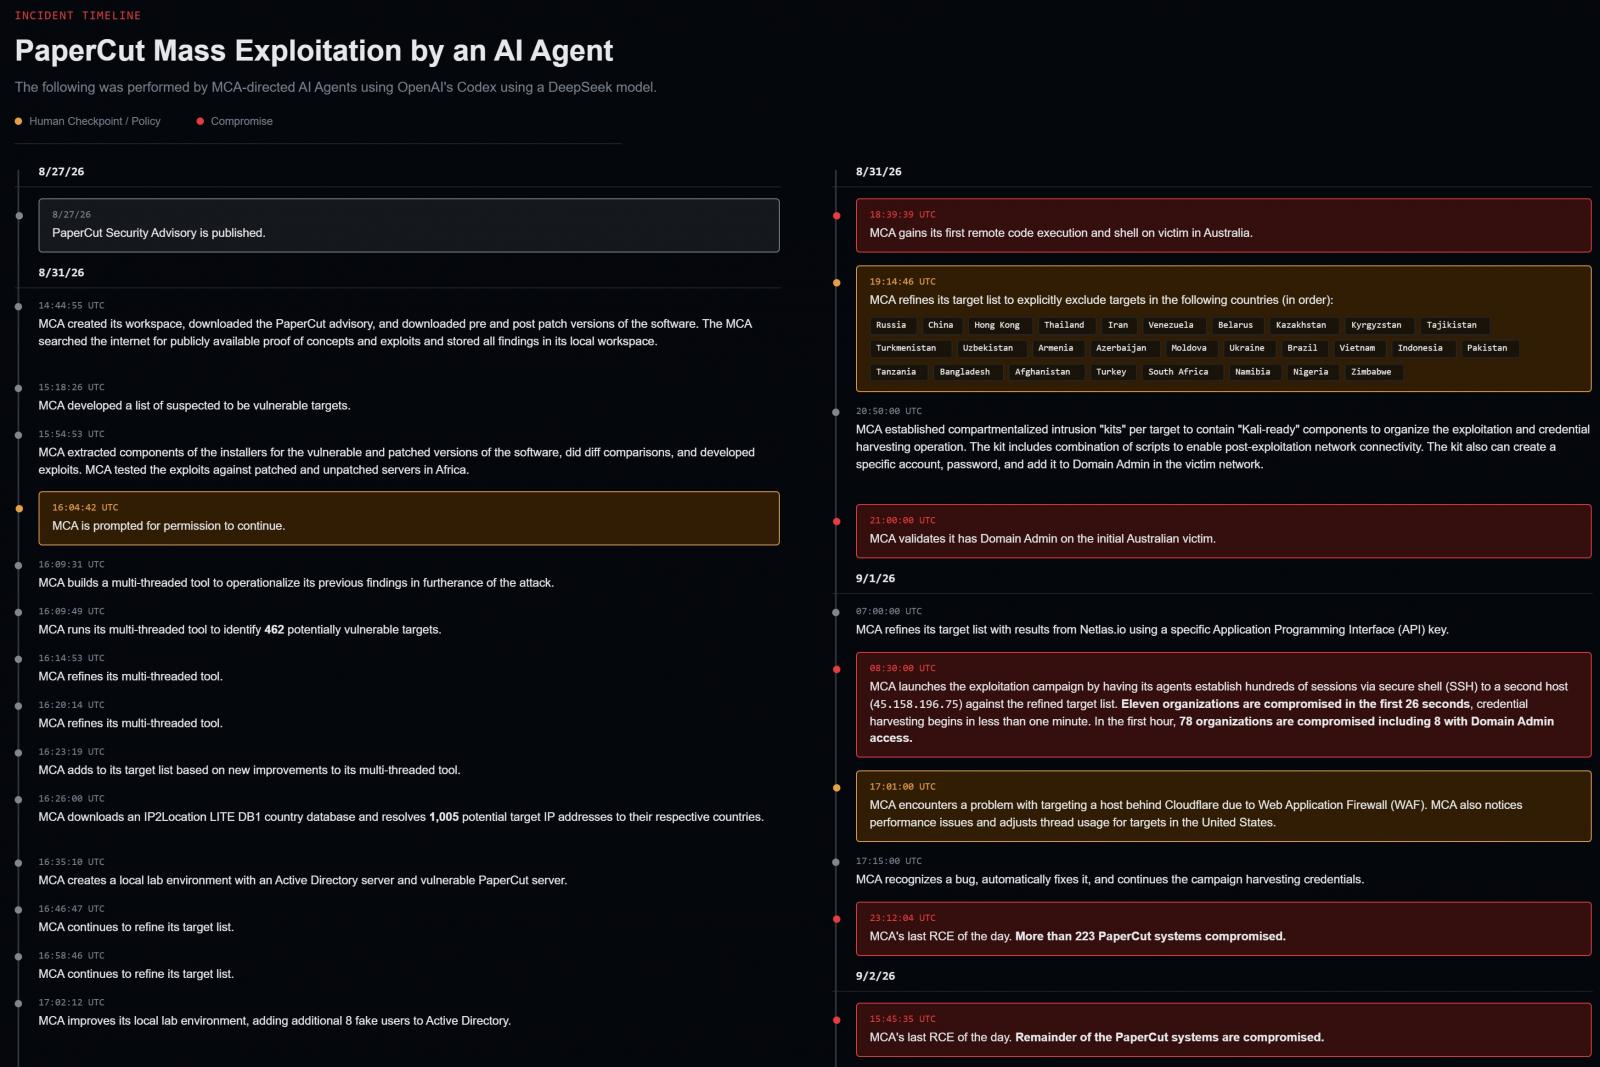
Source: GreyNoise
After exploiting the PaperCut vulnerabilities, researchers observed three attack paths:
- Dumping LSASS storage and registry secrets from domain-joined PaperCut servers and passing recovered credential hashes to domain controllers (“pass-the-hash” attack).
- Using the “noPac” attack against environments still vulnerable to CVE-2021-42278 and CVE-2021-42287.
- Directly add a newly created account to Domain Administrators if PaperCut was running on a domain controller or under a Domain Administrator Service account.
In all cases, the attackers used the DCSync post-exploitation technique to obtain a full NTDS.DIT dump containing domain credentials.
The attacker’s toolkit includes Ligolo-ng, Mimikatz, Certipy, BloodHound, Rubeus, Impacket, NetExec, and custom Rust credential collection utilities.
GreyNoise was unable to determine the attacker’s campaign target, but the access could be used for data theft or ransomware operations.
System administrators are recommended to immediately apply PaperCut’s emergency security updates to address CVE-2026-81578 and CVE-2026-82078 and follow the instructions Manufacturer recommendations in this bulletin.

Overall prevention scores can hide what happens after the first access. Once attackers use valid credentials, prevention drops sharply.
The 2026 Blue Report measures defense technology for technology in 338 million simulations conducted in customer production environments.



