Multiple extensions for Google Chrome and Microsoft Edge provided a malware framework that implemented modules to steal cryptocurrency, sensitive data and browser history, and to inject ClickFix decoys.
The researchers say all 19 malicious modules uncovered in the campaign serve different purposes and are designed to be “highly extensible.”
The operation was discovered by the application security company Socket, and the investigation shows that it may have been active since early 2024.
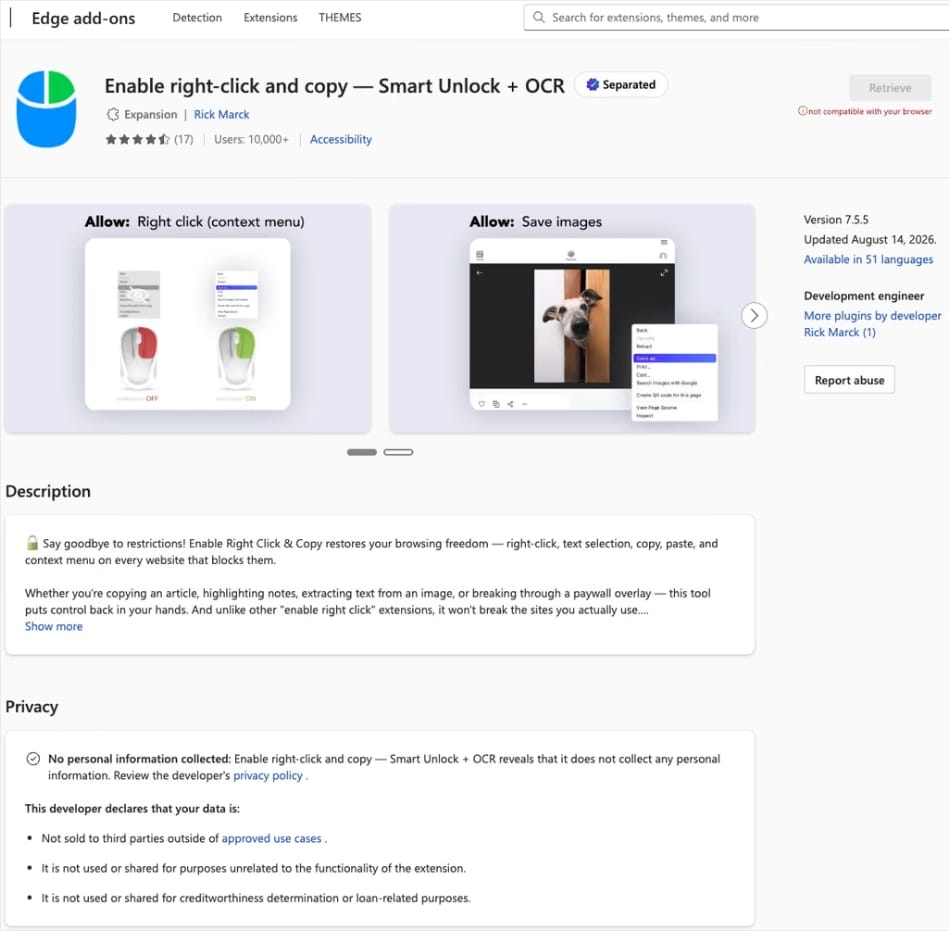
Socket says that when initially published in the Chrome Web Store, many of the extensions provided the advertised functionality and did not contain malware.
According to the researchers, five of the extensions were acquired by their original creators and injected with malware through automatically delivered updates.
One example is the “Enable Right Click & Copy — Smart Unlock + OCR” extension, which had a Chrome user base of at least 70,000 when it became malicious. Edge’s install count was 10,000 at the time.
Google caught the threat early and removed the extension from its add-on marketplace, but at the time of publishing the Socket report, the Edge version remained available.
Source: Socket
Once installed, the malware establishes an encrypted WebSocket connection to command and control (C2) servers, downloads JavaScript modules, strips Content Security Policy (CSP) headers from every website visited, and injects malicious scripts into websites via hidden HTML elements.
Socket monitors malware modules with the following capabilities:
- Draining EVM, Solana and Tron Wallets by Hijacking Legit Wallet Connect and Exchange Buttons
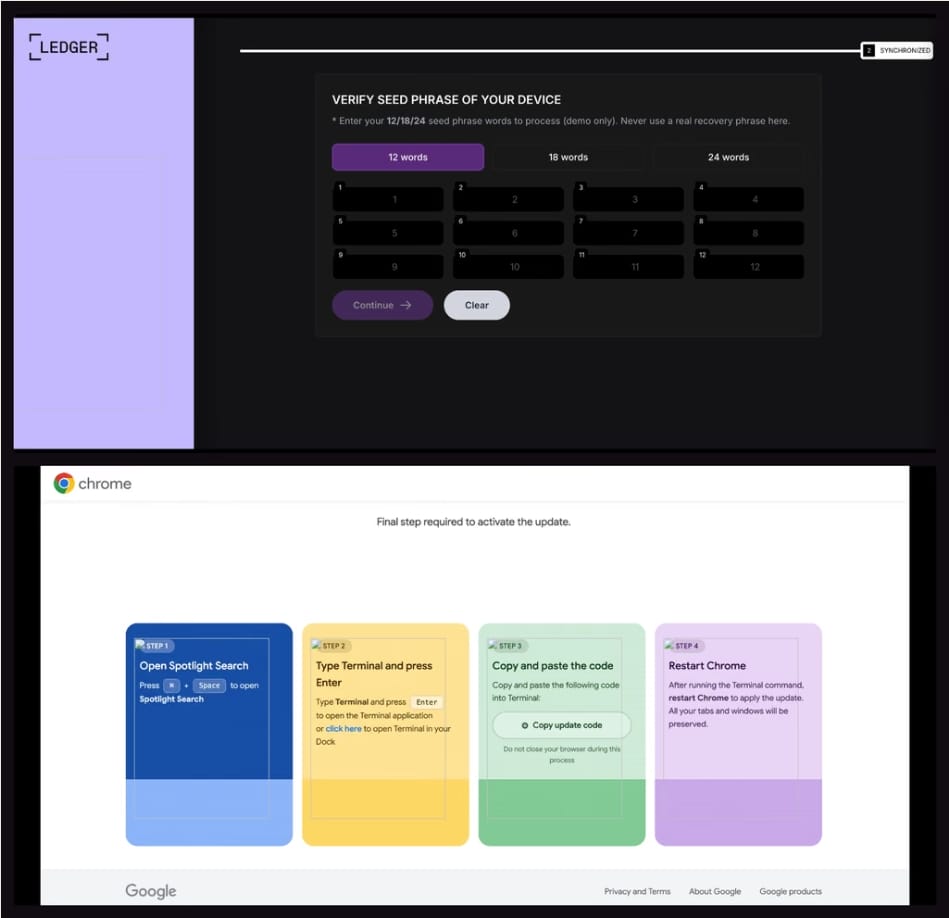
- Replacing the Ledger and Trezor websites with convincing phishing pages with opening phrases
- Theft of sessions, tokens, account data and balances from Coinbase, Binance, Kraken, OKX, MEXC, KuCoin, Bybit and MetaMask
- Saving credentials and form entries on websites
- Collection of information about Facebook and LinkedIn accounts
- Exfiltrate browser history
- Displaying fake ClickFix-style browser updates that instruct victims to execute commands provided by the attacker
Source: Socket
Socket warns that the malicious framework may have more modules and that as the malware evolves over time, new payloads are expected to be deployed.
At the time of publication, none of the malicious extensions are available on the Chrome Web Store.
The Socket Report provides the full list of extension IDs exposed in the campaign along with the domains used for C2 communication.
| Extension ID | Extension name |
| pkoccklolohdacbfooifnpebakpbeipc | Right-click activation and copy — Smart unlock + OCR |
| fegckejpfnlmfgkfjpinlbgmeeijjkel | RapidLens – Google Lens for screen and image search |
| kdenlnncndfnhkognokgfpabgkgehodd | QuickLens – Search screen with Google Lens |
| jamminefolhgepgihbmcjjhgldbfcikp | Password protect PDF |
| inmkjedjdhgpknjogbjomhnbgdccckkg | Enable Copy – Select and activate right button (Edge extension) |
| fcgdejjichpgfaaafflplhfijcnieopb | PixelCheck |
| cfpnjdbpojpcongfaefcamjbaolpelcd | Creative Library – Ad Spy Tool |
| aapdalkmclfaahehnmicbglkohkldhne | Website Traffic Check: MirrorSphere SEO Statistics |
| dkdadldmiefjldmegbjbnhhfddnkhlhm | Site Alert – Check website traffic and SEO |
| fjmlhlkccegopebcllcmafahkmeejpph | SEO Pulse Pro – Website Traffic and SEO Analyzer |
| iekoapohahgmogbagegmcgplbkikcgke | Private crypto news reader |
| ahpnnnjbnfbhoikhohglpohnoocjcoco | Blockfolio: Address Monitor |
| oeacadlaclegkkkdehjmiifnjhcekclj | Crypto exchange rates and fiat converter |
| jmlgannjlbliikgcaieomgmcnfplglea | Crypto Alert: Price Alerts and Volatility Alerts |
| lhmcajhgadanidbopgaoobjlldegjmke | DeFi Pulse Tracker |
| gfackggoapepdmnjnkblogdcjpgcjiak | Crypto Price Token: A Quick Look |
| hfijkbdkpidafdbeebnnkhfccildbcle | Multi-Chain Explorer |
| pcngchfbfgejllcbhmeadjhiebebiome | LedgerLook: Wallet Checker |
| aodkjdeghbjiaienipfjkbpcikkacbcp | Meta & Facebook Ad Library Spy — Save Ads, Finder, Downloader | FeedX-Ray |
Users who had any of the extensions installed should assume their credentials have been compromised and change their login passwords.
Cryptocurrency holders potentially affected by this campaign are advised to move their assets to the newly created wallet as soon as possible.
Update (August 30): The article has been edited to include the full list of malicious extensions detected by Socket.

Generic prevention scores can hide what happens after initial access. Once attackers use valid credentials, prevention plummets.
The 2026 Blue Report measures security techniques by techniques in 338 million simulations run in customer production environments.



