An unpatched vulnerability in Calix GS7 XGS (GS5239XG) home routers used by multiple U.S. broadband providers allows remote, unauthorized attackers to create port forwarding rules that could expose local network devices to the public Internet.
The vulnerability is tracked as CVE-2026-75501 and is described as a missing authentication issue that affects devices running EXOS/6.6.47 firmware.
Security researcher Brian Khan Quintana discovered the flaw, and after trying to notify the vendor on June 7 without success, he reported the vulnerability to the Carnegie Mellon CERT Coordination Center.
After repeated attempts to contact the vendor and no response, CERT/CC coordinated a public disclosure and Quintana released the technical details.
Calix is a major supplier in the US broadband provider market, working with major enterprises such as Cox Communications, Brightspeed, ALLO, CityFibre and Conexon.
The affected model, GS5239XG, is also marketed as GigaSpire 7u10txg and is a new premium gateway device that combines Wi-Fi 7 capabilities with an integrated XGS-PON optical terminal.
The CVE-2026-75501 vulnerability is caused by the device exposing “the MiniUPnPd control endpoint on the WAN interface on TCP port 5000 without access controls.”
“In affected firmware versions, the router connects its UPnP WANIPConnection SOAP service to the public WAN interface on TCP port 5000,” CERT/CC warns.
This allows an attacker on the public network to send unauthenticated “SOAP requests to add, delete, or list port mappings or to query the external IP address” to the device.
In this way, hackers can bypass network address translation (NAT) and router firewall protection and expose internal cameras, network attached storage (NAS) devices, administrative interfaces and IoT devices.
“One unauthenticated request from anywhere in the world is enough to open a permanent hole through the router’s firewall to every device in the house. No password. No prompt. Nothing on screen. Rule survives reboots.” Quintatna says.
The researcher says an attacker exploiting the security issue could take the following actions:
- Create arbitrary port forwarding rules
- Delete existing mappings
- List the current router mappings
- Extract its public IP address
Quintana tested the finding by sending requests outside his home network to create a port mapping that revealed an internal address. A configured non-expiration mapping remains active after the router is powered on.
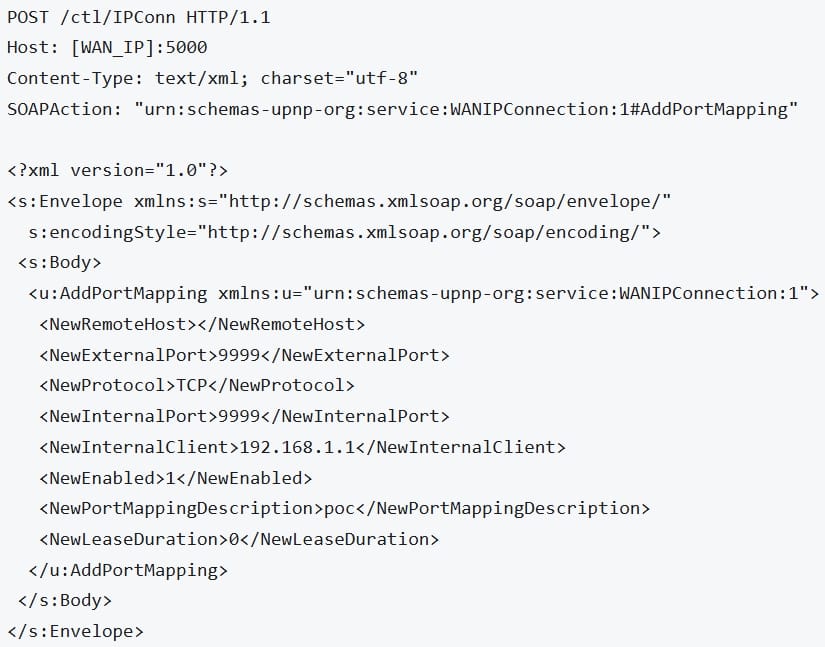
Source: drkq.github.io
This effectively means that anyone on the Internet can instruct vulnerable Calix routers to forward traffic from a public port to a selected device on the home network.
Given that there is no fix for CVE-2026-75501, Quintana recommends that users of the vulnerable device disable UPnP through the administrative interface (Advanced → Security → UPnP).
The researcher notes that this solution disables the automatic port opening that some games rely on, but it’s always possible to open certain ports manually.
CERT/CC also notes that the setting may be locked in some cases, and users who cannot change it should contact their ISP to request the deactivation.
BleepingComputer has reached out to Calix for comment on the flaw, the device models it affects and whether a patch will be released, but we have not heard back by the time of publication.

Generic prevention scores can hide what happens after initial access. Once attackers use valid credentials, prevention plummets.
The 2026 Blue Report measures security techniques by techniques in 338 million simulations run in customer production environments.



