Extortion group ShinyHunters stole personal information from 1.6 million RingCentral accounts after hacking the company in July, according to data breach notification service Have I Been Pwned.
RingCentral is a cloud-based collaboration and communication platform used by over 600,000 businesses for services such as calling, messaging and voicemail.
The company disclosed the incident on July 28, revealing that its systems had been compromised following what it described as a “sophisticated social engineering campaign.”
“We have not seen any new unauthorized activity since we undertook these remediation efforts. To date, this incident has affected the data of a limited portion of RingCentral customers, and we are communicating directly with affected customers.” noted.
“If RingCentral does not contact you, you are not affected. This incident did not impact RingCentral’s core platform and our services continue to operate without interruption.”
While RingCentral has not attributed the breach to a specific threat or hacking group and has yet to share further details about the incident, the ShinyHunters extortion gang took responsibility on July 27, claiming to have stolen 623GB of data.
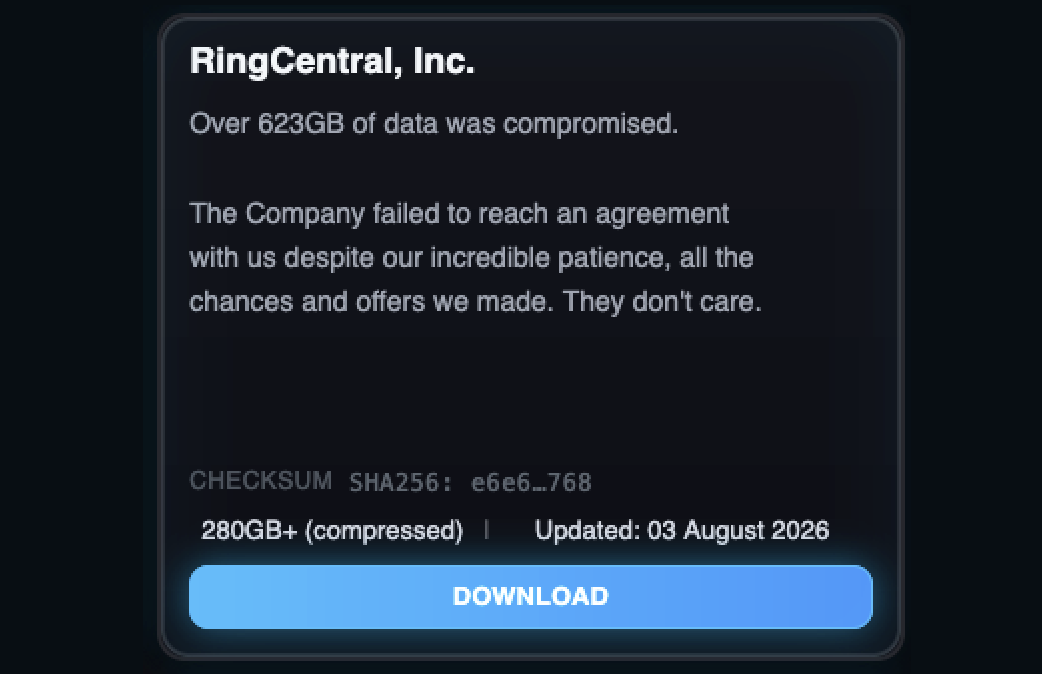
After the company refused to pay a ransom to destroy the stolen data, the cybercrime group leaked a compressed archive containing 280GB worth of files on their dark web data leak site.
While a RingCentral spokesperson did not immediately respond when contacted by BleepingComputer to confirm ShinyHunters’ claims, Have I Been Pwned confirmed the link after analyzing the leaked data and said Thursday that contained records for 1.6 million accountsincluding names, email addresses, phone numbers and physical addresses.
“In July 2026, the RingCentral cloud-based business communication platform was the target of a ShinyHunters ‘pay or leak’ extortion campaign,” it said.
Although RingCentral has not yet shared how exactly the threat actors gained access to its systems, ShinyHunters claimed breaches of hundreds of Salesforce customers over the past year, saying they stole more than 1.5 billion records in the Salesloft Drift and Salesforce Aura campaigns.
The ransomware group was also linked to security breaches at more than a dozen Snowflake customers, as well as various other third-party integration providers.
Most recently, ShinyHunters claimed responsibility for a new series of breaches at over 100 organizations following data theft attacks that exploited an Oracle PeopleSoft zero-day flaw.

Generic prevention scores can hide what happens after initial access. Once attackers use valid credentials, prevention plummets.
The 2026 Blue Report measures security techniques by techniques in 338 million simulations run in customer production environments.



