A new strain of Android malware called Mantax Otax combines ransomware and spyware capabilities to encrypt files, steal sensitive data, and spam and harass victims.
Indonesian operators distribute malware through malicious APK files hosted outside of Google Play, targeting users with phishing and social engineering messages.
Once installed, the malware asks for permission to use the accessibility service, which gives it broad control over compromised devices.
It then fetches its command-and-control infrastructure (C2) domain from GitHub and sends back details about the victim such as location, operator, Android version, and device ID. C2 can send commands over Firebase or WebSockets for execution.
According to CimperiumIndonesian operators distribute the malware through malicious APK files hosted outside of Google Play, the official Android app store, using phishing messages and social engineering to target victims.
Encryption on older Android
According to mobile security company Zimperium, Mantax Otax encrypts devices running older versions of Android. It searches for shared storage and encrypts target file types using a victim-specific AES key obtained from the C2 server.
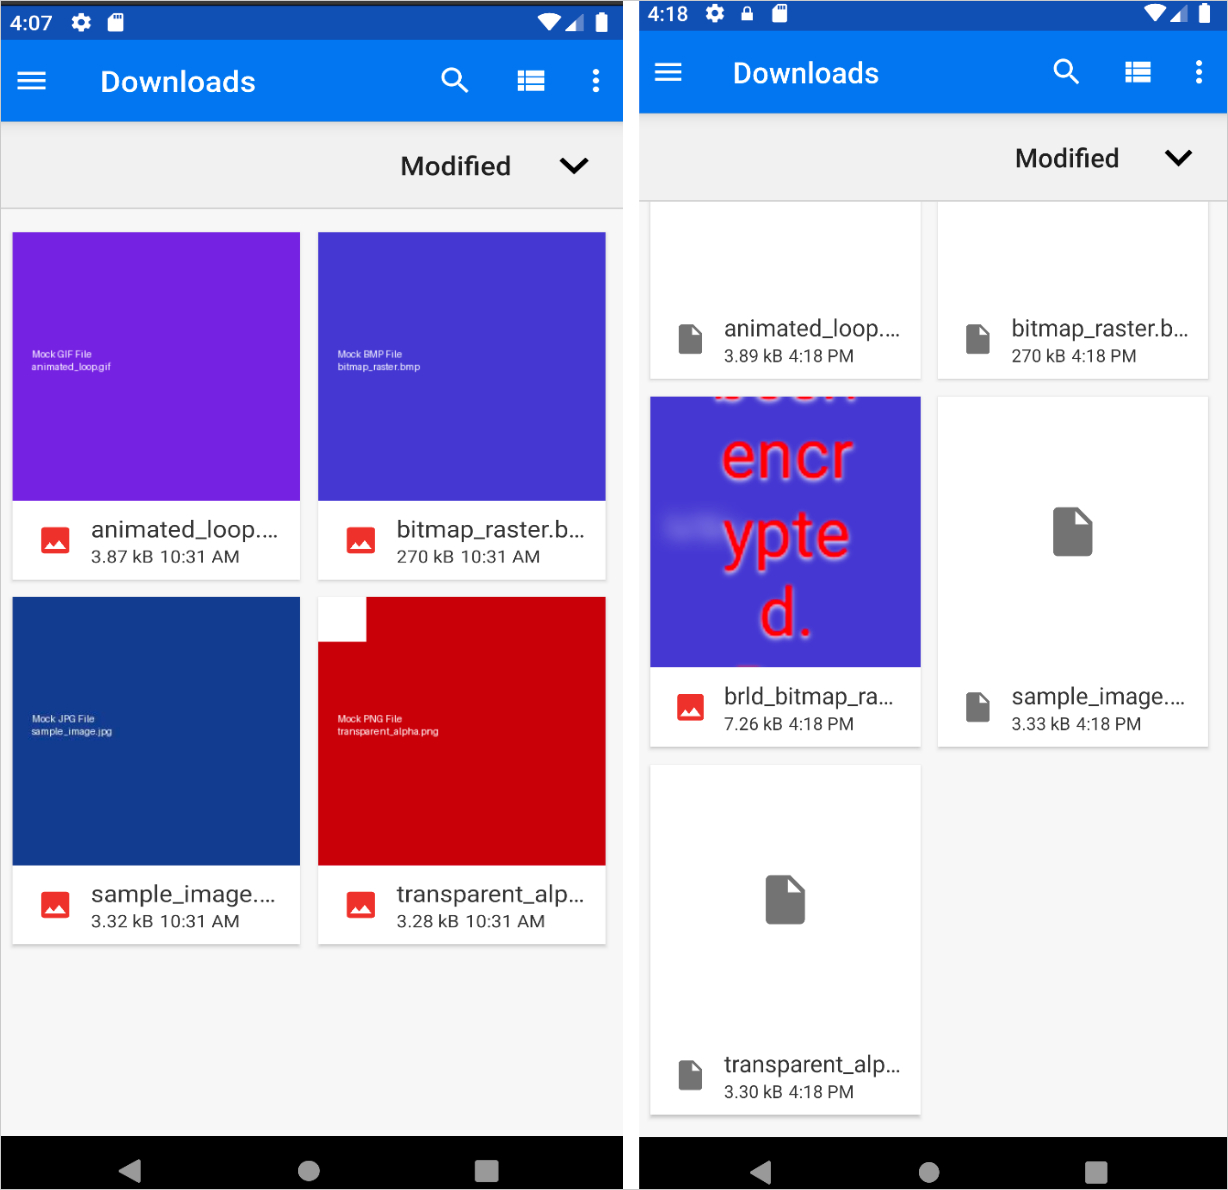
The malware then deletes the original files and adds the “.enc” extension to the encrypted copies.
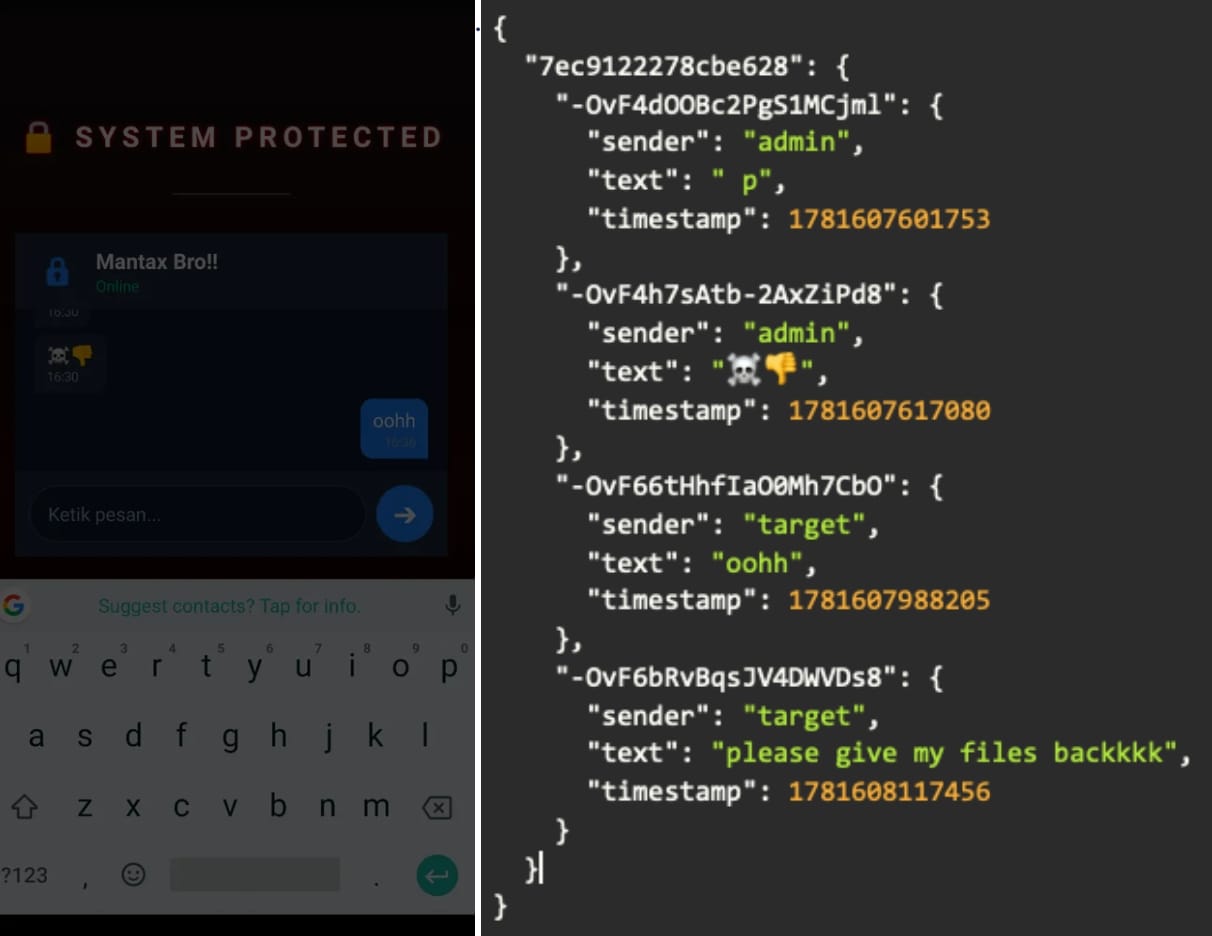
Mantax Otax also replaces local images with ransom notifications and opens a full-screen chat hosted by Firebase to facilitate ransom payment negotiations.
Source: Zimperium
Zimperium researchers were able to exploit a misconfiguration in the Firebase C2 server that exposed the attackers’ chats with the victims.
Source: Zimperium
The Mantax Otax ransomware module only works against Android devices running version 9 or earlier, as the “Scoped Storage” security and privacy feature in Android 10 and later greatly limits the ability to encrypt to the external file directory.
Spying, Spam and Harassment
Apart from ransomware, Mantax Otax includes spying, remote control and harassment features.
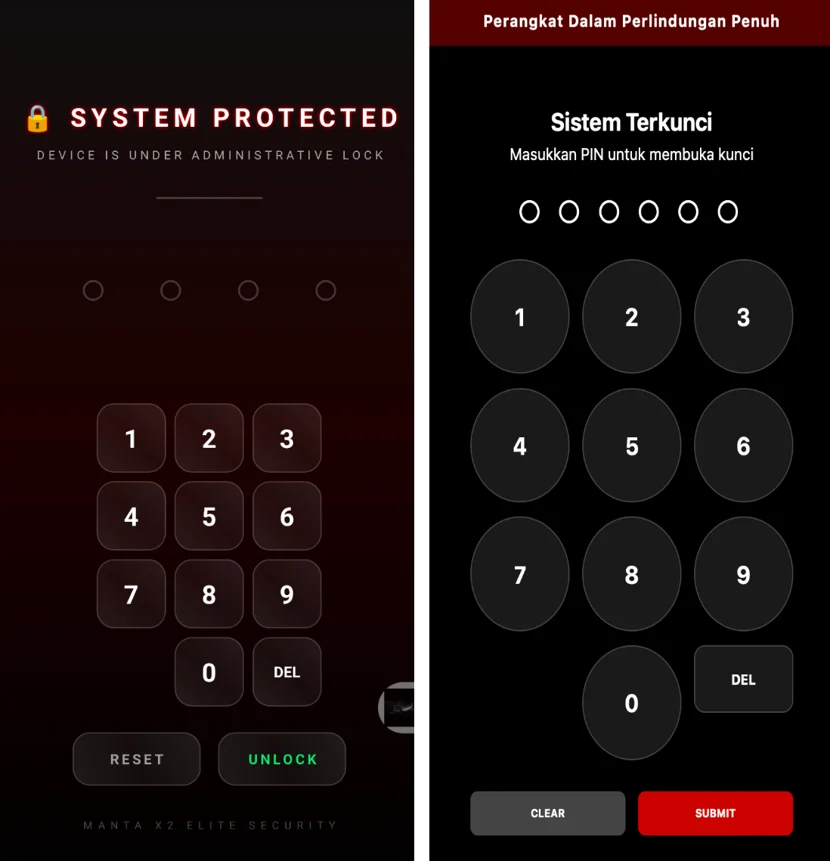
The the researchers note that the malware can steal lock screen PINs to maintain persistent access, read SMS and one-time passwords, access call logs, contacts, browsing history, app lists, Google account information, and location.
Source: Zimperium
It can also retrieve WhatsApp profiles and messages, as well as Telegram chats, using simulated interactions through accessibility services.
It also abuses the Android MediaProjection API to capture screenshots, record MP4 videos, and stream the victim’s screen in near real-time via the Catbox file hosting service.
Mantax Otax can also capture photos using the infected device’s cameras and upload them to the operator.
Version 2 of the malware added harassment features such as repeating dialog boxes, full-screen videos, quick “jumpscare” image overlays, and remote-controlled text messages played through the device’s speakers.
These additional features add an intimidation component to the attacks, which act as a mechanism to pressure the victim into paying the ransom.
Since Zimperium is a Google security partner through the App Defense Alliance (ADA), Mantax Otax is now detected and blocked by current Android devices with active Play Protect service.
Users are generally advised not to install APK files outside of Google Play, not to grant accessibility permissions to questionable apps, and to only trust reputable publishers.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital meeting on what AI attacks are changing, what defenders need to stop doing, and how to validate, solve, fix, and revalidate at machine speed.



