Access keys were introduced with a strong security proposition. Replace passwords with public key cryptography, tie credentials to the legitimate service, keep the private key away from the server, and many of the phishing and credential theft attacks that have plagued enterprise security for decades become dramatically more difficult.
This is all true. But the security conversation has changed very quickly.
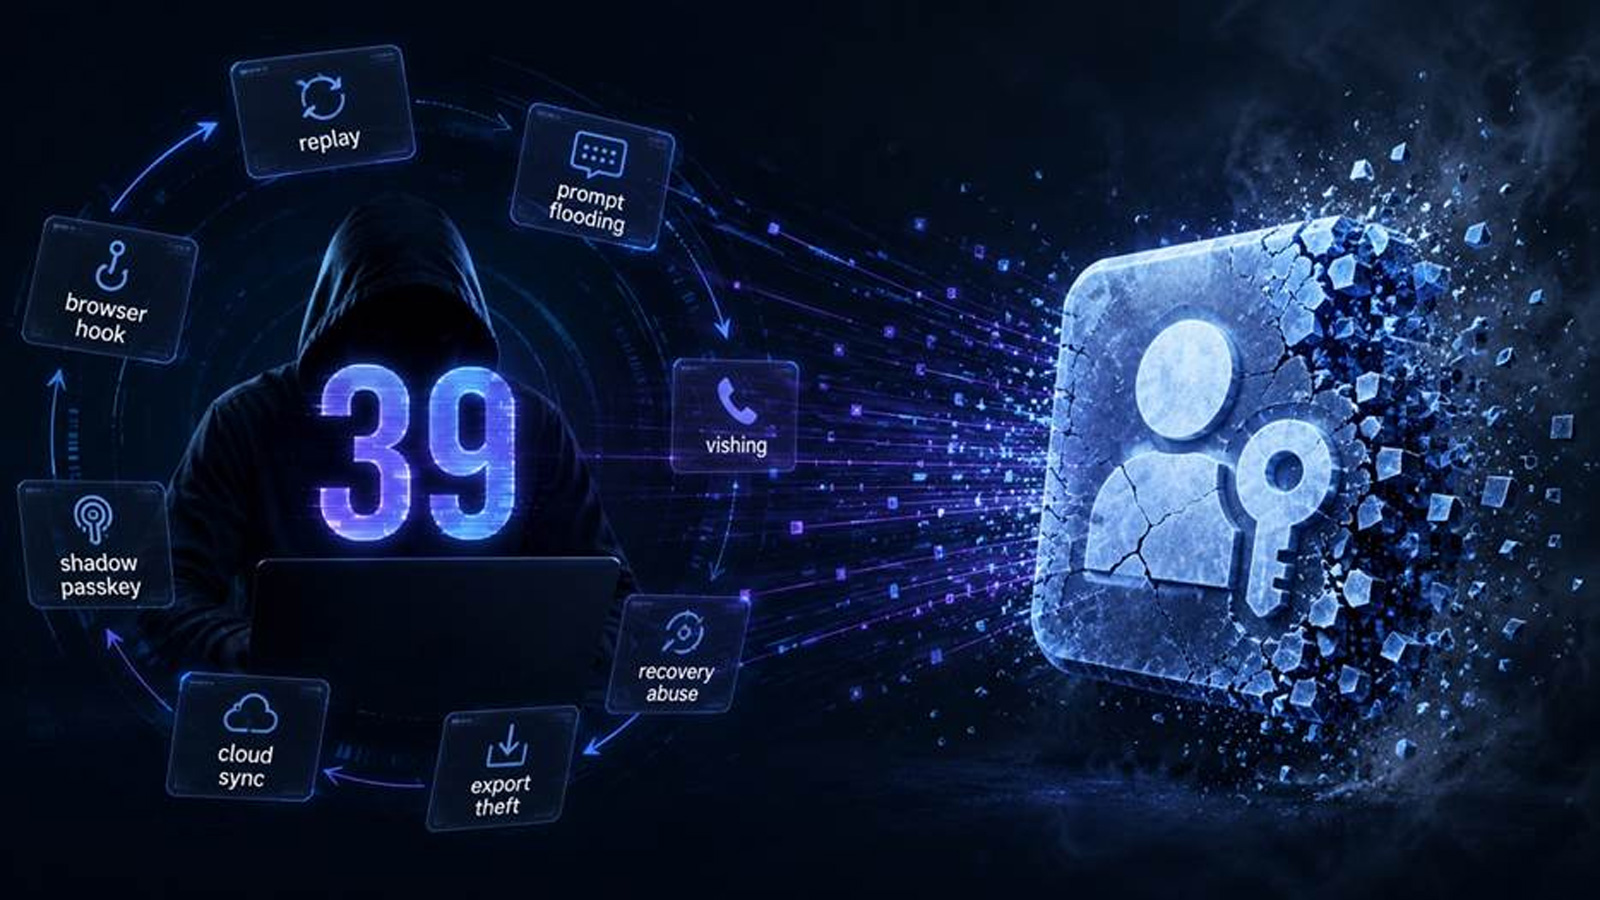
There are now at least 39 publicly documented methods, attack paths, research techniques, and use cases involving passwords and the infrastructure around them. Many already have working proof-of-concept tools or published research showing exactly how the techniques can be implemented. Some are already showing up in real-world attack patterns.
This does not mean that criminals have used all 39. It means that the playbook is being written publicly and attackers no longer have to come up with these techniques themselves.
More importantly, the research reveals a fundamental difference that businesses need to understand. The cryptography in FIDO2 can remain completely intact while the password-protected account is still compromised.
The target is no longer just the password
Modern password authentication the ceremony crosses too many lines of trust. It can include a web application, browser, operating system, password manager, cloud sync service, mobile device, Bluetooth transport, account recovery system, enrollment process, help desk, and ultimately the human being who approves the authentication.
Researchers attack almost every one of these layers. Published techniques now include assertion mining, assertion replay, interrupt attacks, assertion phishing, browser hooking, assertion capture, challenge injection, replay, user authentication manipulation, and user presence manipulation.
SpecterOps demonstrates the importance of this issue in its Pass the Passkey study. One of the most important observations was that malware does not necessarily need to extract a private key.
A malicious Windows application can request the legitimate WebAuthn infrastructure to generate a signed assertion. The user sees what appears to be a legitimate Windows authentication, completes the verification, and the attacker receives the resulting assertion.
The private key never left its secure location. The cryptography was not cracked. Yet the authentication process was successfully manipulated.
This distinction is central to understanding the new password threat model.
Access keys are not completely secure unless they are linked to special biometric hardware.
Learn how attackers take advantage of password logging instead of cracking password cryptography and why specialized biometric hardware strengthens enterprise identity security.
Even the password prompt is an attack surface
Several of the 39 published techniques focus on the user interface around authentication.
Researchers have demonstrated password prompt flooding, credential interface spoofing, application metadata spoofing, window handle spoofing, remote desktop password phishing, and FIDO interface overlay attacks.
This recreates a problem that the security industry has already faced with push-based MFA. Users get used to authentication prompts. Once authentication becomes a routine visual interaction, attackers can manufacture, repeat, mask, or strategically time these interactions.
SpectreOps demonstrated tools capable of repeatedly invoking legitimate-looking Windows password prompts. The researchers also demonstrated techniques that can make malicious authentication activity appear to originate from an application that the employee already trusts.
The lesson is important. Phishing resistance at the cryptographic protocol level does not guarantee spoofing resistance at the operating system, browser, application, and user interface layers surrounding that protocol.
Shared passwords Expand the attack surface
The attack surface increases significantly when access keys can be shared, synchronized, exported, restored, or moved between devices.
The published inventory now includes sync vault compromise, Apple or Google account hijacking, cloud recovery hijacking, stolen or compromised phones, mobile malware, rooted mobile devices, hybrid authentication manipulation, KeePassXC export theft, Bitwarden export theft, credential exchange theft, malicious browser extensions, and attacks involving CTAP and Bluetooth communication.
This is not essentially a cryptographic problem. This is an architectural problem.
Once credentials can be moved between devices, synced through a cloud account, exported from a vault, recovered using another identity, or recovered through another process, the security boundary extends far beyond the original authenticator.
The attacker no longer has to defeat FIDO2. An attacker must compromise a sufficiently trusted component somewhere in the surrounding ecosystem.
Therefore, a synced passkey can use extremely strong cryptography while inheriting the weaknesses of the phone, operating system, password manager, cloud account, browser, recovery process, and sync system responsible for managing it.
Save and restore Create another opening
Some of the most consistent attacks do not steal an existing access key at all. They just create another.
Published techniques include shadow passwords, logging vishing, attacker phone logging, attacker-controlled passkey logging, help desk hijacking, temporary credential abuse, SIM-based recovery, reverse vishing, and pretext migration attacks.
Consider what happens when an attacker gains enough control over an employee’s account to initiate a legitimate password login. Instead of extracting the employee’s existing credentials, the attacker registers entirely new credentials on a device controlled by the attacker.
Nothing is cracked. Nothing is necessarily stolen from the existing authenticator. The legitimate service itself creates perfectly valid credentials for the adversary.
This leads to an increasingly important principle of identity. Phishing-resistant authentication is insufficient if device recording, replacement, recovery, and registration are not protected to the same standard.
Special biometric hardware changes the attack surface
Dedicated biometric hardware approaches the problem much differently than passwords stored on general-purpose devices.
A purpose-built biometric authenticator can store personal credentials on secure hardware with no cloud sync, no export mechanism, and no password manager responsible for moving credentials between devices.
Authentication may require a live fingerprint directly on the authenticator, as well as physical proximity to the endpoint requesting access.
Equally important, the dedicated authenticator must not contain a traditional general-purpose operating system, app store, browser, or screen.
This distinction eliminates huge portions of the attack surface.
There are no third-party apps for an attacker to replace with malicious versions. Rogue apps cannot simply be installed on the authenticator. No compromise with a browser extension ecosystem. There is no screen where the malware can present a fraudulent authentication interface.
There is no custom operating system full of unrelated apps, permissions, background services and update dependencies.
The authenticator performs a very small number of security-specific functions and nothing else.
This drastically changes the economy of his attack. Instead of trying to compromise a massive general-purpose computing environment, an attacker faces a tightly controlled hardware device designed specifically to protect cryptographic credentials and verify biometric identity.
It also makes the authentication process much more resistant to employee tampering. An employee may be convinced to visit a website, answer a phone call, or follow instructions from someone claiming to be tech support. But social engineering can’t install a fake app on hardware that doesn’t run regular apps.
It cannot manipulate a screen that does not exist. It cannot sync credentials through a cloud service that the authenticator does not use.
In this sense, properly designed specialized biometric hardware becomes both highly resistant to attackers and highly resistant to errors made by employees.
Correct configuration of the service is critical
Dedicated hardware alone is not enough. The trusted service must be configured to preserve the security model.
For sensitive enterprise environments, authentication and enrollment should be limited to approved authentication classes. The relying party must validate the identity of the authenticator, enforce user verification, properly validate challenges and sessions, use appropriate countersignature defenses, and prevent weaker methods from becoming fallback authentication paths.
Recording and recovery deserve special attention. Adding a new authenticator should require proof from an already authorized authenticator, rather than simply proving account control through a weaker recovery channel.
Configured correctly, this architecture prevents an attacker from simply recording a simple password from another laptop, phone, software vault, or security key. Ingesting a cloud account does not give away the credentials. Compromising the password manager does not. Mobile malware cannot infect the authenticator.
No malicious app can be installed on it. And a remote attacker cannot produce the combination of special hardware, biometric verification, physical proximity, and legitimate interaction with the service required for authentication.
What the 39 attacks really tell us
The existence of 39 published attack methods does not mean that FIDO2 cryptography has failed. In many ways, it shows the opposite.
Researchers repeatedly attack the software, synchronization systems, recording processes, operating systems, browsers, recovery mechanisms, and people around credentials because directly defeating properly implemented cryptographic hardware is significantly more difficult.
This should tell security leaders where the next identity frontier should be.
For high-value enterprise identities, credentials should not be freely sharable between user devices and cloud ecosystems. They must be tied to dedicated biometric hardware, a verified person, a legitimate service, and an enterprise-controlled enrollment and recovery process.
Access keys solved much of the password problem. The 39 published attacks show us what the attackers are targeting.
Specialized biometric hardware, properly implemented from enrollment through authentication and recovery, removes virtually all of this surrounding attack surface before an attacker has the opportunity to exploit it.
Download Security eBook with Access Key to explore many published attack methods and see how specialized biometric hardware is changing the corporate identity trust model.
Sponsored and written by Token.



