A critical authentication bypass vulnerability (CVE-2026-82329) in JFrog Artifactory is exploited in token creation attacks that provide administrative access.
The vulnerability is present in the default configuration of self-managed instances of JFrog Artifactory, a repository manager used to store, organize, secure, and distribute software packages.
An unauthorized attacker with network access can use it to gain administrative permissions.
Researchers at the offensive security company watchTowr noticed that the flaw was being used by “attackers who hack admin tokens.”
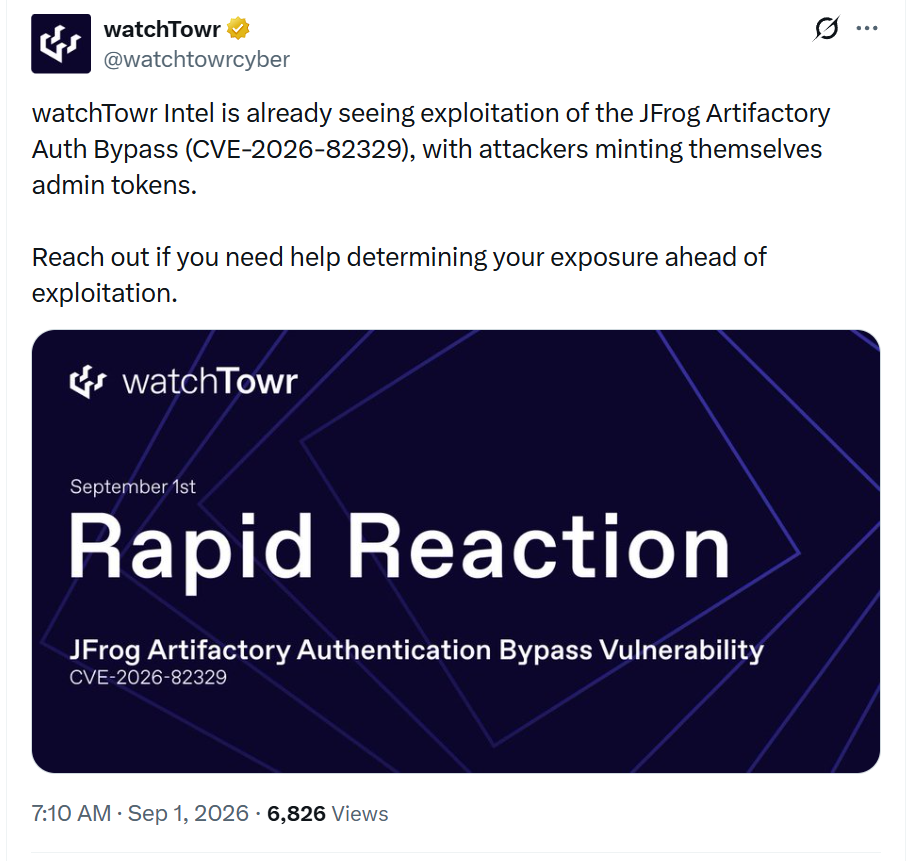
The details of the flaw are scarce and JFrog’s advice doesn’t share many details other than that the pass can be used in Artifactory’s default configuration.
CEO of Vercel Guillermo Rauch warned that the impact of the flaw could go beyond compromising the Artifactory itself.
“Administrative access to Artifactory reaches released artifacts that downstream systems already trust and download automatically,” Colin Hogue-Spears, senior director of solution management at application security company Black Duck, told BleepingComputer.
Spears also notes that JFrog treats access tokens as independent credentials with their own expiration and revocation mechanisms, so upgrading the Artifactory binary does not by itself invalidate an already issued token.
Because organizations use Artifactory to store binaries and packages used by build and deployment systems, attackers with administrative access can replace trusted artifacts and potentially execute malicious code on downstream systems.
Rauch also speculated that the vulnerability may be related to recent research involving autonomous AI agents.
JFrog considered the matter on August 28 in Artifactory versions 7.111.21, 7.117.28, 7.125.20, 7.133.29, 7.146.38, and 7.161.20. The provider says that JFrog Cloud environments have already been secured.
A hacker forging his own admin tokens means he can perform a variety of sensitive actions, such as enumerating users, groups, and federated topologies, reading artifacts, changing security configurations, and poisoning existing packages.
However, the extent of the compromise and whether the servers were actually breached is unclear. The number of victims, details of telemetry and indicators of compromise (IoC) are also unclear.
BleepingComputer has contacted JFrog to confirm the reported activity, but we have yet to hear back.

Generic prevention scores can hide what happens after initial access. Once attackers use valid credentials, prevention plummets.
The 2026 Blue Report measures security techniques by techniques in 338 million simulations run in customer production environments.



