Cybersecurity firm ReliaQuest confirmed it was attacked by hackers linked to the notorious ShinyHunters group, but said the impact of the attack was limited.
ReliaQuest revealed on August 17 in an X post that it tracked a widespread ShinyHunters phishing campaign involving domains with the “company.claims” URL pattern.
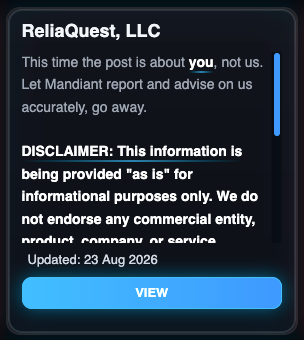
The company also warned that the hacking gang was expanding its social engineering tactics to include impersonating a legal team along with impersonating IT and the help desk.
In response to this now-deleted post, someone shared some screenshots that appear to show access to the ReliaQuest Okta dashboard.
The same screenshots were posted on the ShinyHunters website, along with a message mocking the security firm.
ReliaQuest addressed the incident on Monday, admitting it was the target of a social engineering attack over the weekend.
According to the company, hackers registered a fake domain and set it up to host a ReliaQuest SSO phishing page.
“The threat actor then called several ReliaQuest teammates, each time impersonating a security official by name in an attempt to direct them to the fake page,” the security firm explain. “A teammate entered his password and approved the push notification on his phone. This gave the attacker a short session on our identity board.”
ReliaQuest says the attackers only gained review access to the dashboard and says its applications, systems and customer data were not compromised.
“The threat actor continued to attempt to access these applications from the dashboard, but was consistently denied due to the security controls in place,” it noted.
ReliaQuest added: “No additional identities were accessed, no business applications were reached, no customer or ReliaQuest data was accessed beyond the user’s login credentials, and no persistence was established. Claims that ReliaQuest was compromised or targeted by ransomware are false.”
Connected: Cl0p Ransomware Group Names Over 40 Victims of PTC Windchill Campaign
Connected: Personal Information Exposed in the Apollo Global Data Breach
Connected: 1.6 million likely affected by RingCentral data breach



