Cybersecurity company ReliaQuest has confirmed that one of its employees was the target of a social engineering attack after hackers posed as a member of the security team.
In a statement over the weekend, ReliaQuest said an attacker called multiple employees and tried to trick them into accessing “a fake ReliaQuest single sign-on (SSO) page behind a content delivery network.”
Last week, ReliaQuest’s threat research team shared in a already deleted postthat the ShinyHunters extortion gang registered .claims domains to impersonate company help desks and IT teams.
“ReliaQuest is tracking a widespread ShinyHunters campaign using domains that follow the company(.)claims pattern. These domains include the target organization’s name or abbreviation under the .claims TLD,” X’s company post said.
Yesterday, a the newly created X account believed to be related to the threat, participants responded to the post saying “Who’s hunting who?”, sharing screenshots of what appeared to be a compromised Okta SSO account for a ReliaQuest employee.
Soon after, ShinyHunters posted the same screenshots in a new entry on their leak site.
ReliaQuest’s and the alleged threat actor’s posts were later taken down by X.
According to the company, the threat hosted the phishing page on a “lookalike domain” that BleepingComputer found to be reliaquest.claimsand used the name of a real security guard in the phishing attempts.
One of the targeted employees fell for the attacker’s ruse, entered his credentials on the fake SSO page and approved a targeted MFA notification, giving the attacker temporary, view-only access to the ReliaQuest identity dashboard.
However, the device’s trust controls successfully blocked subsequent attempts to access apps through the dashboard, according to the company.
“The level of access was for review only. No ReliaQuest applications or systems were accessed and no customer data was ever touched,” ReliaQuest says.
“The threat actor continued to attempt to access these applications from the dashboard, but was consistently denied due to the security controls in place.”
The cybersecurity firm says it terminated the attacker’s sessions, voided the exposed password and reset all authentication tokens.
The subsequent investigation found no evidence of access to other accounts, applications or data, and no indication that the actor had established a vulnerability in ReliaQuest’s systems.
The firm audited management fidelity, device trust and network access since August 21 and found no suspicious activity.
ShinyHunters takes the attack
ReliaQuest’s statement comes shortly after the infamous data extortion group “ShinyHunters” announced an attack on the company.
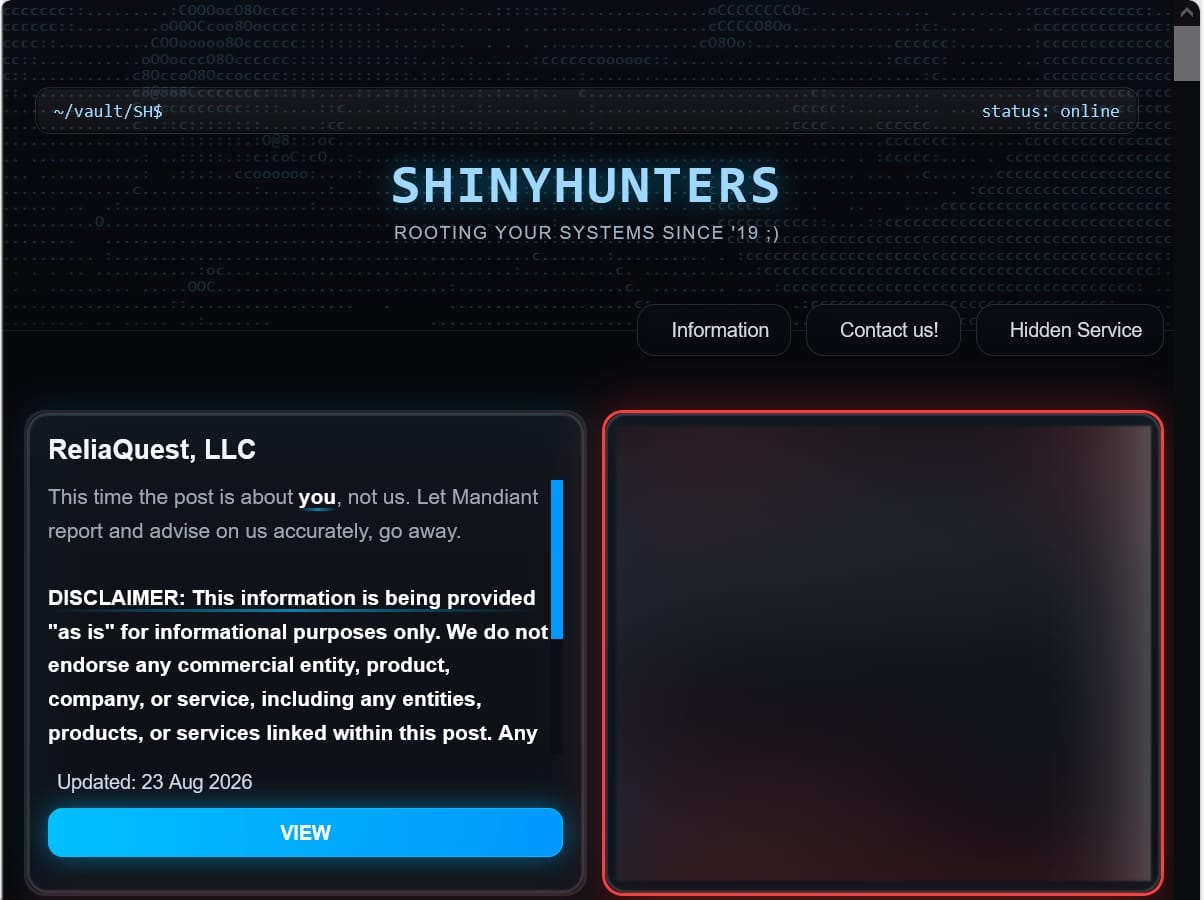
In a new post on its extortion portal, ShinyHunters refers to ReliaQuest’s previous report on the threat group, saying that “this time the post is about younot us.”
Source: BleepingComputer
The threat actors published proof of access showing that they had successfully breached ReliaQuest’s Okta SSO account.
We have asked ReliaQuest if the disclosed incident is related to ShinyHunters, but have not yet received further information.
However, ShinyHunters told BleepingComputer that their access is for review only and does not reach applications, systems or customer data.
“No additional identities were accessed, no business applications were reached, no customer or ReliaQuest data was accessed beyond the user’s login credentials, and no persistence was established,” the threat actor told us.

Generic prevention scores can hide what happens after initial access. Once attackers use valid credentials, prevention plummets.
The 2026 Blue Report measures security techniques by techniques in 338 million simulations run in customer production environments.



