A previously unknown malware family called SynkLoader is spreading in Microsoft Teams phishing campaigns to steal credentials via a fake lock screen.
The attacker poses as the target company’s IT help desk, a tactic Microsoft highlighted earlier this year as increasingly common in multi-stage attacks.
Expel security researcher Marcus Hutchins explains that the attacks direct the victim to install a fake “PowerShell Cleaner” (.MSI) executable file hosted on Microsoft Azure, which makes the download look legitimate.
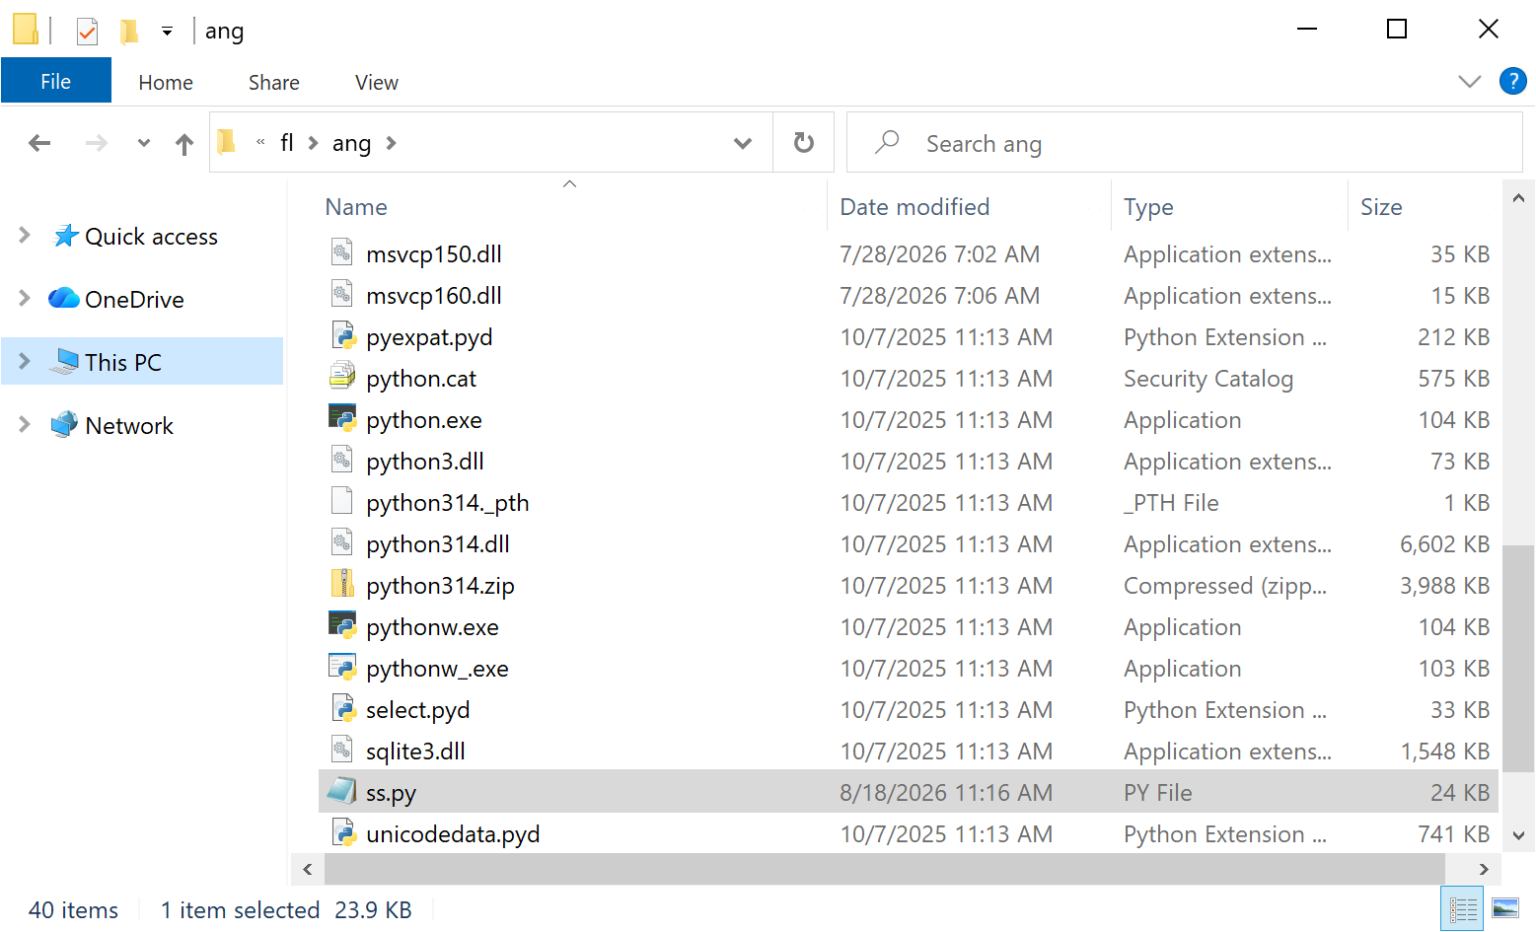
Analysis of the malware showed “compile dates and file timestamps indicating that it was first compiled and distributed around July 28, 2026.”
The installer extracts a PowerShell script named cleaner.ps1 and a ZIP archive containing the Python framework, a malicious Python script, precompiled Python libraries, and several fake Microsoft executable DLLs.
source: Expel
Based on the breach profile of the environment and operational objectives, attackers choose which modules to deploy.
SynkLoader was named so because of its unusual combination of Python, PowerShell, C# and C++, sometimes mixing up to three programming languages in one module.
Expel identified the following SynkLoader modules after setting up a honeypot pinging the attacker’s C2 posing as a legitimate victim:
- System profilers — Collects hostname, user name, privilege level, running processes, services, domain details, and number of computers in Active Directory.
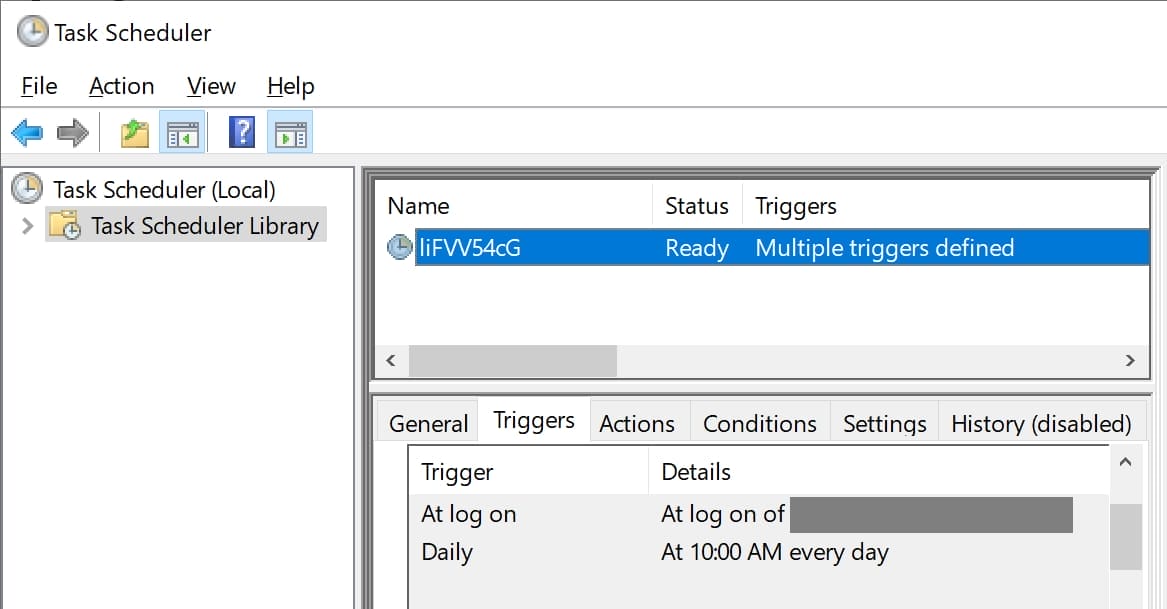
- Persistence module — Creates an arbitrarily named scheduled task that starts SynkLoader at user login and every day at 10am
- PhishLocker — Displays a convincing fake Windows lock screen to capture the user’s login password.
- TrafficRedirector — Creates a reverse proxy that allows attackers to reach internal network services or route Internet traffic through the infected computer.
- Interactive Shell (RAT) — Allows attackers to remotely execute PowerShell commands and receive their output.
- StreamMaster (VNC) — Streams the victim’s desktop and allows remote control of the active session with a mouse and keyboard.
- Module status script — Reports which malware modules and related threads are currently running.
Source: Expulsion
Windows 11 fake lock screen
The most interesting component of SynkLoader is the PhishLocker module, which attempts to obtain the victim’s Windows account password via a fake lock screen.
Once the password was obtained, attackers could use it in conjunction with the tunneling module to access corporate environments from the infected device, bypassing IP whitelist restrictions.
While the fake lock screen looks particularly convincing, Expel notes that simply using Alt+Tab shows the active windows at the top of the lock screen, which is simply “a full-screen borderless GUI application.”
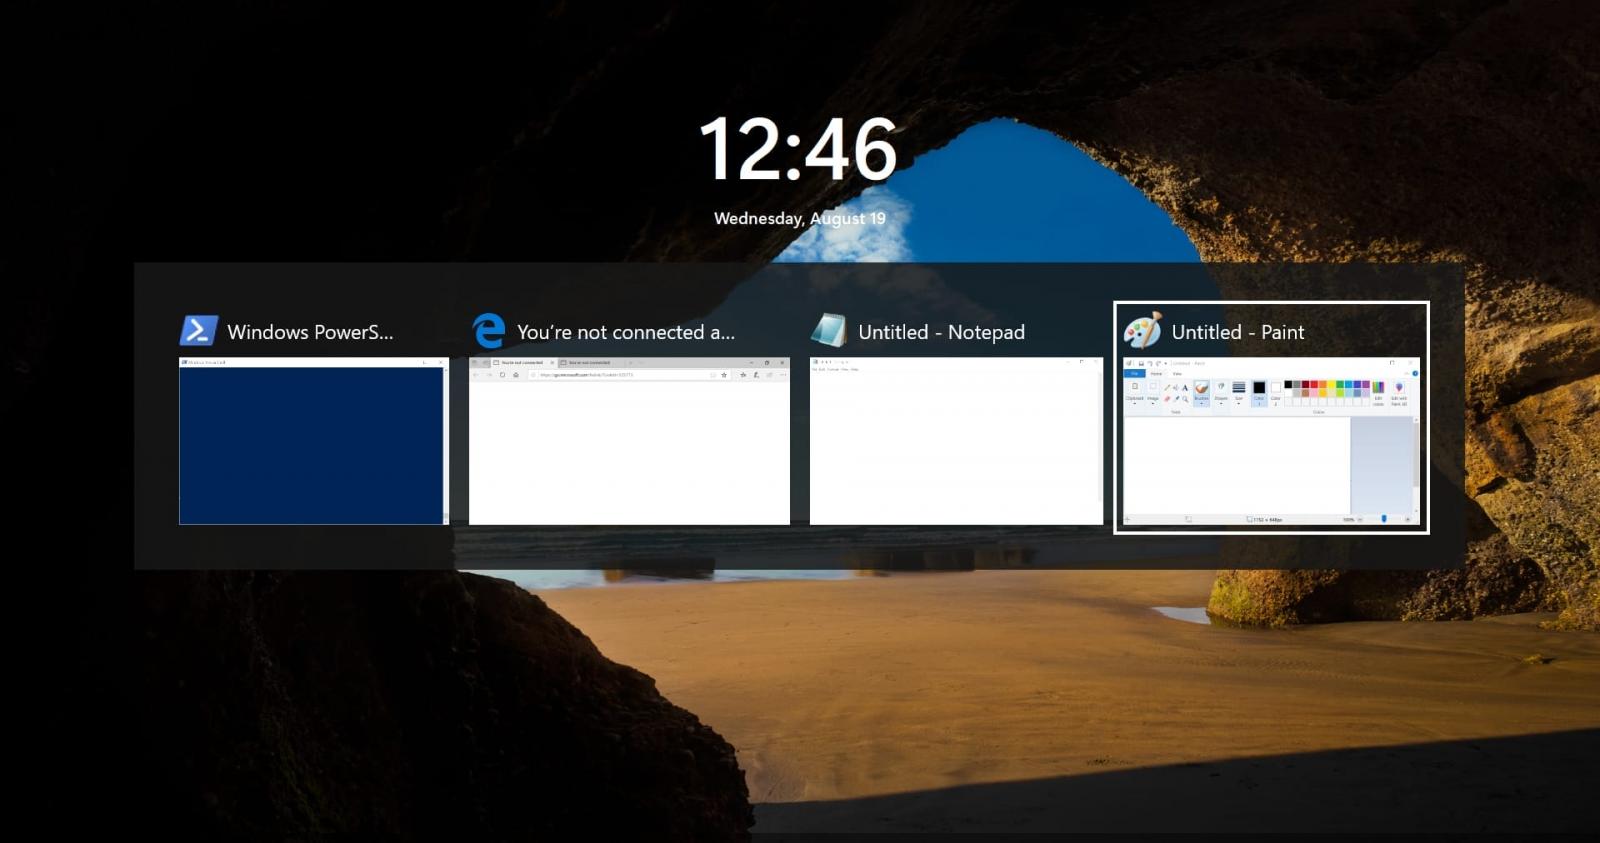
Source: Expulsion
Hutchins says that based on SynkLoader’s focus on measuring the size of an Active Directory environment, it is likely to be used in ransomware operations.
“We ended up writing an emulator for the shellback module, just to confirm that it was actually a hands-on keyboard attack,” says the researcher.
“The threat actor attempted to execute several profiling commands before realizing they were not in a real environment and disconnecting.”
Expel provided Indicators of Compromise (IoCs) for the observed attack, although it noted that SynkLoader module hashes are unique to each infection and therefore not very useful to defenders.
Best practice would be to check IT requests independently and avoid installing unwanted MSI files.
When you encounter an unexpected lock screen, try Ctrl+Alt+Delete or Alt+Tab to determine its authenticity.

Generic prevention scores can hide what happens after initial access. Once attackers use valid credentials, prevention plummets.
The 2026 Blue Report measures security techniques by techniques in 338 million simulations run in customer production environments.



