More than 9,300 Amazon Web Services (AWS) access keys that were made publicly available between August 2022 and August 2026 are still active and valid.
Truffle Security has been tracking this disclosure for four years and says 817 of the exposed keys were associated with companies, 526 of which were AWS root keys.
According to the researchers, 242 of the keys are associated with Identity and Access Management (IAM) users with the AdministratorAccess policy. This role has full permissions to create, modify, delete, and view virtually all AWS services and resources within an account.
They note that each key of the 768 live keys in the two sets contains “full control of an organization’s AWS account.”
The company found 431,875 AWS secrets in code repositories, Git histories, datasets, Docker images, registries, and CI logs, and extracted 64,024 unique AWS keys corresponding to 50,654 AWS accounts after removing duplicates.
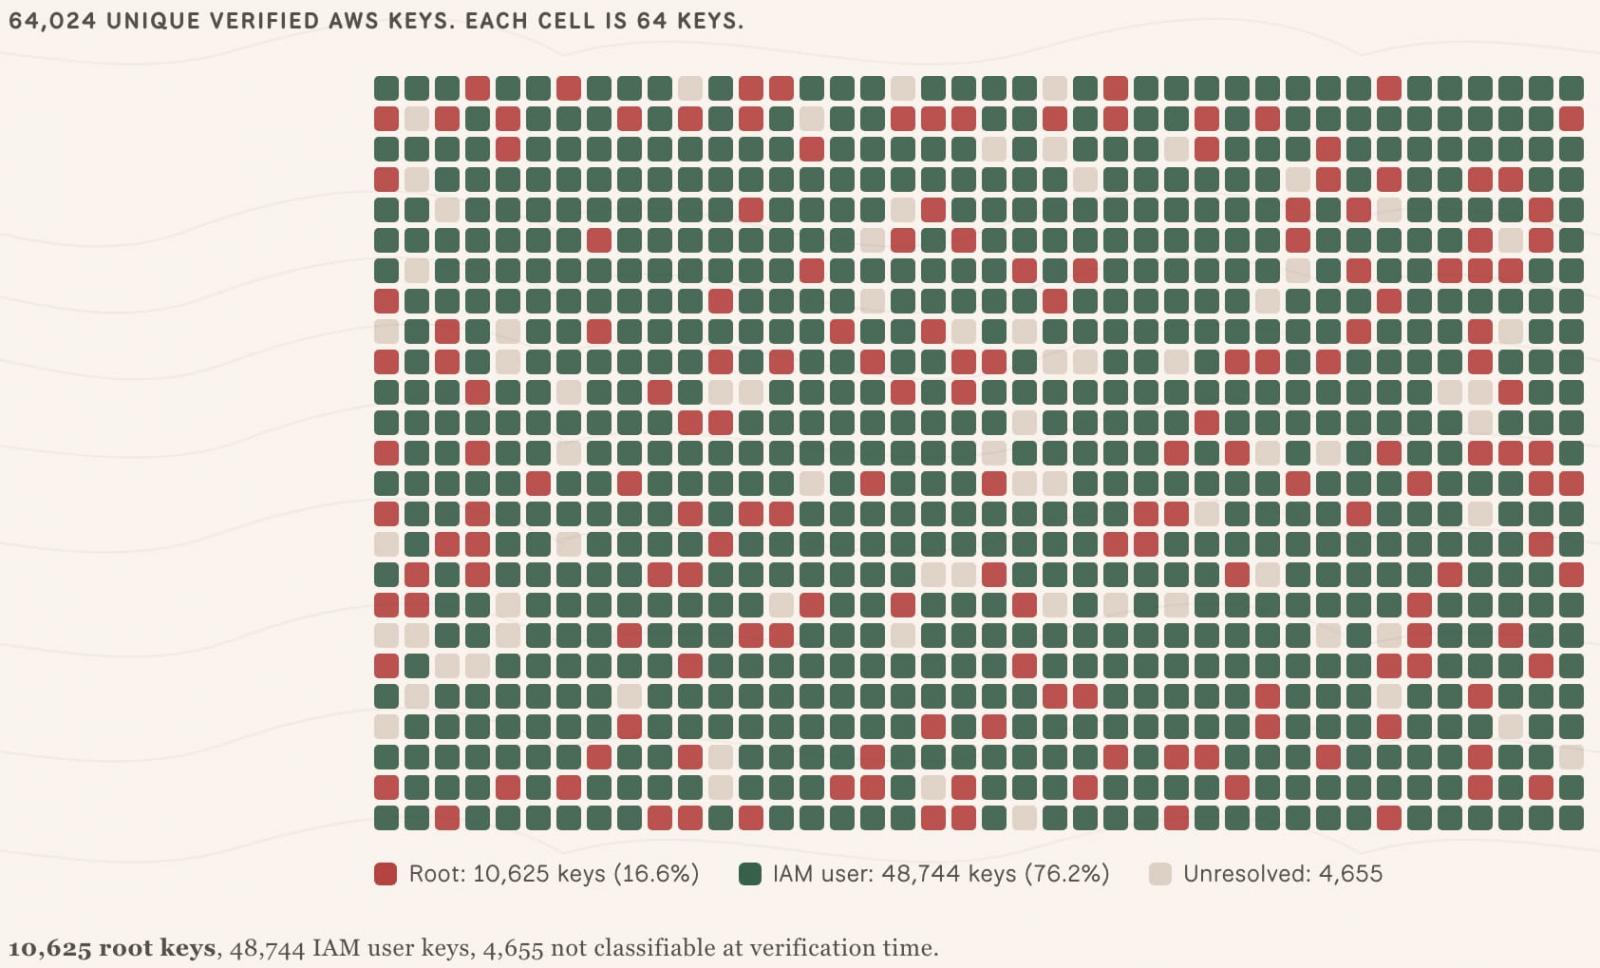
Source: Truffle Security
However, the subset for which researchers had complete credentials that could be used for re-verification was 10,616 keys, and 88% of them continued to authenticate as of August 10.
Amazon Web Services (AWS) is Amazon’s cloud computing platform that companies use to host websites and applications, store data, operate databases and servers, manage domains, and operate their online infrastructure.
Complete control of a company’s AWS account could allow an attacker to access, exfiltrate or delete data hosted in the cloud, take control of servers and applications, and create fraudulent administrator accounts for persistent access
Threat actors could also use their access to deploy cryptominers, which would incur significant costs to the company. Truffle Security says that only 262 of 2,754 readable accounts had a budget alert set up.
Hugging Face, a popular online platform where developers share AI models, datasets and applications, was the single largest source of leaked AWS keys, with 8,482 unique key revelations.
Additionally, 17.9% of these keys were root keys, which is the highest privileged identity that is not restricted by IAM permissions.
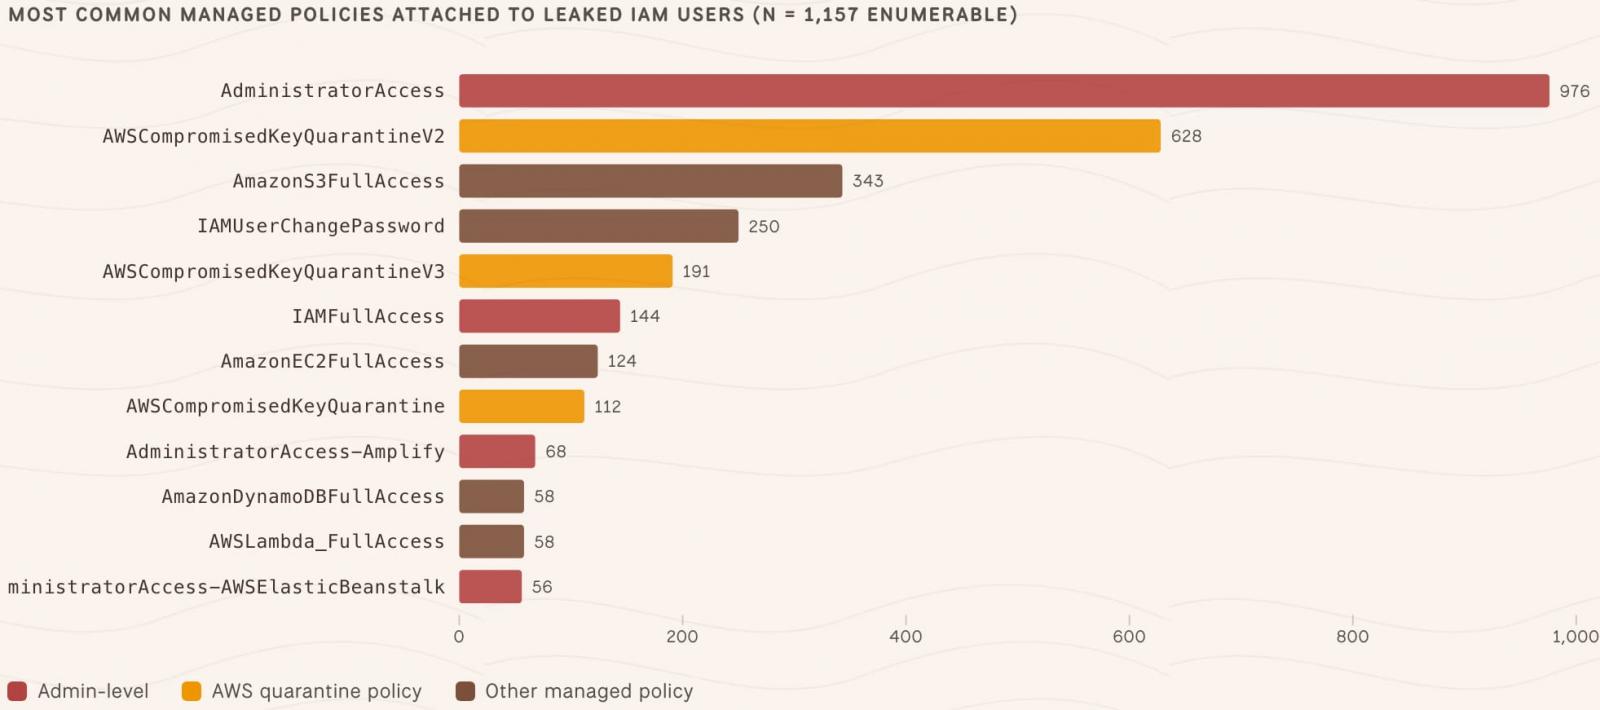
Source: Truffle Security
Truffle Security found that the average age of the 2,903 keys with available creation dates was 1,831 days (about five years), while the oldest key had existed for 17.4 years.
Only 398 (13.7%) of these entries had a newer access key assigned to the same user, suggesting that most were never rotated.
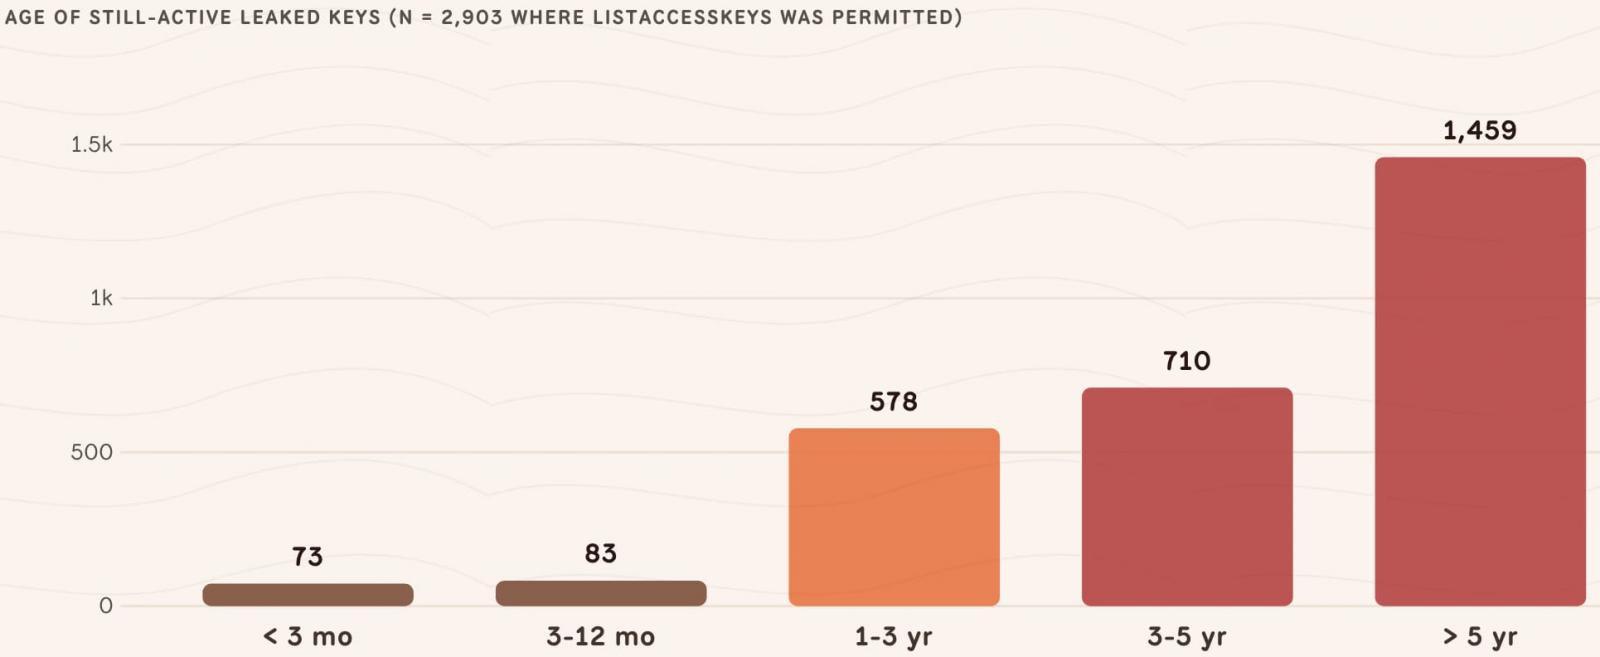
Source: Truffle Security
To prevent potential abuse, researchers recommend deleting all root access keys, checking IAM credentials by age, rotating or revoking exposed keys, and configuring budget alerts.
Additionally, any credentials shared with a public source should be treated as compromised.
Truffle Security said testing was limited to read-only metadata and all identifiable owners of exposed credentials were notified.

Overall prevention scores can hide what happens after the first access. Once attackers use valid credentials, prevention drops sharply.
The 2026 Blue Report measures defense technology for technology in 338 million simulations conducted in customer production environments.



