Cryptocurrency hardware wallet provider SafePal is warning of a data breach affecting around 39,798 customers after a flaw was used to steal customer order information, and a threat now claims to be selling the stolen data.
SafePal says the breach affected customers who placed orders between March 2, 2025 and April 11, 2026, exposing their names, email addresses, shipping addresses, phone numbers and purchase information.
The company says the breach did not expose customers’ home wallet phrases, private keys, passwords, bank account information, payment card numbers, government-issued identification numbers or other credentials.
“No evidence was found that the incident itself compromised access to SafePal wallets or funds,” SafePal said in security tips published on Sunday.
The company says it notified all affected customers via email on Aug. 16 with the subject line “(Important) Your SafePal order information has been affected.”
SafePal also launched online verification tool which allows customers to enter their order number and country of delivery to determine if the details of that order have been stolen.
The company warns that the stolen information can be used to conduct targeted phishing and other social engineering attacks, with customers reporting phishing emails and phone calls to SafePal as far back as May.
Order tracking flaw exposes customer data
A threat actor now claims to be selling the stolen SafePal customer data on a cybercrime forum.
As observed by DarkWebInformerthe seller listed the same affected order period and approximately 39,798 customers discovered by SafePal.
For potential buyers, the threat is also willing to share order ID and shipping country information from stolen orders, which can be verified through SafePal’s online verification tool as proof that the sale is legitimate.
“I’m not interested in low balls, please come right and at a good price or don’t message me at all,” the forum post reads.
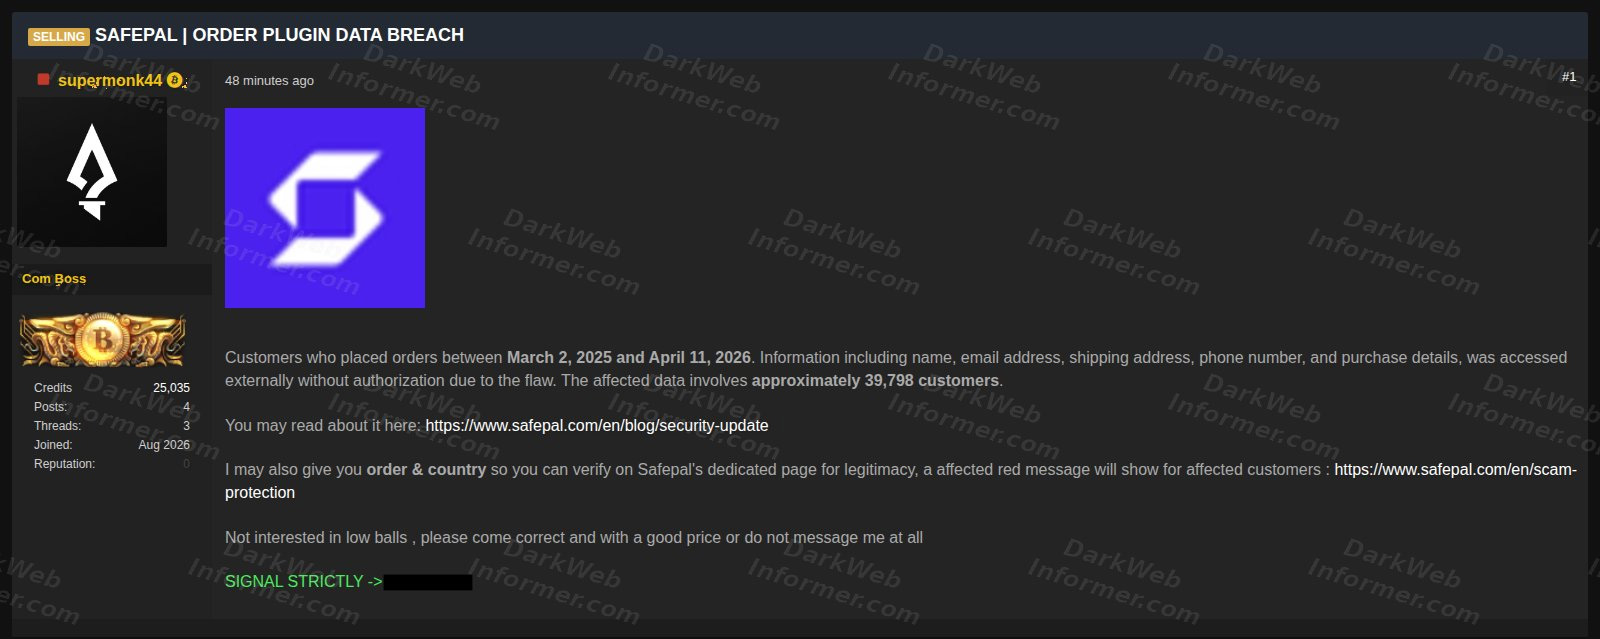
Source: DarkWebInformer
BleepingComputer has not independently verified whether the threat possesses the stolen data.
SafePal says it first received a report consistent with the incident in early May 2026, which it initially treated as an isolated incident.
Although it is not clear if this report is related to a client published on X that they received a phishing email from SafePal and a phone call from someone claiming to be an employee of the company in May. The phishing email claims that a security vulnerability has been discovered in the SafePal X1 hardware wallet and that a firmware update is required to fix the flaw.
“We first received a report consistent with this issue in early May and treated it as an isolated incident at the time, but have escalated it into a formal security investigation and put additional safeguards in place,” the statement said.
“Because our e-commerce system includes multiple interconnected components and external integrations, as well as third-party logistics partners, we cannot immediately rule out several possible explanations.”
In July, SafePal began what it described as a “complete review and overhaul” of its order processing system and discovered an authorization flaw in a plugin’s order tracking feature that allowed unauthorized access to another customer’s order information.
SafePal says it has patched the vulnerability and implemented additional security measures. The company is also working with a third-party security firm to confirm the patch and conduct a broader review of its order processing systems.
However, as part of this investigation, SafePal determined that a threat used the vulnerability to steal order information belonging to approximately 39,798 customers.
During the investigation, SafePal also discovered a separate configuration error that caused the data cleansing process to stop functioning properly between September 2025 and April 2026, resulting in order data being retained as far back as March 2025.
For affected orders, SafePal says it has scrubbed personal data from active e-commerce servers, although it retains an encrypted offline copy for potential law enforcement investigations.
SafePal also warns customers to watch for targeted phishing emails and phone calls regarding firmware upgrades, product returns, refunds or legal investigations.
The company says it has already taken down more than 30 fraudulent websites and phishing links linked to this incident.
Customers whose order information was exposed should not change their hardware wallets or move cryptocurrency due to the breach, according to SafePal.
However, if a customer has already shared their passphrase or private key in response to a phishing email or text, they should treat their wallet as compromised and transfer all assets to a new wallet on a trusted SafePal device or official app.

Generic prevention scores can hide what happens after initial access. Once attackers use valid credentials, prevention plummets.
The 2026 Blue Report measures security techniques by techniques in 338 million simulations run in customer production environments.



