Oil giant Shell has confirmed it is investigating a possible security incident after the Clop ransomware gang claimed to have stolen 89GB of data.
Shell is a British multinational energy company and one of the three largest oil and gas companies in the world after Chevron and ExxonMobil. The company employs 85,000 people in more than 70 countries and operates a vast network of tens of thousands of service and charging stations, serving over 20 million customers every day.
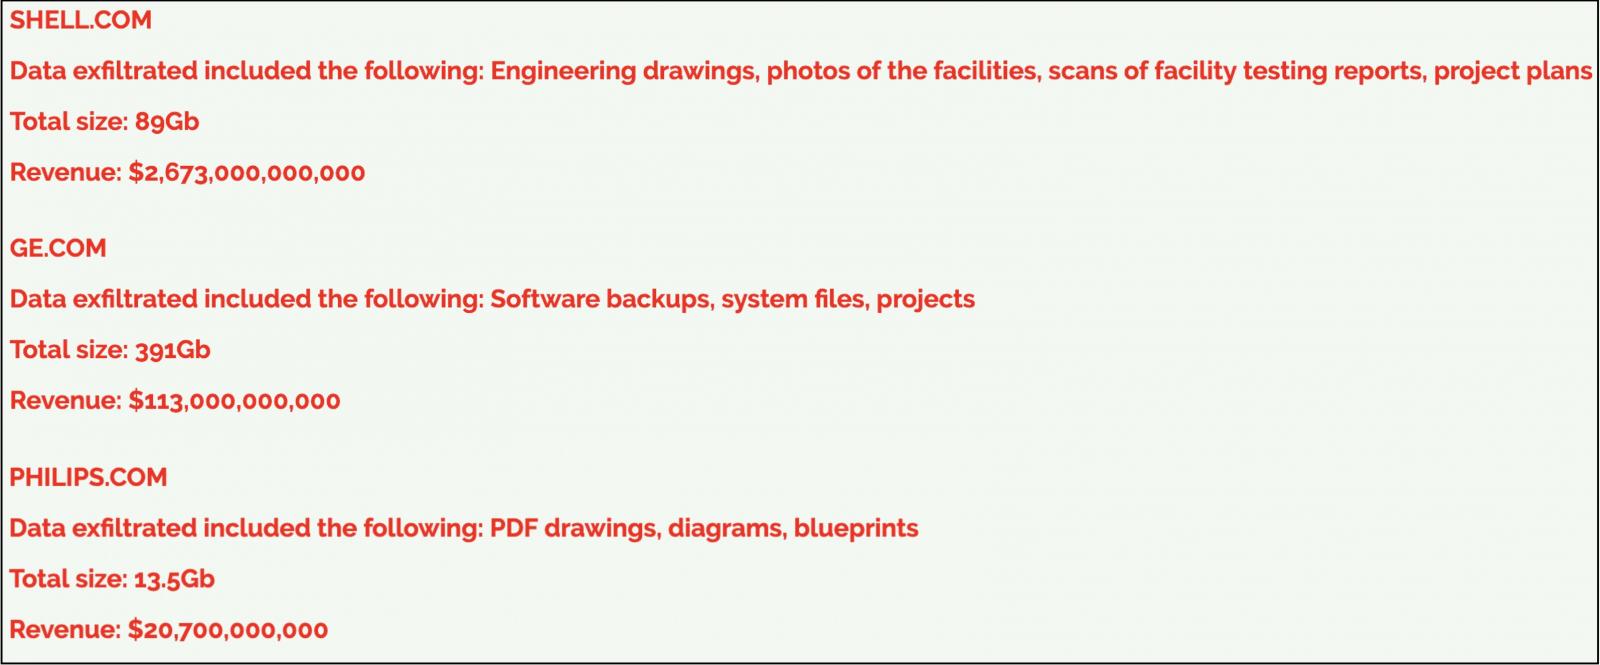
According to a recent post on Clop’s dark web data leak page, the allegedly stolen files include technical drawings, scans of equipment test reports, photos of the equipment and project plans.
“We are aware of a possible incident. We are working with our security teams and relevant experts to investigate,” a Shell spokesperson told BleepingComputer when asked to confirm Clop’s claims of data theft.
While the company has not yet shared any further information, the Clop gang has listed it on its leak site as one of 43 new victims likely to be the target of data theft attacks on web-accessible PTC Windchill and FlexPLM instances that exploit a critical improper input validation vulnerability known as Tracked CVE-2026-12569.
As part of the same attacks, Clop also claimed to have stolen sensitive data, including backups, system files, projects, drawings, diagrams and blueprints, from the networks of technology giants General Electric and Philips.
Spokespeople for GE and Philips were not immediately available for comment when contacted by BleepingComputer today. A PTC spokesman also has not yet responded to a request for comment.
PTC began Release of security patches CVE-2026-12569 on June 17 and although it did not confirm exploitation in the wild, it also published one private advice We encourage customers to scan environments for Indicators of Compromise (IOCs).
After PTC warned customers of “increased threat activity” on June 26, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) also confirmed that the vulnerability was being actively exploited in attacks. add it too the “Known Exploited Vulnerabilities” catalogue, and directing federal agencies to secure their PTC Windchill and FlexPLM instances within three days.
CVE-2026-12569 too prompted the German authorities to take immediate actionwith the Federal Office for Information Security (BSI) warning PTC customers in the middle of the night to patch their systems as quickly as possible.
Clops Windchill and FlexPLM attacks have also been confirmed the Ransomware Information Sharing and Analysis Center (Ransom-ISAC)a non-profit organization dedicated to tracking and preventing ransomware threats, and by Cybersecurity company ReliaQuestIt says that the threat actors deployed JSP webshells that allow them to steal sensitive data from victims’ compromised PLM platforms.
PTC FlexPLM and PTC Windchill are enterprise software platforms in the Product Lifecycle Management (PLM) category that are used to track, design, and manage products through final manufacturing.
The two systems are popular with engineering, manufacturing, quality and supply chain teams at major aerospace, defense, automotive, heavy engineering, retail and medical companies. PTC says its products are used by over 30,000 customers worldwide, including more than 1,500 brand and retail customers using FlexPLM.

Overall prevention scores can hide what happens after the first access. Once attackers use valid credentials, prevention drops sharply.
The 2026 Blue Report measures defense technology for technology in 338 million simulations conducted in customer production environments.



