A maximum severity SAP Commerce Cloud remote code execution vulnerability patched three days ago is now under attack, according to threat intelligence firm Defused.
Commerce Cloud (formerly known as SAP Hybris) is a cloud-based e-commerce platform used by online stores owned by well-known global brands and large retailers.
Tracked as CVE-2026-58231this critical flaw stems from an incorrect authorization weakness in the core Data Hub Adapter extension for Commerce Cloud, which unprivileged threats can exploit in low-sophistication attacks to execute arbitrary code.
“SAP Commerce Cloud allows an unauthenticated attacker to abuse the default authentication client and submit a specially crafted login to certain functions without sufficient validation,” explains SAP.
“Successful exploitation could enable arbitrary code execution and compromise internal components, resulting in severe impacts to application privacy, integrity and availability.”
While SAP has not yet flagged this security flaw as being actively exploited in a security tips issued this Tuesday, Defused security researchers confirmed earlier today that CVE-2026-58231 is now targeted in the wild.
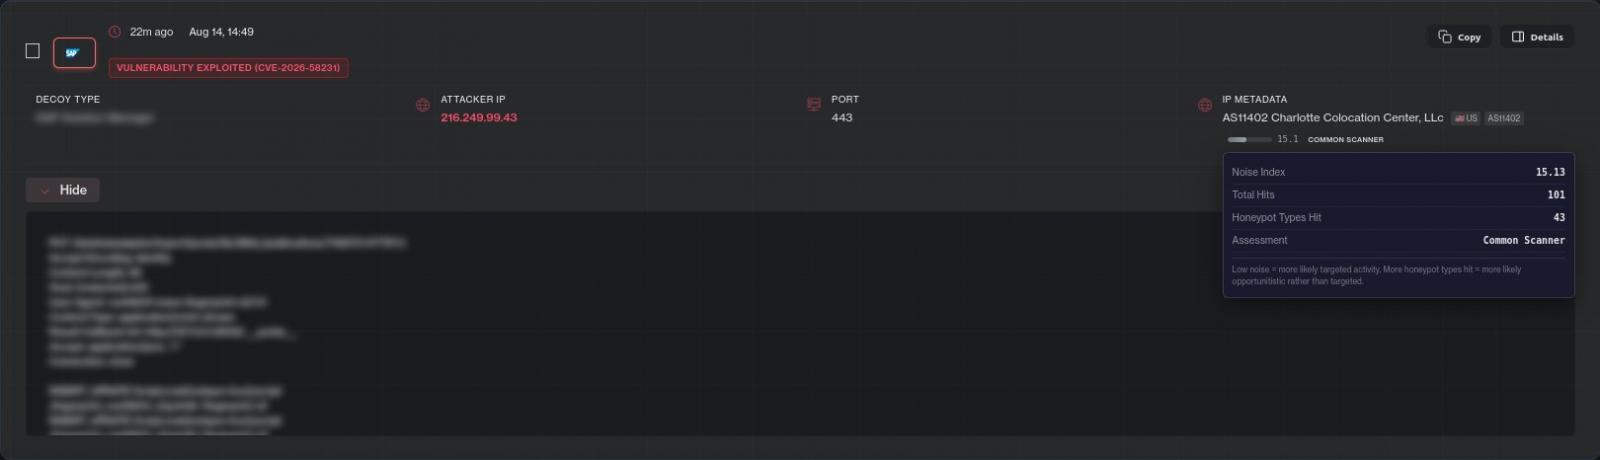
”First exploit attempts against CVE-2026-58231 (Unauthorized RCE in SAP Commerce Cloud, CVSS 10.0) are already hitting our honeypots – 3 days after patch day,” Defused warned in a tweet on Friday. “This vulnerability has no public PoC and is not known to be exploited.”
A SAP spokesperson told BleepingComputer that the company is aware of and looking into this issue when asked to confirm Defused’s report.
“Security note https://me.sap.com/notes/3771065 is published and available to SAP customers and partners and was released on SAP’s August Patch Day. We recommend that customers and partners patch their systems with immediate effect,” the spokesperson added.
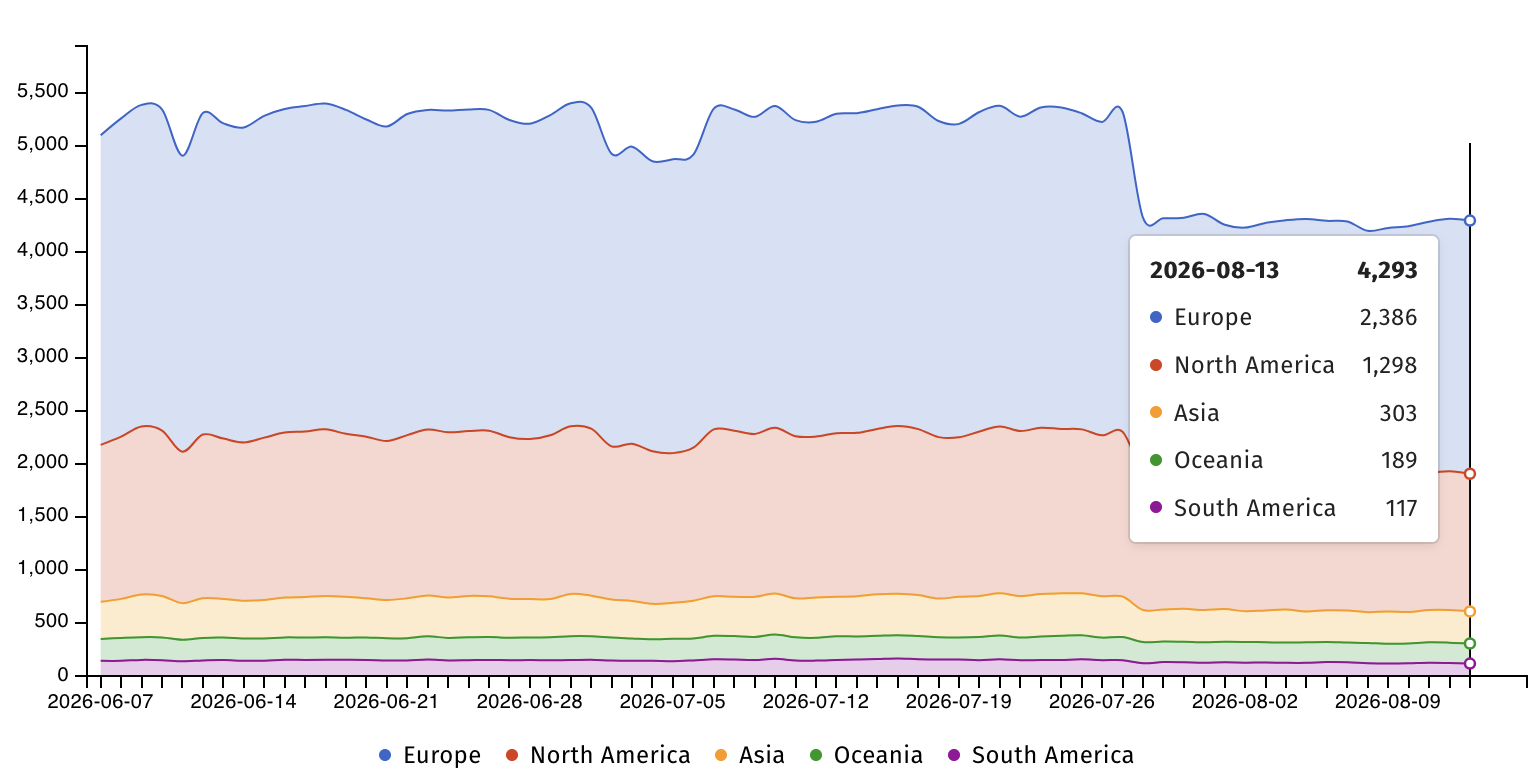
Internet security monitoring group Shadowserver tracks over 4200 IP addresses with SAP Commerce Cloud fingerprintmost of which from Europe and North America.
However, there is no information on how many of them are honeypots or have already been protected against CVE-2026-58231 attacks.
Most recently, SAP patched 16 vulnerabilities in its July 2026 security patch package and another 30 vulnerabilities in June and May, including three more critical security flaws (CVE-2026-44761, CVE-2026-22732and CVE-2026-34263) affecting Commerce Cloud’s enterprise-level e-commerce platform.
In April, cybersecurity companies Aikido and Socket also reported that attackers aiming to steal credentials from developer systems compromised multiple official SAP npm packages in a supply chain attack.
From November 2021, the US Cybersecurity and Infrastructure Security Agency (CISA) added 14 SAP vulnerabilities to its catalog of known exploited vulnerabilities, including three that have been exploited in ransomware attacks.
SAP is a German multinational software corporation that serves 99 of the world’s 100 largest companies and has reported total revenues exceeding €36 billion in fiscal year 2025.
Update Aug 14, 11:51am EDT: Added SAP statement.

Generic prevention scores can hide what happens after initial access. Once attackers use valid credentials, prevention plummets.
The 2026 Blue Report measures security techniques by techniques in 338 million simulations run in customer production environments.



