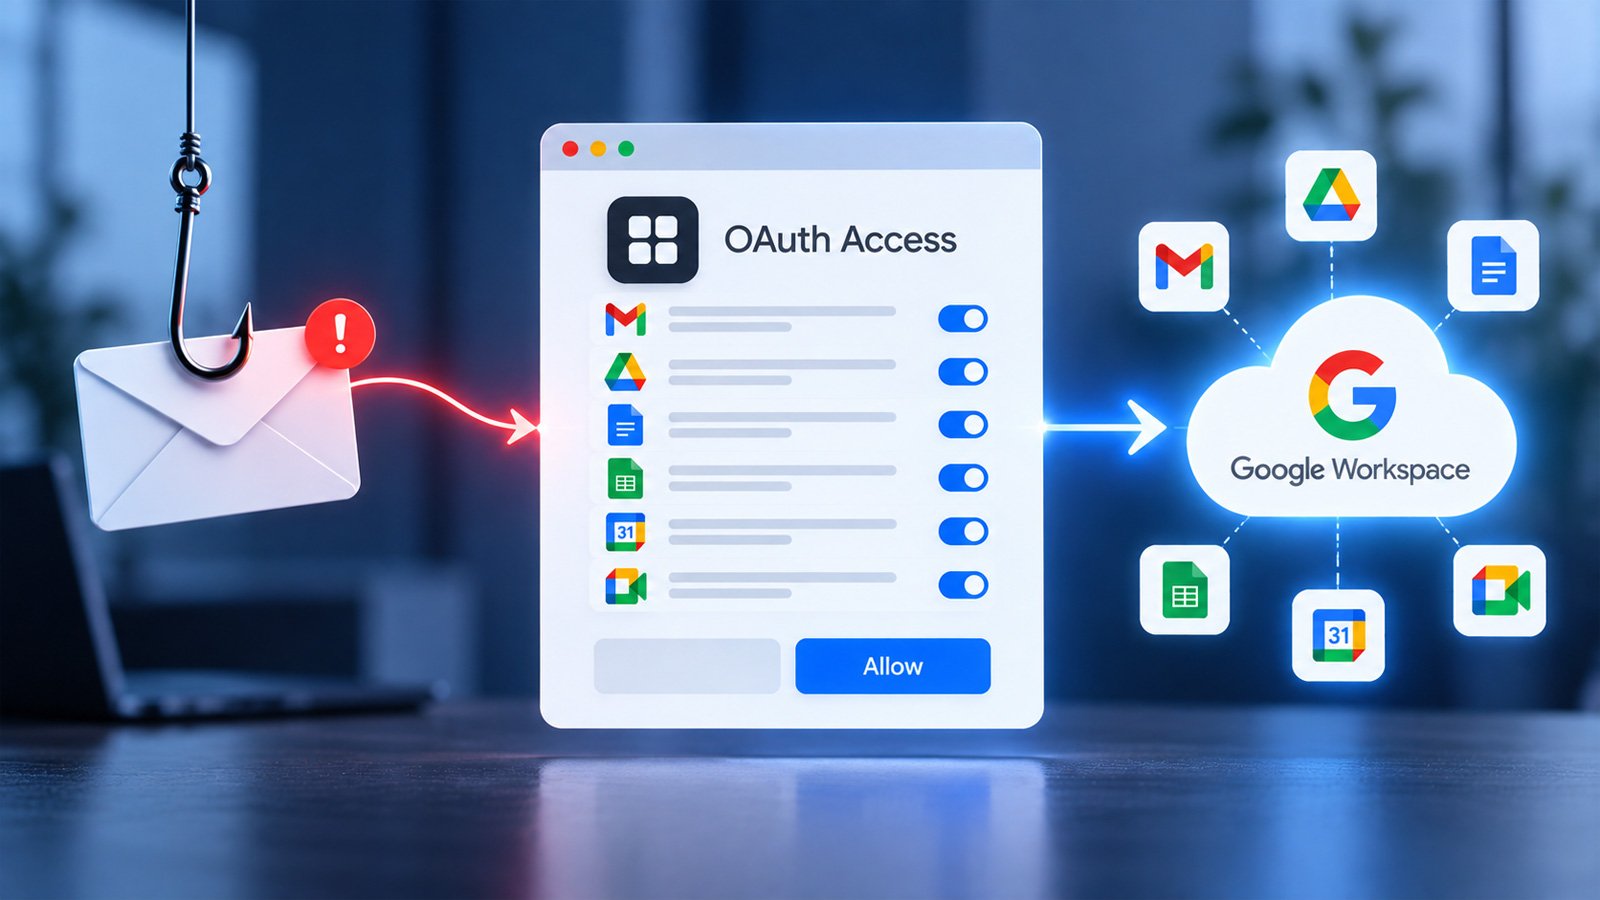
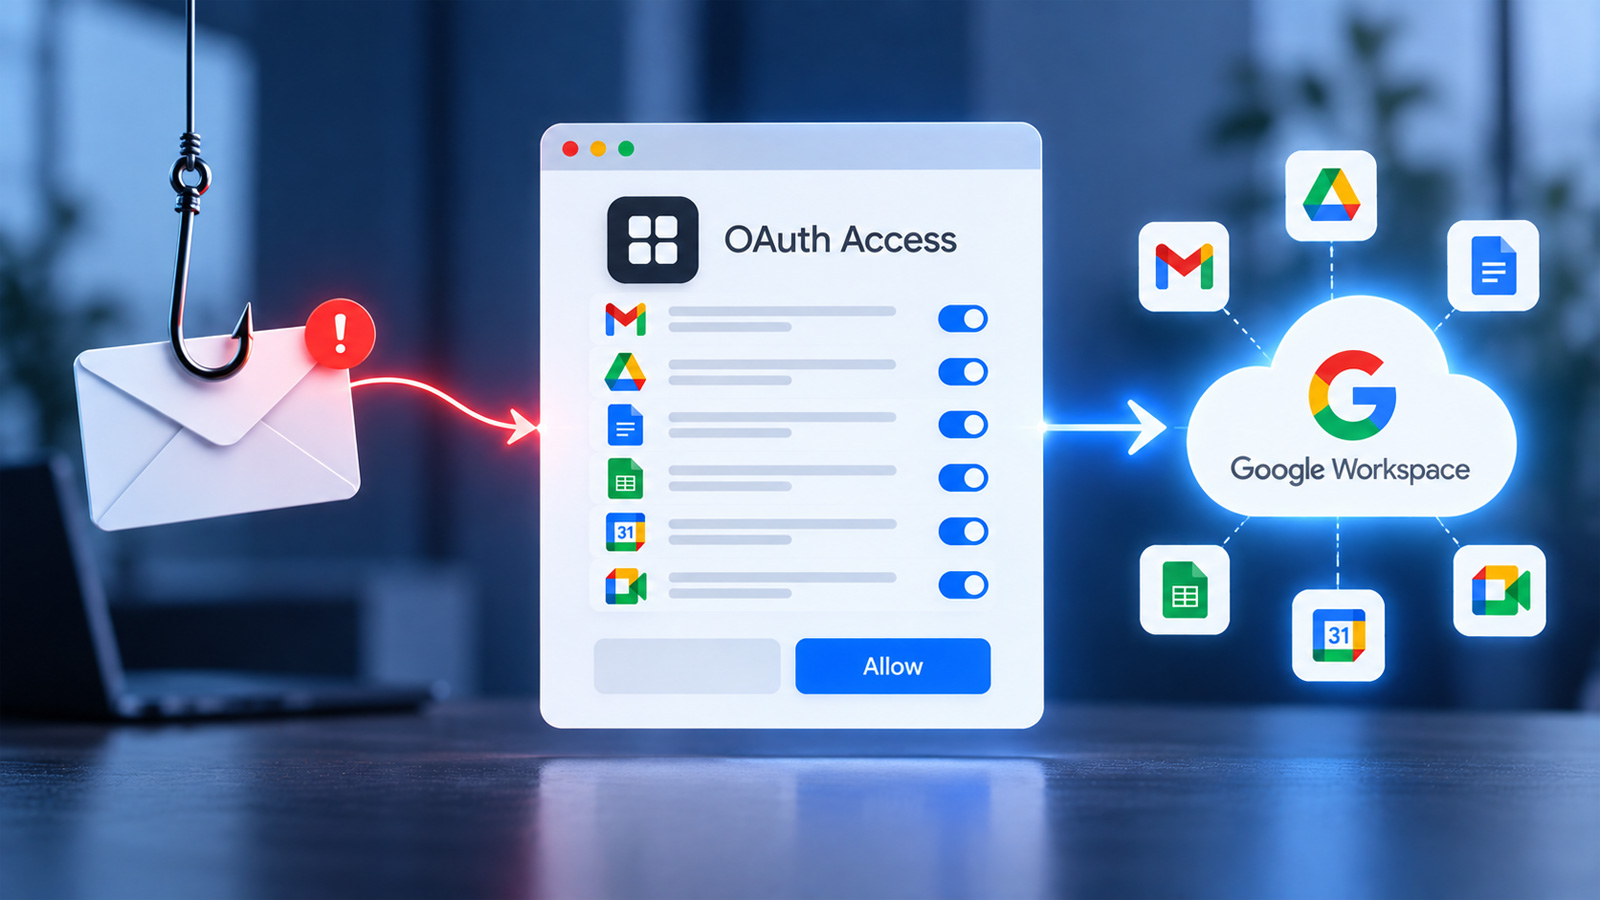
Google Workspace attackers don’t necessarily need to exploit a software vulnerability or steal a user’s password to gain access to an organization’s data.
On September 23, 2026, BleepingComputer will host a live webinar titled “Security Breach Autopsy: How Fast-Growing Companies Are Under Attack by Google Workspace” with material security.
In the webinar, Rajan Kapoor, vice president of security at Material Security, and Rick Fitzgerald, president of Fireside Consulting LLC, will examine two attacks that used malicious OAuth applications and social engineering to penetrate Google Workspace environments.
With OAuth, users can grant applications access to Google Workspace data and services without sharing their passwords. While this makes it easier for legitimate applications to connect to Google Workspace, attackers can also abuse the authorization process by tricking users into granting permissions to malicious apps.
Instead of stealing credentials, attackers can use social engineering to trick a target into authorizing an application, potentially gaining access to sensitive information available through user-approved permissions.
These attacks illustrate why to protect Google Workspace, organizations need to look beyond passwords and traditional authentication controls and understand which applications have access to their environment.
During the webinar, speakers will explain the sequence of events of the two attacks, the weaknesses that allowed them to succeed, and the decisions organizations made in the critical first hours of the incidents.
Attendees will also learn which security controls provide the most value for fast-growing companies and what speakers’ priorities would be if they were building a Google Workspace security program from the ground up.
When attackers trick users into granting access
Social engineering attacks often involve tricking users into revealing passwords or other credentials. Malicious OAuth apps offer attackers another approach: they can trick the victim into authorizing access instead.
A user may believe they are connecting to a legitimate application or responding to a trusted request, when in reality they are granting permissions to a malicious app in their Google Workspace environment.
The resulting access depends on the permissions granted, but the attack shows why organizations need visibility into third-party applications and the access that users are allowed to authorize.
By examining two attacks that combined malicious OAuth applications with social engineering, this webinar provides practical insight into how these breaches occur and what defenders can do to reduce their exposure.
The upcoming webinar will cover:
- How attackers combine social engineering and malicious OAuth applications to attack Google Workspace environments
- How users can be manipulated into authorizing application access
- What happens in the first hours of a Google Workspace breach and what response decisions are most important?
- Which security controls provide the most value for fast-growing companies with limited security resources?
- Practical security improvements that companies can implement quickly, sorted by effort and potential impact
Join us to learn how malicious OAuth applications and social engineering can lead to Google Workspace breaches and what organizations can learn from real-world attacks.



