According to Google’s Threat Intelligence Group (GTIG), both criminal and state-sponsored attackers are increasingly using AI to automate and scale their attacks.
What began as a relatively simple adversary instant injection into companies’ AI systems has evolved into a full-blown war, with attackers developing and deploying their own AI systems and companies deploying additional AI defenses that provide an expanded attack surface. It is an ongoing and expanding cycle that is unlikely to go away.
Google, which is on both sides of this war (partly a cause of Gemini’s development, partly a defensive measure in its efforts to detect and eliminate attackers), has done so recorded the development until 2026.
The overall effect of this automation is increased attack speed, and TeamPCP (UNC6780) provides an example. “The threat actor used an AI coding chatbot, a command prompt, and a set of agent instructions to plan, create, and execute a mass credential collection campaign in under six hours,” Google researchers say.
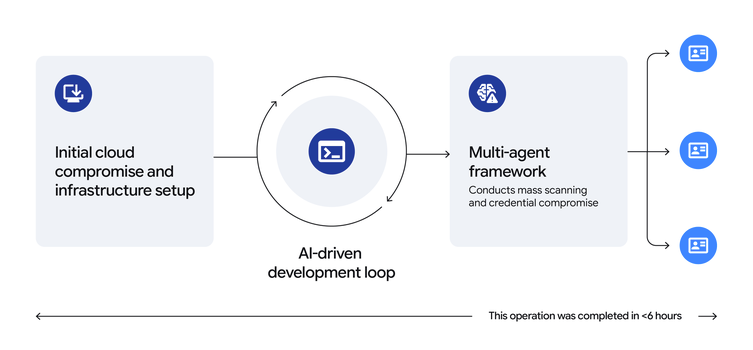
The use of AI allows attackers to operate on a scale typically associated with larger and better-resourced groups, such as those affiliated with nation-states.
TeamPCP is also used to highlight the increasing severity of threat actors’ exploitation of AI and the open source supply chain. Since March 2026, the actor has been carrying out such compromises against targets such as PyPI, npm and Docker Hub. The company has also implemented more than half a dozen different methods to target or exploit AI tools and open source software development practices, some of which are embedded in its Dustmaker credential stealing software.
TeamPCP has also developed Shai-Hulud and Miasma, both of which are publicly available. GTIG believes that “the publicity, apparent success, and open source release of the UNC6780 malware will likely lead adversaries to emulate these tactics.”
The group is just one of many players that are also using AI as a force multiplier for their activities. When a cybersecurity attack is a firefight, AI fuels the fire. But it’s not just financially motivated criminals who benefit from this – nation-state actors are also increasingly making use of AI.
In June 2026, GTIG reported on a multi-year cyber espionage campaign by UNC6508, a threat actor in the People’s Republic of China (PRC) nexus, targeting academic, medical and military research institutions in North America.
GTIG has also identified various nation-state actors interested in developing offensive agent AI tools. A group from the PRC experimented with AI-powered development tools to build an AI-powered, automated exploitation and post-exploitation pipeline.
PRC-nexus Basin Castle was observed querying LLMs to profile high-value targets during the early reconnaissance phase, design and translate localized social engineering decoys, create obfuscated custom malware, and troubleshoot post-exploitation commands.
Calanque Ion (also known as APT42), an Iranian-backed group, has used genetic AI (including Gemini) to identify target email addresses, conduct OSINT research, and translate content into local languages to create localized pretext decoys.
Ravine Castle (aka APT24), aka PRC-Nexus, leverages Gemini across the entire attack lifecycle, from intelligence gathering to developing attack capabilities to influencing operations. It has also been observed that twins have been used to create politically charged propaganda; Research methods for anonymizing data leaks for downstream dissemination to journalists and social media influencers.
Midnight Neptune (UNC1069) is a North Korea nexus actor that has increasingly integrated AI into its operational lifecycles to support cryptocurrency theft.
Google’s response to this increase in AI-powered attacks is to disrupt adversary operations by disabling associated projects and accounts as soon as they are identified. It also hardens its own models against abuse; For example: “In response to model extraction or ‘distillation’ attacks, we have deployed real-time defensive measures designed to degrade the performance of unauthorized ‘student’ models and to detect attempts to clone proprietary logic.” (See details from CISA on China’s distillation attacks against U.S. border AI companies here.)
However, the fundamental problem lies in AI’s ability to find vulnerabilities and develop new malware and exploits. As long as this continues, malicious actors will use AI as a force multiplier for their activities. There will never be a shortage of vulnerabilities – as quickly as they are found and fixed, they will be replaced by other vulnerabilities in new software. Good actors like Google can detect and disrupt adversary activity, but the bad actors will move, adapt and move on. This has been the pattern in cybersecurity since the advent of the Internet – only the details change. The AI introduces many more details and increases the speed and scope, but the basic warzone remains and will likely remain unchanged.
Related: AI drives “industrial” cybercrime as time to exploitation shrinks to hours
Related: Google DeepMind introduces framework for exploiting AI’s cyber weaknesses
Related: The UK Cybersecurity Center says “deepfakes” and other AI tools pose a threat to the next election
Related: Cyber Insights 2026: Cyberwar and Growing Threats from Nation States



