An Advance Passenger Information System (APIS) database containing more than 220 million passenger and crew records, including passport numbers and flight details, was accessed online through a chain of security misconfigurations. The system appears to be linked to a Vietnamese organization, according to the researchers who discovered it.
Advance Passenger Information Systems are used around the world to collect identity, passport and flight information from airlines before passengers and crew arrive or depart a country.
The exposed records cover the period from January 2017 to April 2026 and may include passengers of many nationalities flying to, from or through Vietnam during that period.
Nine years of passenger and crew data
Kinryū Labs discovered the Elasticsearch cluster on June 3 while examining open databases as part of an investigation into ransomware activity.
The cluster named “pax-info” contains 29 indexes and approximately 107 GB of data. Its two main indexes contained 210,318,069 passenger records and 10,465,631 crew records, for a combined 220,783,700 records.
According to Kinryū Labs, the cluster is hosted in an IP space assigned by Viettel in Hanoi. BleepingComputer could not confirm which Vietnamese organization runs the system.
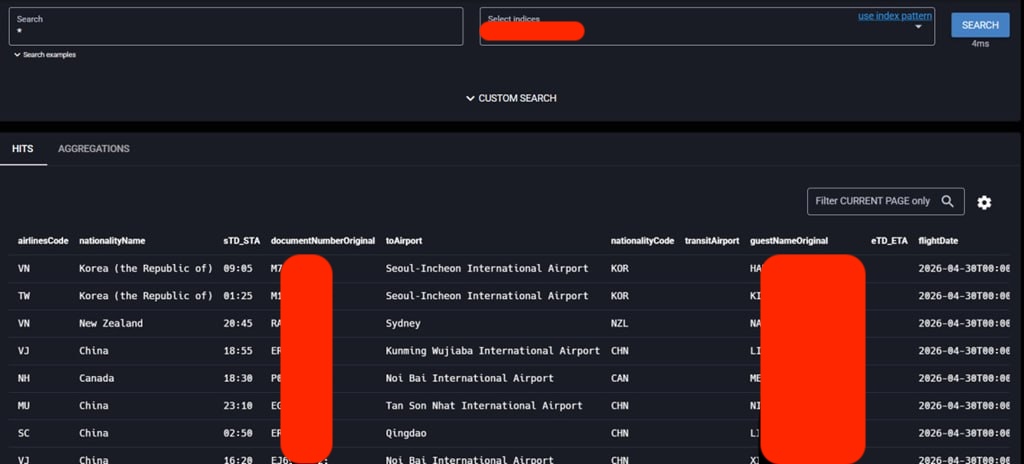
The information disclosed includes names of passengers and crew members, dates of birth, gender, nationality, passport or travel document numbers, expiry dates of the documents and issuing countries.
Related travel data includes flight numbers and dates, airlines, departure, destination and transit airports, seat allocations, baggage claim and schedule, expected and actual flight times, information typically carried by APIS and related airline systems.
Sample records reviewed by BleepingComputer include travelers with Korean, Chinese, Canadian and New Zealand nationalities, among others.
(Kinryū Labs)
Although the researchers were unable to provide a complete breakdown by nationality, the data covered multiple international airlines in the Asia-Pacific region, Europe and the Middle East. As a result, the records discovered can relate to people from almost anywhere who visited or passed through Vietnam during the nine-year period.
Kinryū Okay confirmed that the information was legitimate by matching database entries with its researchers’ own trip to Vietnam.
The numbers represent travel records, not unique individuals. Passengers and crew members who have flown multiple times may therefore appear multiple times in the database.
Database accessible via chained misconfigurations
Kinryū Labs told BleepingComputer that it reached the database by chaining together two incorrect configurations.
From the open Internet, the endpoint returned an HTTP 401 “Unauthorized” response, preventing direct access to the database. However, a cloud path allowed researchers to reach the cluster, which then assumed default credentials.
Internet intelligence platform FOFA first recorded the host and port in October 2022 and identified the service as a database in July 2023. However, Kinryū Labs could not determine when passenger data first became recoverable during the second access path.
As a result, while the records themselves span over nine years, the actual length of exposure is unknown.
Kinryū Labs said it reported the problem to Vietnamese authorities, the airlines represented in the database and the country’s computer emergency response teams as of June 3. The researchers said access to the database was fixed on June 8.
A verified email reviewed by BleepingComputer shows that Singapore Airlines’ security team helped coordinate the response, informing Kinryū Labs on June 8 that it had “engaged the relevant parties” and “taken steps to contain the issue.” Singapore Airlines did not provide further comment to BleepingComputer.
The findings, shared with BleepingComputer, identified several major airlines whose passenger records appeared in the database. However, there is no indication that the airlines operated the exposed system or that their own networks were compromised.
Changi Airport Group, which manages and operates Singapore’s Changi Airport, told BleepingComputer it was investigating the case but declined to comment.
BleepingComputer also contacted Vietnamese authorities long before publication but did not receive a response.
It remains unclear whether the database was downloaded, sold, ransomed or otherwise exploited by malicious actors before it was secured. Kinryū Labs said it found no ransom notes or unknown indexes on the cluster and could not identify the dataset offered for sale online.
However, without access to the server’s log files, researchers cannot definitively determine whether anyone copied the data.
Kinryū Labs expects to publish additional technical findings about it blog later this week.

Generic prevention scores can hide what happens after initial access. Once attackers use valid credentials, prevention plummets.
The 2026 Blue Report measures security techniques by techniques in 338 million simulations run in customer production environments.



