A phishing-as-a-service framework called BigBear 2.0 was used to bypass multi-factor authentication at 258 organizations and steal more than 5,000 Microsoft 365 credentials.
Researchers at cybersecurity firm CloudSEK gained administrative access to the control panel and discovered that the service managed 42 VPS nodes, all of which were configured to target Microsoft 365 as part of the observed operation.
According to the researchers, the campaign uses an Evilginx2-based adversary-in-the-middle framework to intercept passwords and authenticated session cookies, allowing attackers to hijack accounts after victims complete the multi-factor authentication (MFA) process.
BigBear uses a configuration called “offy” that sets up a man-in-the-middle (AiTM) proxy between the victim and Microsoft’s legitimate authentication infrastructure.
This allows the attacker to capture credentials, including MFA, and session cookies and replay them via an API to hijack the victim’s authentication session.
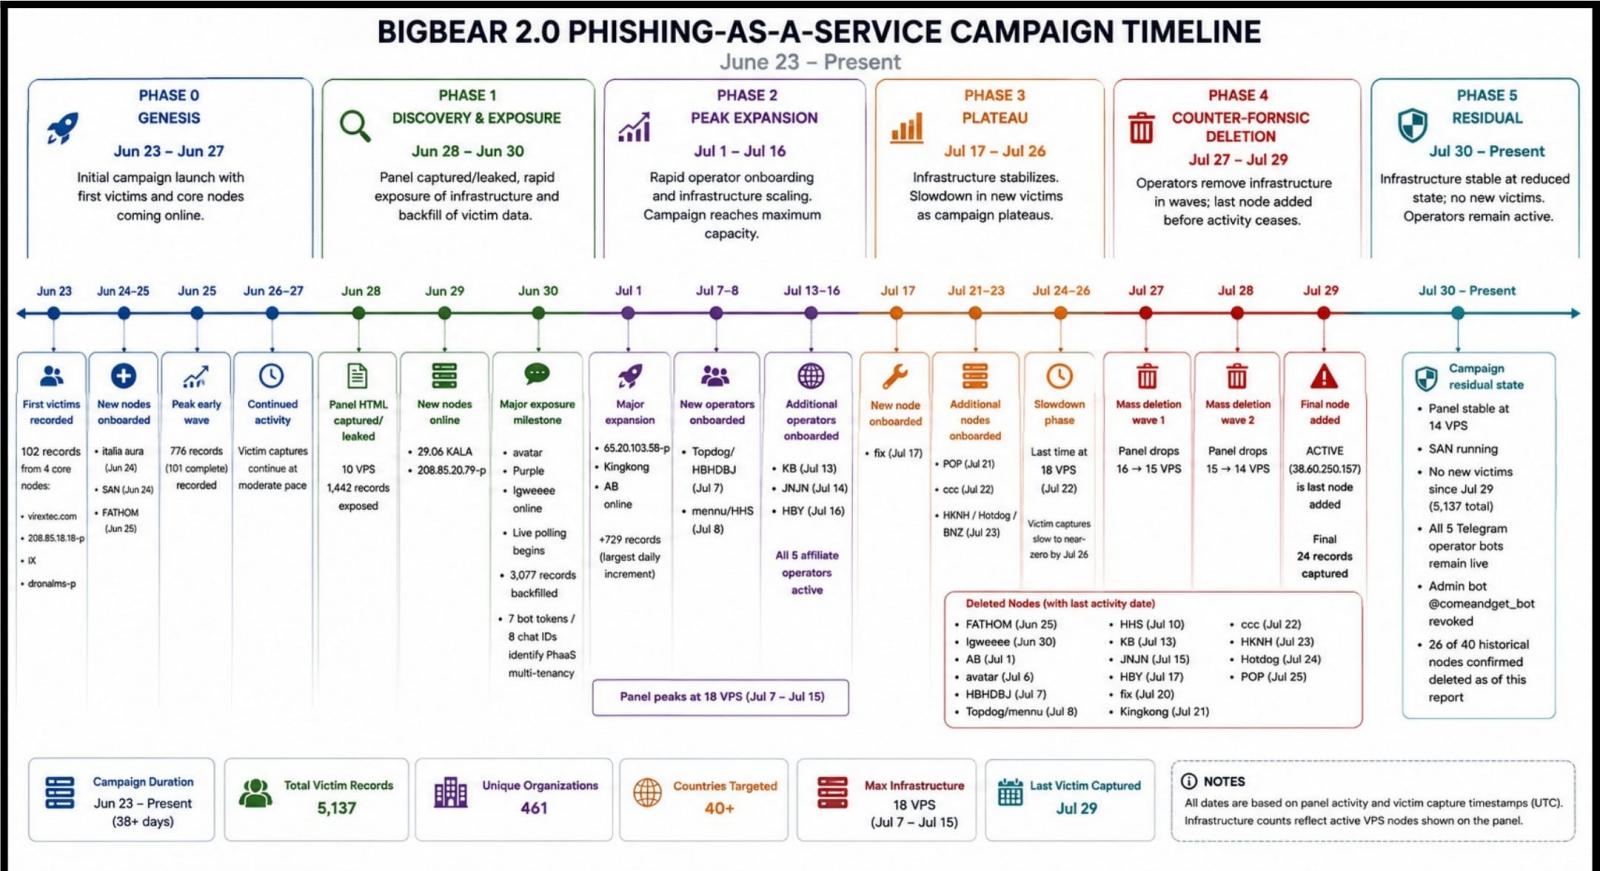
Source: CloudSEK
Microsoft 365 is Microsoft’s cloud productivity and identity ecosystem and includes services such as Exchange Online, Teams, SharePoint, OneDrive and Entra ID authentication.
Compromising an authenticated Microsoft 365 session can expose emails and files while potentially allowing access to other applications connected via single sign-on.
According to CloudSEK, BigBear proved successful enough to compromise hundreds of entities and capture thousands of cookies.
“The panel exfiltrated 5,137 credential records – including 474 full MFA bypassed authentications, 1,032 plaintext passwords and 4,148 session cookies – affecting 3,331 unique victim IPs in over 40 countries, with the operation still active at the time of writing.” CloudSEK says in a report shared with BleepingComputer.
“The multi-user PhaaS panel is leased to at least five affiliate operators identified by live Telegram exfiltration bots, each of which receives stolen credentials in real time.”
While 461 organizations appeared in the broader targeting dataset, CloudSEK clarified that 258 different organizations had at least one MFA bypass compromise completed.
CloudSEK also discovered that BigBear uses custom JavaScript that compromises FIDO2/WebAuthn authentication and disables corresponding browser functionality to force targets to use weaker authentication methods.
To increase its effectiveness, the platform uses geo-targeted residential proxies for 69 countries and matches the victim’s location with a residential IP address so that Microsoft’s authentication servers do not flag the activity as suspicious.
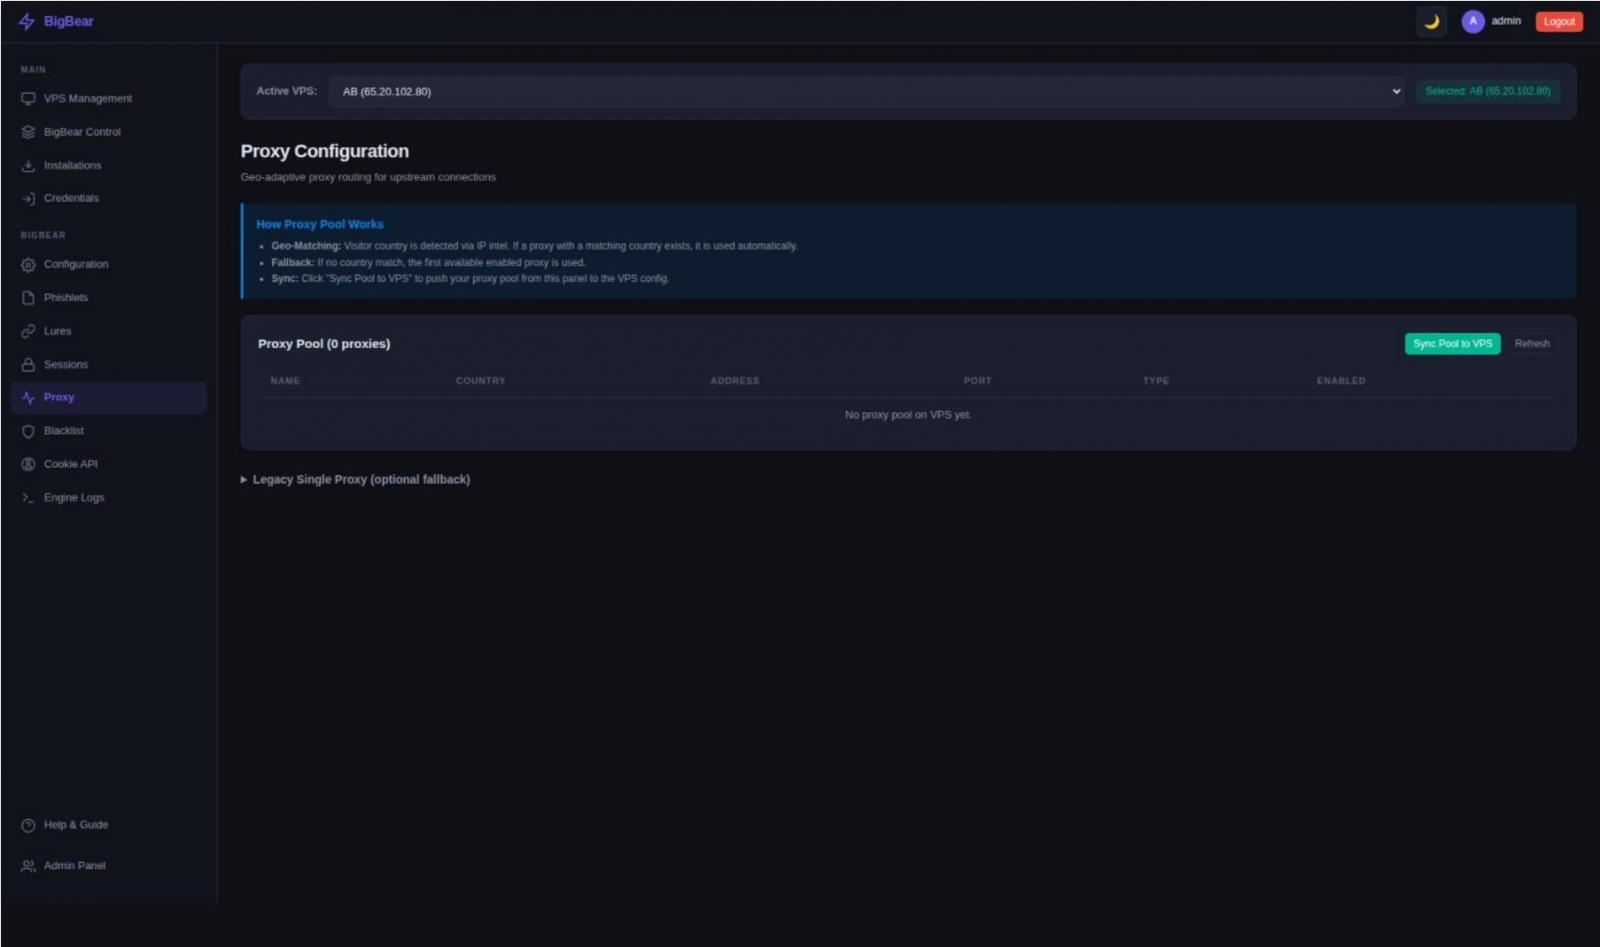
Source: CloudSEK
CloudSEK said it notified law enforcement and several affected organizations and included the credentials in disclosure reports.
At the time of writing, the administration panel is still online, while the phishing infrastructure has been offline for almost three weeks.
Organizations potentially affected by BigBear activity should reset exposed passwords, revoke active sessions, update tokens, and force re-authentication for highly privileged accounts.
It is also advisable to enforce phishing-resistant FIDO2/WebAuthn and use conditional access policies that require managed devices rather than relying on geolocation signals.

Overall prevention scores can hide what happens after the first access. Once attackers use valid credentials, prevention drops sharply.
The 2026 Blue Report measures defense technology for technology in 338 million simulations conducted in customer production environments.



