Of course, there is no shortage of network mapping and monitoring tools. There is one light package that I recently opened and finally passed the test. LAN Orangutan (what a name) has become one of my favorite fast Docker containers to run in my home lab. It has the potential for an early release that already does almost everything right. It deploys quickly, keeps things simple, and provides an efficient way to map and monitor networks.
When network scanners come in handy at home
This is not just a tool for enthusiasts

Network scanning is not for those who like to look at numbers, objects found, and see what is happening on the local network live. It is also valuable for everyone who interacts with customers and destinations online. Most devices on a typical home LAN obtain their IP address from the router’s DHCP server. A few IP addresses to remember is not a big deal.
But once you start self-hosting services and applications, get more hardware online, and even get into smart home territory, your LAN can quickly grow into triple digits. That’s when it becomes difficult to remember every address on the web. Spin up a new Linux container (LXC) or virtual machine (VM)? This will be another IP address to remember. Want to use VLANs to segment and control specific traffic? More IP addresses, please.
It does exactly what it says on GitHub.
This is where a network discovery tool like LAN Orangutan comes into play. I’ve used NetBox, Fing, Nmap and Angry IP Scanner for years. They’re all great, but LAN Orangutan caught my eye because it’s self-driving, simple, and lightweight. In fact, it doesn’t do much other than check the network and list all clients. Of course, this data may be available in the router software I use, but it looks much better and is more accessible.
Plus it gives me access to others because I don’t want anyone to access my router server right?
Setting up LAN Orangutan is easy
Works in less than a few minutes

LAN Scanner is available through Docker, which handles the entire startup and maintenance process LAN Orangutan painless process, even if this is your first time running a Docker container. If you’re using a GUI solution like Portainer to manage your self-hosted applications, you can simply install LAN Orangutan through the interface and you’re good to go. If, like me, you want to run LXC in every app, here’s how to do it:
-
Create a Debian LXC.
-
enter LXC shell.
-
Update your system.
apt update && apt upgrade -y -
Installation Docker, certificate serverand cURL.
apt install docker ca-certificates curl -
make APT key directory.
install -m 0755 -d /etc/apt/keyrings -
Add Docker GPG key.
curl -fsSL https://download.docker.com/linux/debian/gpg -o /etc/apt/keyrings/docker.asc -
adjust permissions Docker key file.
chmod a+r /etc/apt/keyrings/docker.asc -
turn on Docker repository.
tee /etc/apt/sources.list.d/docker.sources Types: deb
URIs: https://download.docker.com/linux/debian
Suites: $(. /etc/os-release && echo "$VERSION_CODENAME")
Components: stable
Architectures: $(dpkg --print-architecture)
Signed-By: /etc/apt/keyrings/docker.asc
EOF -
Update the package index.
apt update -
Installation Docker engine.
apt install docker-ce docker-ce-cli containerd.io docker-buildx-plugin docker-compose-plugin -
Make sure it works.
systemctl status docker -
Running LAN Orangutan.
docker run -d \
--name lan-orangutan \
--network host \
--restart unless-stopped \
--cap-add NET_RAW \
--cap-add NET_ADMIN \
--cap-add NET_BIND_SERVICE \
-v lan_orangutan_data:/var/lib/lan-orangutan \
291group/lan-orangutan
The LAN Orangutan listens on port 291, so enter the IP address assigned by the LXC in the browser followed by 291. For me it was 192.168.1.242:291. Interestingly, we need to find the IP address of the network scanner to use the IP address scanner tool. This can be achieved by checking the network configuration in Proxmox for LXC, either in LXC or via the router’s DHCP interface.
Once started, LXC uses only 150 MB of RAM and a fraction of the two vCPU cores assigned. Just north of 1GB of memory is used, so this tool can easily be installed on low-power hardware like a single-board computer (SBC).
It is simple, easy to use and effective
See what’s happening on your local network
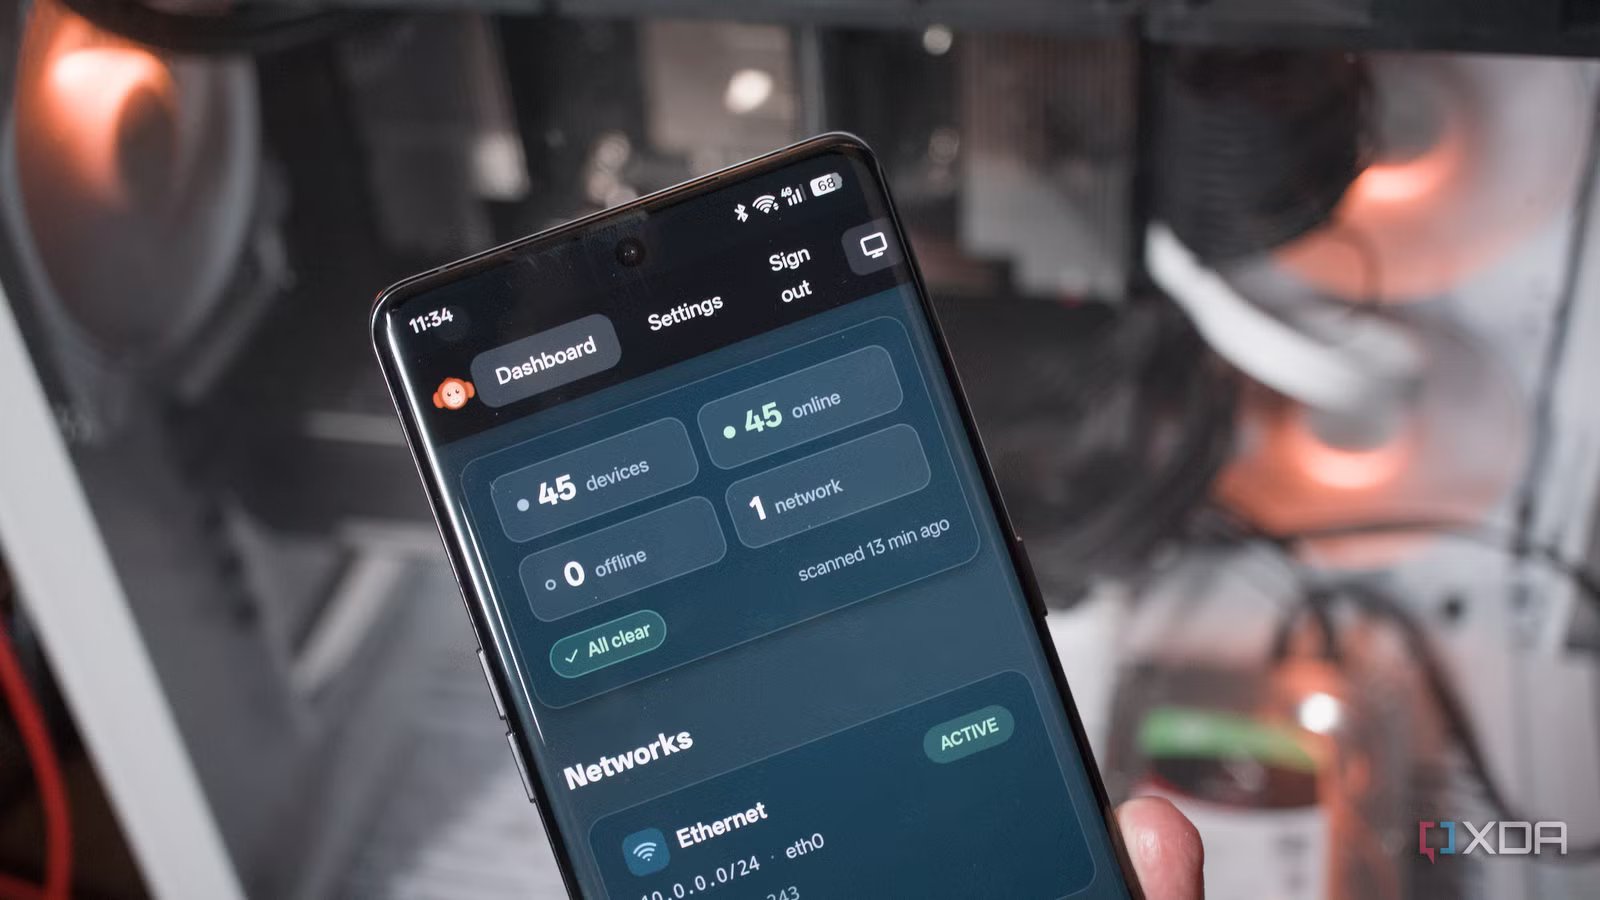
Launching the web interface asks for an administrative password to maintain all security. After that, log in using your password and you will be greeted with a single web page. All LAN Orangutan offers is a basic dashboard showing all networks and identified clients. There’s a settings area and a small popup when editing devices, and that’s about it. The application provides MAC and IP addresses, as well as hostnames and providers where possible.
I tried to do a quick batch using all the defined clients network for all infrastructure equipment and server for self-contained items and home lab equipment. Instead of simply scanning a network and calling it a day (which is possible with a toggle in the dashboard), LAN Orangutan tries to keep a lightweight inventory of all detected networks by default. Interestingly, there is Nmap under the hood, which handles all discovery workloads.
And if you’re the one running and using Tailscale, there’s full support, which is a nice touch.
It is not “drunk” like other tools
LAN Orangutan’s goal is to make networking simple, efficient, and visually appealing. I think the team achieves all three, and this is another great networking tool available for the home lab arsenal. Is it as functional or feature rich as ntopng? Absolutely not, but that’s totally the point. If I want to know something that hasn’t been documented on my LAN yet (QR codes and label maker are perfect for that), I can run this handy tool to check it out.